

The Access token field accepts four kinds of Notion credential: an organization bot token, an internal connection token, a public OAuth access token, or a personal access token. Oleria detects which one you pasted and adjusts what it syncs. Use an organization bot token for full coverage, see Credential coverage.
What Oleria discovers
With an organization bot token, Oleria continuously discovers and maps the following from the connected workspace:- Accounts - workspace members, including name, email, and workspace role (owner, membership admin, member, or restricted member). Owners and membership admins are flagged as administrators.
- Roles - one role per Notion workspace role, with each account linked to the role it holds.
- User groups - permission groups and their direct members, including which members own each group.
- Non-human identities (NHIs):
- Integration bots - internal and public integrations in the workspace.
- Personal access tokens - active, expired, and revoked tokens, with the person who created each token, its creation, expiration, and last-used dates, and who revoked it and when.
- MCP client connections - one entry per MCP client (for example, Claude or ChatGPT), with when it was first connected and last active, linked to every member who connected it.
- Access - each active personal access token is linked to the person it acts as, and each MCP client is linked to every member who authorized it.
Credential coverage
What Oleria can read depends on the credential you connect with. If the credential can’t reach a data type, Oleria skips it and continues syncing everything else, rather than failing the connection. The exception is listing members: if an organization bot token losesuser:read, or an internal connection or public OAuth token loses Read user info (including email), syncs fail until you restore it.
Prerequisites
- For full coverage, a Notion workspace on the Enterprise plan. The Notion Admin API and organization bot tokens are available only on Enterprise.
- An organization owner in Notion to create the organization bot token in organization settings.
- The workspace ID of the workspace you want to connect, see Find the workspace ID.
- Admin access on the Oleria platform to add a new integration.
The exact location of settings in Notion can change over time. If the steps below don’t match what you see, refer to Notion’s own documentation.
Create a credential in Notion
- Option A: Organization bot token (Recommended)
- Option B: Internal connection (any plan)
1
Open admin bots and tokens
Sign in to Notion as an organization owner, open organization settings, and select the Admin bots and tokens tab.
2
Create the bot and token
Create an admin bot with a name your team will recognize, such as
Oleria. Then create a token for the bot and assign the scopes below.Leave out the write scopes for a read-only connection. Notion scopes are independent: a write scope does not grant the matching read scope.
The
user and permission-group scopes are available only to eligible Enterprise organizations. If they don’t appear when you create the token, contact your Notion representative.3
Copy the token
Copy the token immediately and store it securely. You’ll paste it into Oleria in the next section.
Find the workspace ID
An organization bot token can reach every workspace in your organization, so Oleria needs to know which workspace to connect. Internal connections and personal access tokens report their own workspace, so you can leave the field blank for them. In Notion, open Settings and copy the Workspace ID. Depending on your plan, it is at the bottom of the Identity tab or on the General tab. It is a 36-character value such asf0f21888-0225-4b8b-89ff-64c9fa6a114c.
Connect Notion to Oleria
1
Open the integration
Go to your Oleria workspace, select Integrations, then select Notion.
2
Complete the connection form
Fill in the connection form: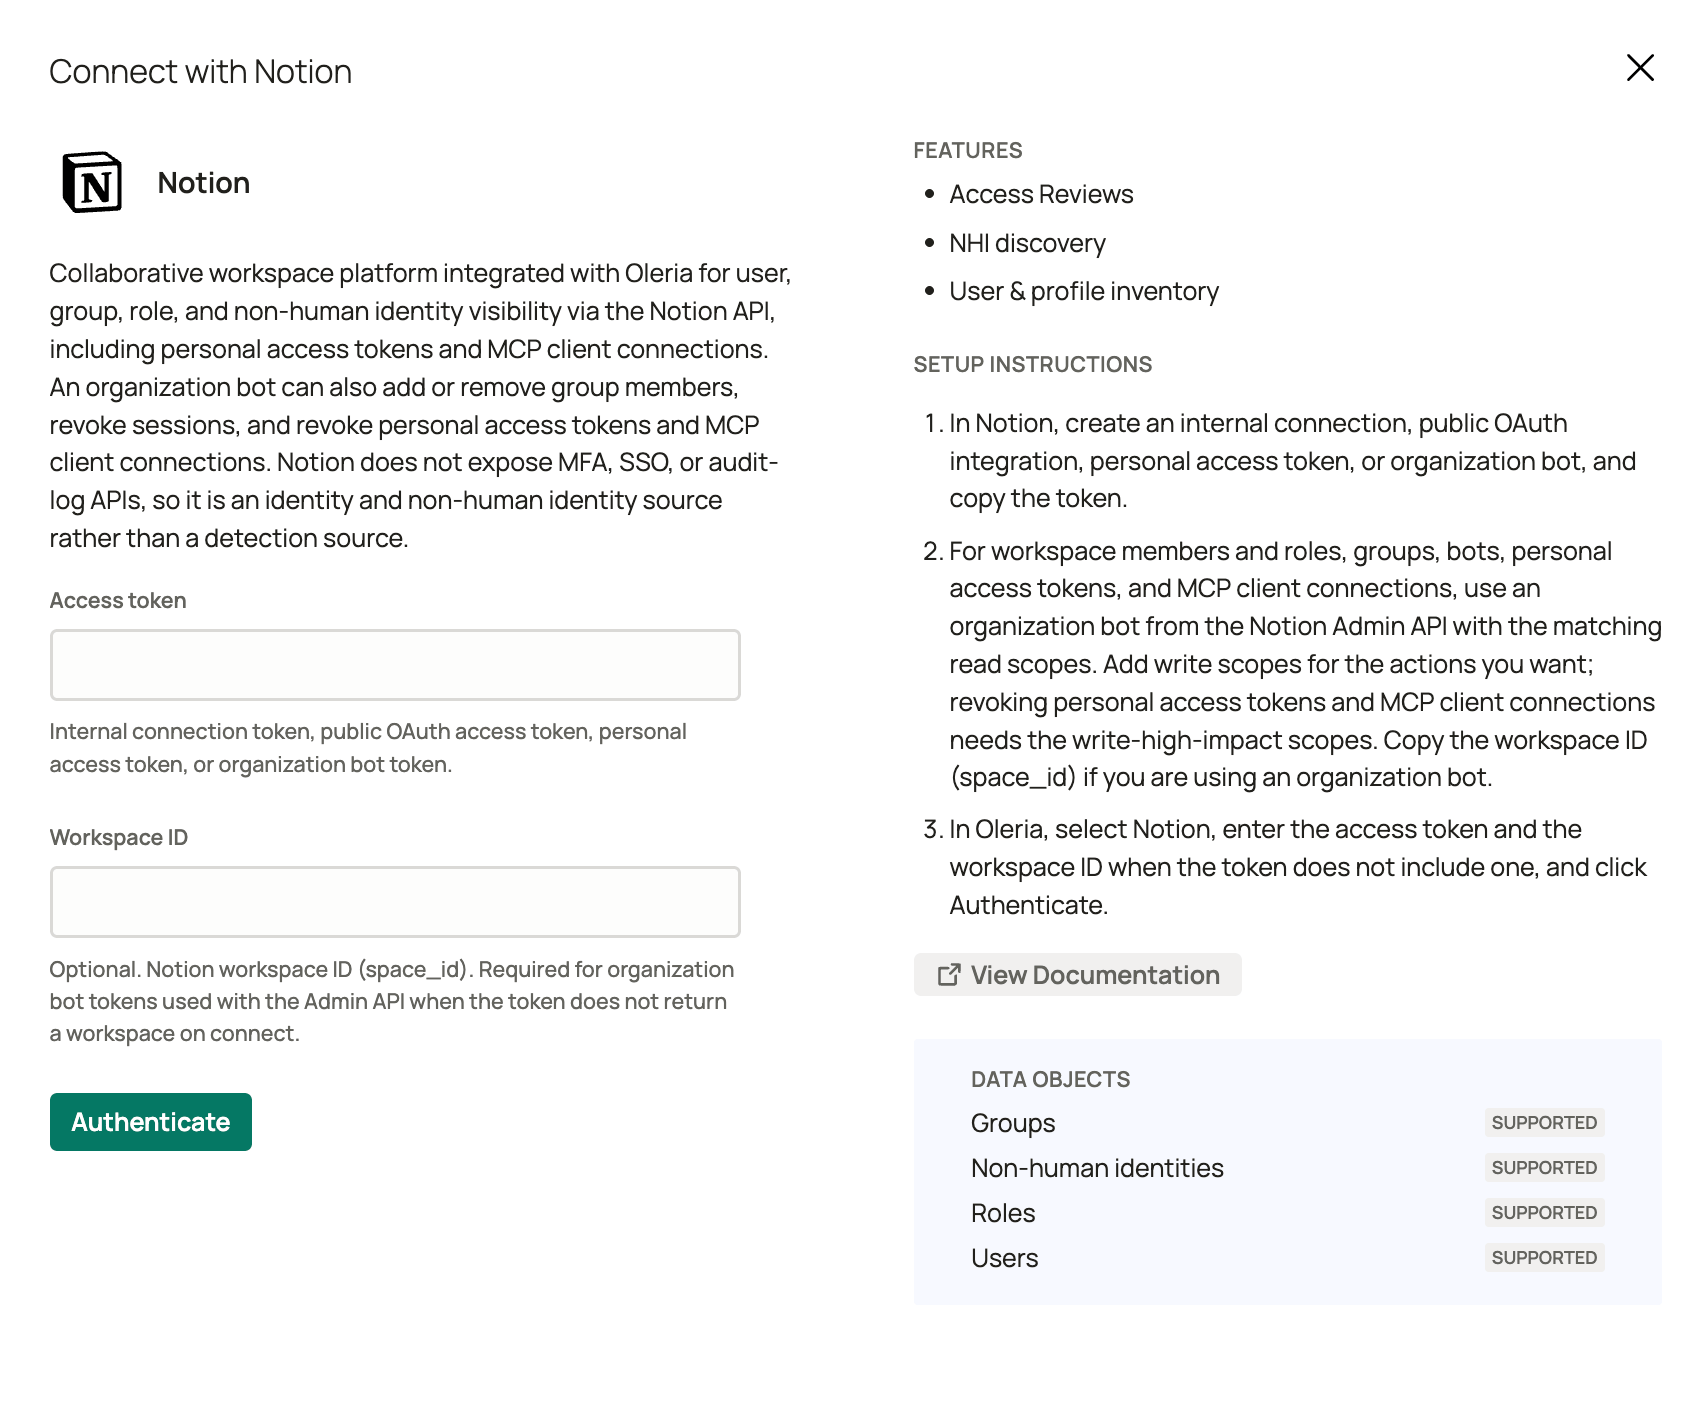
A public OAuth access token comes from your own public Notion integration’s authorization flow. Oleria does not refresh it: if Notion expires it, edit the integration, paste a new token, and select Update. A personal access token is created by a member in their Notion settings, and only shows that token and its creator.
3
Save the integration
Select Authenticate. Oleria checks which kind of credential you pasted and which data it can reach before saving.
Verify the integration
Confirm the new instance appears on the Connected tab of your Oleria Integrations page with a status of Healthy. After the first sync completes, you can review the discovered accounts, workspace roles, permission groups, and NHIs.If you rotate the credential, edit the integration in Oleria, paste the new value, and select Update. The new credential must belong to the same workspace. To connect a different workspace, add a new Notion integration. To switch from an organization bot token to another kind of credential, delete the Notion integration and add a new one. Pasting a different kind of credential with Update makes syncs fail. You can switch to an organization bot token with Update.
Moving from the earlier Notion connection
Earlier Notion connections used SCIM credentials, and they stop syncing until you reconnect them. Edit the existing integration, paste a new access token (and the workspace ID for an organization bot token), and select Update. Your integration history is kept. The earlier SCIM connection could disable and create Notion users. The native integration can’t, because Notion’s Admin API has no endpoint for it (see Known limitations). Before you reconnect, move any workflow or remediation that disables Notion accounts to your identity provider’s Notion SCIM provisioning. You can use Revoke user sessions to sign a user out.Remediation actions
Standard integrations are configured read-only. If you enable remediation for Notion, Oleria uses the same organization bot token. Each action needs the matching write scope from Create a credential in Notion, and Oleria checks for that scope before the action runs.
Disable NHI is one action in Oleria. It’s available only when the token has all of
personal-access-token:read, personal-access-token:write-high-impact, mcp-client-connection:read, and mcp-client-connection:write-high-impact, so you can’t enable personal access token revocation without MCP client revocation. Integration bots can’t be disabled from Oleria.
Groups that your identity provider manages through SCIM can’t be changed from Oleria. Change their membership in your identity provider instead.
Known limitations
- Activity - Notion’s audit log is available only through its SIEM connection, which pushes events. Notion provides no API to read audit events, so Oleria does not sync activity.
- MFA and SSO - Notion does not expose multi-factor authentication or single sign-on status through its API.
- Last sign-in and last password change - available only in Notion’s audit log. Oleria shows last-activity dates for personal access tokens and MCP clients.
- Pages, databases, and teamspaces - content and page-level sharing are out of scope.
- Deprovisioning members - Notion’s Admin API cannot remove or deactivate a workspace member, so Oleria cannot disable a person’s Notion account. Keep offboarding in your identity provider’s Notion SCIM provisioning. Revoking sessions signs a person out but does not remove them.
- Page guests - Notion’s API does not list page guests.
- Nested groups - Notion’s Admin API returns direct group members only.
- Custom agents - not yet shown in Oleria.