Connect Okta to Oleria for single sign-on and user provisioning, covering both the Main Workspace and the Governance App.
This page walks through connecting Okta to Oleria from a blank slate: creating the Okta app, wiring up single sign-on (SSO), and turning on directory provisioning (SCIM), for whichever combination of Main Workspace and Governance App you need. It draws on SSO configuration, SCIM user provisioning, and Governance App SCIM provisioning - see those pages for the full request/response reference and troubleshooting detail; this page focuses on getting from zero to a working Okta connection.
This page is about signing in to Oleria and provisioning Oleria accounts from Okta. It is not the same as the Okta integration under Integrations, which connects Okta as a data source so Oleria can analyze your Okta tenant’s identities and access. That integration does not affect who can sign in to Oleria or how.
Oleria has two independent surfaces, each with its own sign-in and provisioning configuration:
Main Workspace - where administrators, operators, and analysts run Oleria itself: posture, access graph, workflows, and settings.
Governance App - a separate portal where reviewers and approvers complete access reviews, act on access requests, and work governance queues. Governance app users are a distinct population from workspace users, typically much larger (anyone in the org who might approve or review something), and usually don’t need any other access to Oleria.
Each surface has its own tab in Settings → SSO Configuration and its own tab in Settings → SCIM Configuration, with separate identity provider lists, separate SCIM credentials, and separate SCIM base URLs. You can connect Okta to one, the other, or both - they don’t have to match. For example, it’s common to enable SSO and SCIM for the Governance App (so every employee can be provisioned as a reviewer automatically) while managing the smaller set of Main Workspace administrators by hand.
Oleria has three related but independent mechanisms. SSO is for authentication only, where as SCIM and automatic user provisioning are for provisioning.
SSO
SCIM
Automatic user provisioning
Solves
Authentication - how a user proves who they are when signing in
Provisioning - how an Oleria account gets created, updated, and removed
An Oleria setting that creates an account the moment someone signs in and doesn’t already have one
Direction
Okta redirects the user’s browser to Oleria with a signed SAML assertion at sign-in time
Okta’s provisioning engine calls Oleria’s SCIM API directly, independent of anyone signing in
Triggered as a side effect of a successful SAML or social sign-in; nothing is pushed from Okta
Configured where
Settings → SSO Configuration, either tab
Settings → SCIM Configuration, either tab
Settings → SSO Configuration, Governance App tab only
Can deactivate/remove users
No
Yes
No - it only ever creates accounts
Without it
Users sign in with a social login or in rare cases a local account
An administrator adds, updates, and removes users by hand
Because these mechanisms are independent, and each applies per workspace, several combinations are all valid. Pick the one that matches what you’re trying to achieve before you start:
Flow
Main Workspace
Governance App
When to use it
SSO + SCIM (recommended)
Okta SAML + SCIM
Okta SAML + SCIM
Full end-to-end: Okta group membership determines who has an Oleria account and what role they hold, and the same Okta credentials sign them in, including automatic deactivation when someone is unassigned. This is what the rest of this page sets up.
SSO only
Okta SAML
Okta SAML
Small, stable user list you’re comfortable adding by hand in Manage Users, but want Okta credentials for sign-in. Apply to either tab independently, or both.
SCIM only
Okta SCIM
Okta SCIM
Users should come from Okta automatically, but you’re not ready to move sign-in off social login yet. Apply to either workspace independently, or both.
SSO + automatic user provisioning
N/A - Governance App only
Okta SAML + Oleria’s automatic user provisioning toggle
Lighter-weight than SCIM - no provisioning connector to build in Okta, accounts just appear the first time someone signs in - but there’s no automatic deprovisioning, and it’s gated only by email domain, not Okta group/app assignment. Good for “let anyone at the company become a reviewer” without building a directory sync.
Split by surface
Manual, or a different IdP
Okta SAML + SCIM
Common when only the Governance App needs to reach a broad, automatically-provisioned population (for example, every employee as a potential reviewer), while a small workspace admin team is managed separately
This page sets up the recommended SSO + SCIM flow, one workspace at a time. If you’d rather use automatic user provisioning instead of SCIM for the Governance App, see the note at the end of Part 2.
Okta super admin access - Okta’s own guidance for enabling SCIM on a custom app is to sign in as a super admin, and lesser admin roles may not see the setting.
Decide which workspaces - Main Workspace, Governance App, or both - you’re connecting Okta to, and whether you want SSO, SCIM, or both for each. See Possible provisioning flows above.
For SCIM only: your Okta org must have Okta Lifecycle Management (LCM) entitlements. LCM is a separate Okta product from SSO, and without it the Provisioning setting never appears on the app. Check this before you start - it’s the most common reason this setup can’t be completed. See Okta Lifecycle Management is required for SCIM below. SSO (Part 1) does not require LCM.
For SCIM into the Main Workspace: know which Oleria roles (admin, operator, analyst, governance-operator, identity-lifecycle-operator) your Okta groups should map to. See How Oleria maps roles and groups.
In Oleria, go to Settings → SSO Configuration, select the Main Workspace or Governance App tab depending on which application you’re connecting first, and click Add IdP in the SAML IdP card.
2
Create the Okta app
In the Okta Admin Console, go to Applications → Applications → Create App Integration, select Classic experience since Integration Wizard is not supported at this time. Select SAML 2.0, and name it something that identifies which Oleria workspace it’s for (for example Oleria - Main Workspace or Oleria - Governance App) - this matters once you’ve done this twice for both workspaces.
3
Copy Oleria's SP details into Okta
On Oleria’s Oleria details step, copy the Entity ID and ACS URL. On Okta’s Configure SAML step, enter them as the Audience URI (SP Entity ID) and Single sign-on URL. Copy or download the Request signing certificate shown on Oleria’s Oleria details step - you’ll need it later in this Part if you turn on Sign requests.
4
Configure the NameID
Still on Configure SAML, set Name ID format to Persistent and Application username to Email.
Application username is also the value Okta sends as userName when you add SCIM in Part 2, so leave it on Email rather than Okta username or a custom expression. Oleria identifies an account by one email address, and Okta’s matching queries look that address up by userName. If Application username resolves to something other than the user’s email - a user.login on a different domain, say - then userName and the provisioned emails value disagree, Okta can’t find the account it created, and it retries the create on every sync. Keep Application username, the app’s email attribute mapping, and the email attribute statement in the next step all pointing at the user’s email.
5
Add the required attribute statements
This step is on a different page than the previous one for most Okta orgs today. On Okta Identity Engine (OIE) orgs - the default for new orgs - Attribute Statements aren’t part of the Configure SAML page at all; add them afterward on the app’s Sign On tab, under Attribute Statements. Only on legacy Okta Classic Engine orgs do they appear further down the same Configure SAML page.
Add an attribute statement Nameemail, Name formatUnspecified, Valueuser.profile.email, and a second Namename, Name formatUnspecified, Valueuser.profile.firstName + " " + user.profile.lastName.See Connect a SAML identity provider for why each of these is required.
6
Assign users
Assign the app to the users or groups who should be able to sign in to Oleria.
7
Enter the SAML IdP details in Oleria
On the Sign On tab copy the Identity Provider metadata URL.
Back in Oleria, complete the SAML IdP details step: give the identity provider a Name, paste the Okta metadata URL into Metadata, and decide whether to turn on Sign requests and/or Encrypt SAML responses. Click Add identity provider.
8
If you turned on Sign requests: upload the request signing certificate to Okta
Skip this step if you left Sign requests off. Otherwise, go back to the Okta app’s General tab, open SAML Settings → Edit, and click Show Advanced Settings. Upload Oleria’s Request signing certificate (downloaded in pem format earlier in this Part) next to Signature Certificate, then set Signed Requests to Validate SAML requests with signature certificates.
9
If you turned on Encrypt SAML responses: download and upload the response encryption certificate
Skip this step if you left Encrypt SAML responses off. Otherwise, back in Oleria you’ll see a prompt to download the Response encryption certificate generated specifically for this identity provider - download it in pem format. In Okta, in that same Show Advanced Settings view, set Assertion Encryption to Encrypted and upload the certificate next to Encryption Certificate.Before:After:
10
Confirm sign-in works
Sign out of Oleria, go to https://www.oleria.com/sign-in, select the new identity provider, and confirm you land back in Oleria signed in.
You can add SCIM provisioning to the same Okta app you just created for SSO - Okta supports provisioning on custom SAML apps once you turn it on, provided your org is licensed for it.
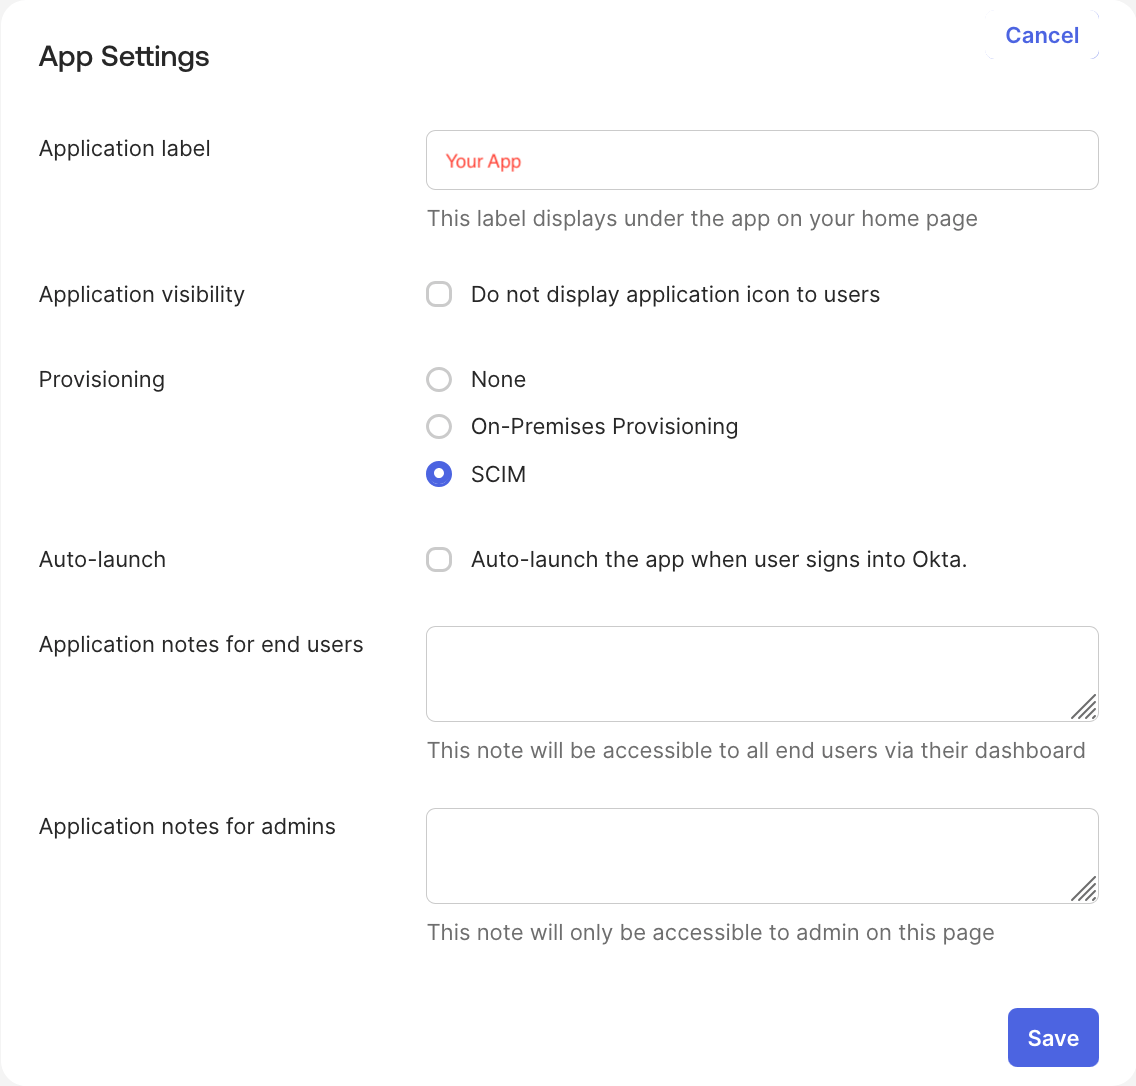
Outbound SCIM provisioning is part of Okta Lifecycle Management (LCM), a separate Okta product from SSO. If your org isn’t entitled to LCM, the Provisioning setting simply isn’t rendered: the App Settings dialog shows only Application label, Application visibility, Auto-launch, and the two notes fields, with no Provisioning options to select. Nothing is greyed out, so it reads as though the setting doesn’t exist.LCM is included in Okta’s Essentials, Professional, and Enterprise suites and in the Okta Identity Governance add-on. It is not included in the Starter or Core Essentials plans, where it’s a paid add-on.Quickest way to check: in the Okta Admin Console, look at any other app in your org that should provision users (for example a directory app like Google Workspace). If no app in the org has a working Provisioning tab, your org doesn’t have LCM. Your Okta account team can confirm whether it’s in your contract or needs to be added.If you can’t add LCM, Oleria still has working options - see Alternatives without Lifecycle Management.
1
Enable provisioning on the Okta app
Open the same Okta app from Part 1. On the General tab, click Edit next to App Settings, then set Provisioning to SCIM - some Okta orgs show this as a Enable SCIM provisioning checkbox instead of a radio group - and click Save. A new Provisioning tab appears on the app.
No Provisioning setting in the dialog? The most likely cause is that your org isn’t entitled to LCM, as described above. Two other causes: the app is an OIDC integration rather than SAML 2.0 or SWA (Okta doesn’t support SCIM on custom OIDC apps created in the Classic experience), or the app was created through the Okta API or Terraform rather than the Admin Console, which can leave the provisioning options absent or unconfigurable. If the app is a SAML 2.0 app created in the Admin Console and your org does have LCM, contact Okta Support to check whether the provisioning feature needs activating for your org.
2
Get Oleria's SCIM credentials
In Oleria, go to Settings → SCIM Configuration and select the same workspace you used in Part 1 (Main Workspace or Governance App). Copy the SCIM Base URL, Client ID, Client Secret, and OAuth Token URL.
3
Configure the API integration
On the Okta app’s Provisioning tab, select Integration, click Edit. Enter Oleria’s SCIM Base URL as the SCIM connector base URL, for unique identifier enter userName, and check Push New Users, Push Profile Updates, and Push Groups.
Set Authentication Mode to OAuth 2, under OAuth 2 set Grant Type to Client Credentials, and enter Oleria’s OAuth Token URL as the access token endpoint along with the Client ID and Client Secret you copied.
Oleria’s SCIM API only issues short-lived tokens through this client credentials exchange - it does not accept a single, static, long-lived bearer token. Use OAuth 2 / Client Credentials here, not the HTTP Header (bearer token) authentication mode. Okta mints and automatically refreshes its own token from the Client ID and Client Secret, so there’s nothing to manually re-enter later. See Authenticate to the SCIM API for how this same OAuth 2.0 Client Credentials flow works if you’re ever calling the API directly instead of through Okta.
4
Turn on the provisioning actions you need
Under Provisioning → To App, click Edit and enable Create Users, Update User Attributes, and Deactivate Users.
5
Confirm userName and email carry the same address
Still under Provisioning → To App, scroll to Oleria Attribute Mappings and confirm the app’s email attribute maps to Okta’s user.email, which is the default. Combined with Application username set to Email in Part 1, that makes userName and emails carry the same address - which is what Oleria stores and what Okta’s matching queries search on.Okta requires an email on every user, so there’s no fallback to configure here. The two ways this drifts are changing Application username away from Email, and remapping email to something other than user.email; either one leaves the two values disagreeing for some users, which shows up as repeated create attempts for users who already exist in Oleria.
6
Main Workspace only: push groups from Okta
Main Workspace only: Oleria grants roles through group membership, not directly on the user (see How Oleria maps roles and groups).Governance App: there is no group-to-role mapping to configure - every provisioned user is assigned the single reviewer role automatically. You only need users pushed, not groups.
In Okta, go to the app’s Push Groups tab and push each Okta group whose members should get Oleria access. Okta then creates the matching group in Oleria automatically via SCIM, with membership synced, but without a role set. Okta’s Push Groups doesn’t support mapping a role or any other custom attribute onto the group it creates, so a newly-created group falls back to Oleria’s read-only analyst role until you assign it a different one in the next step.
7
Main Workspace only: assign each group a role in Oleria
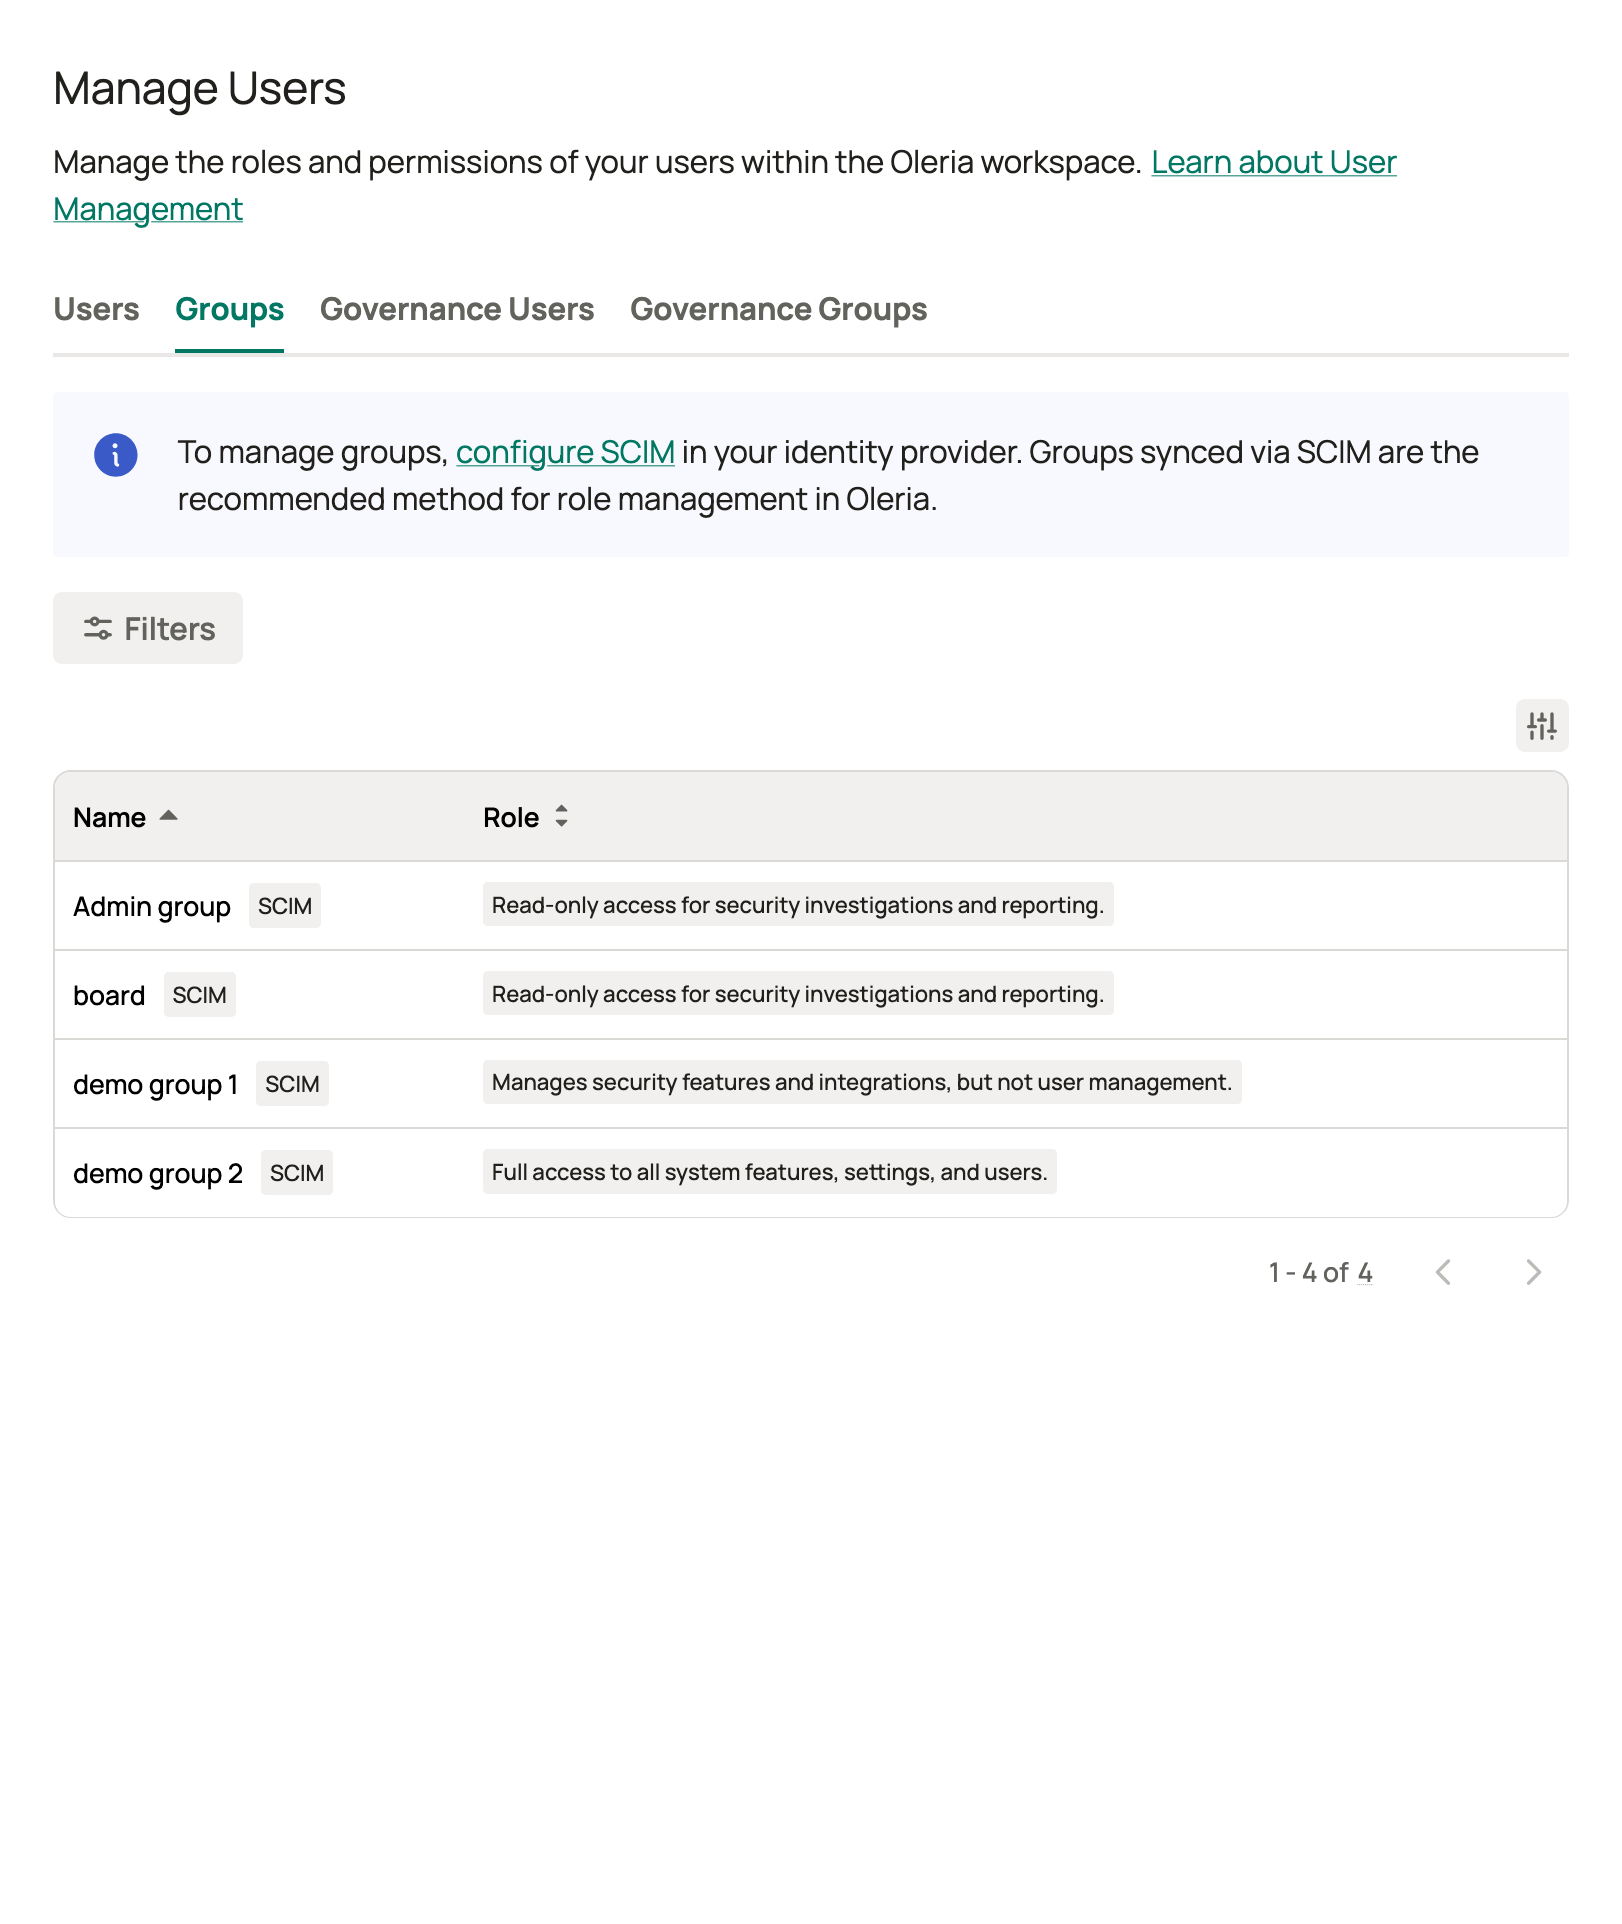
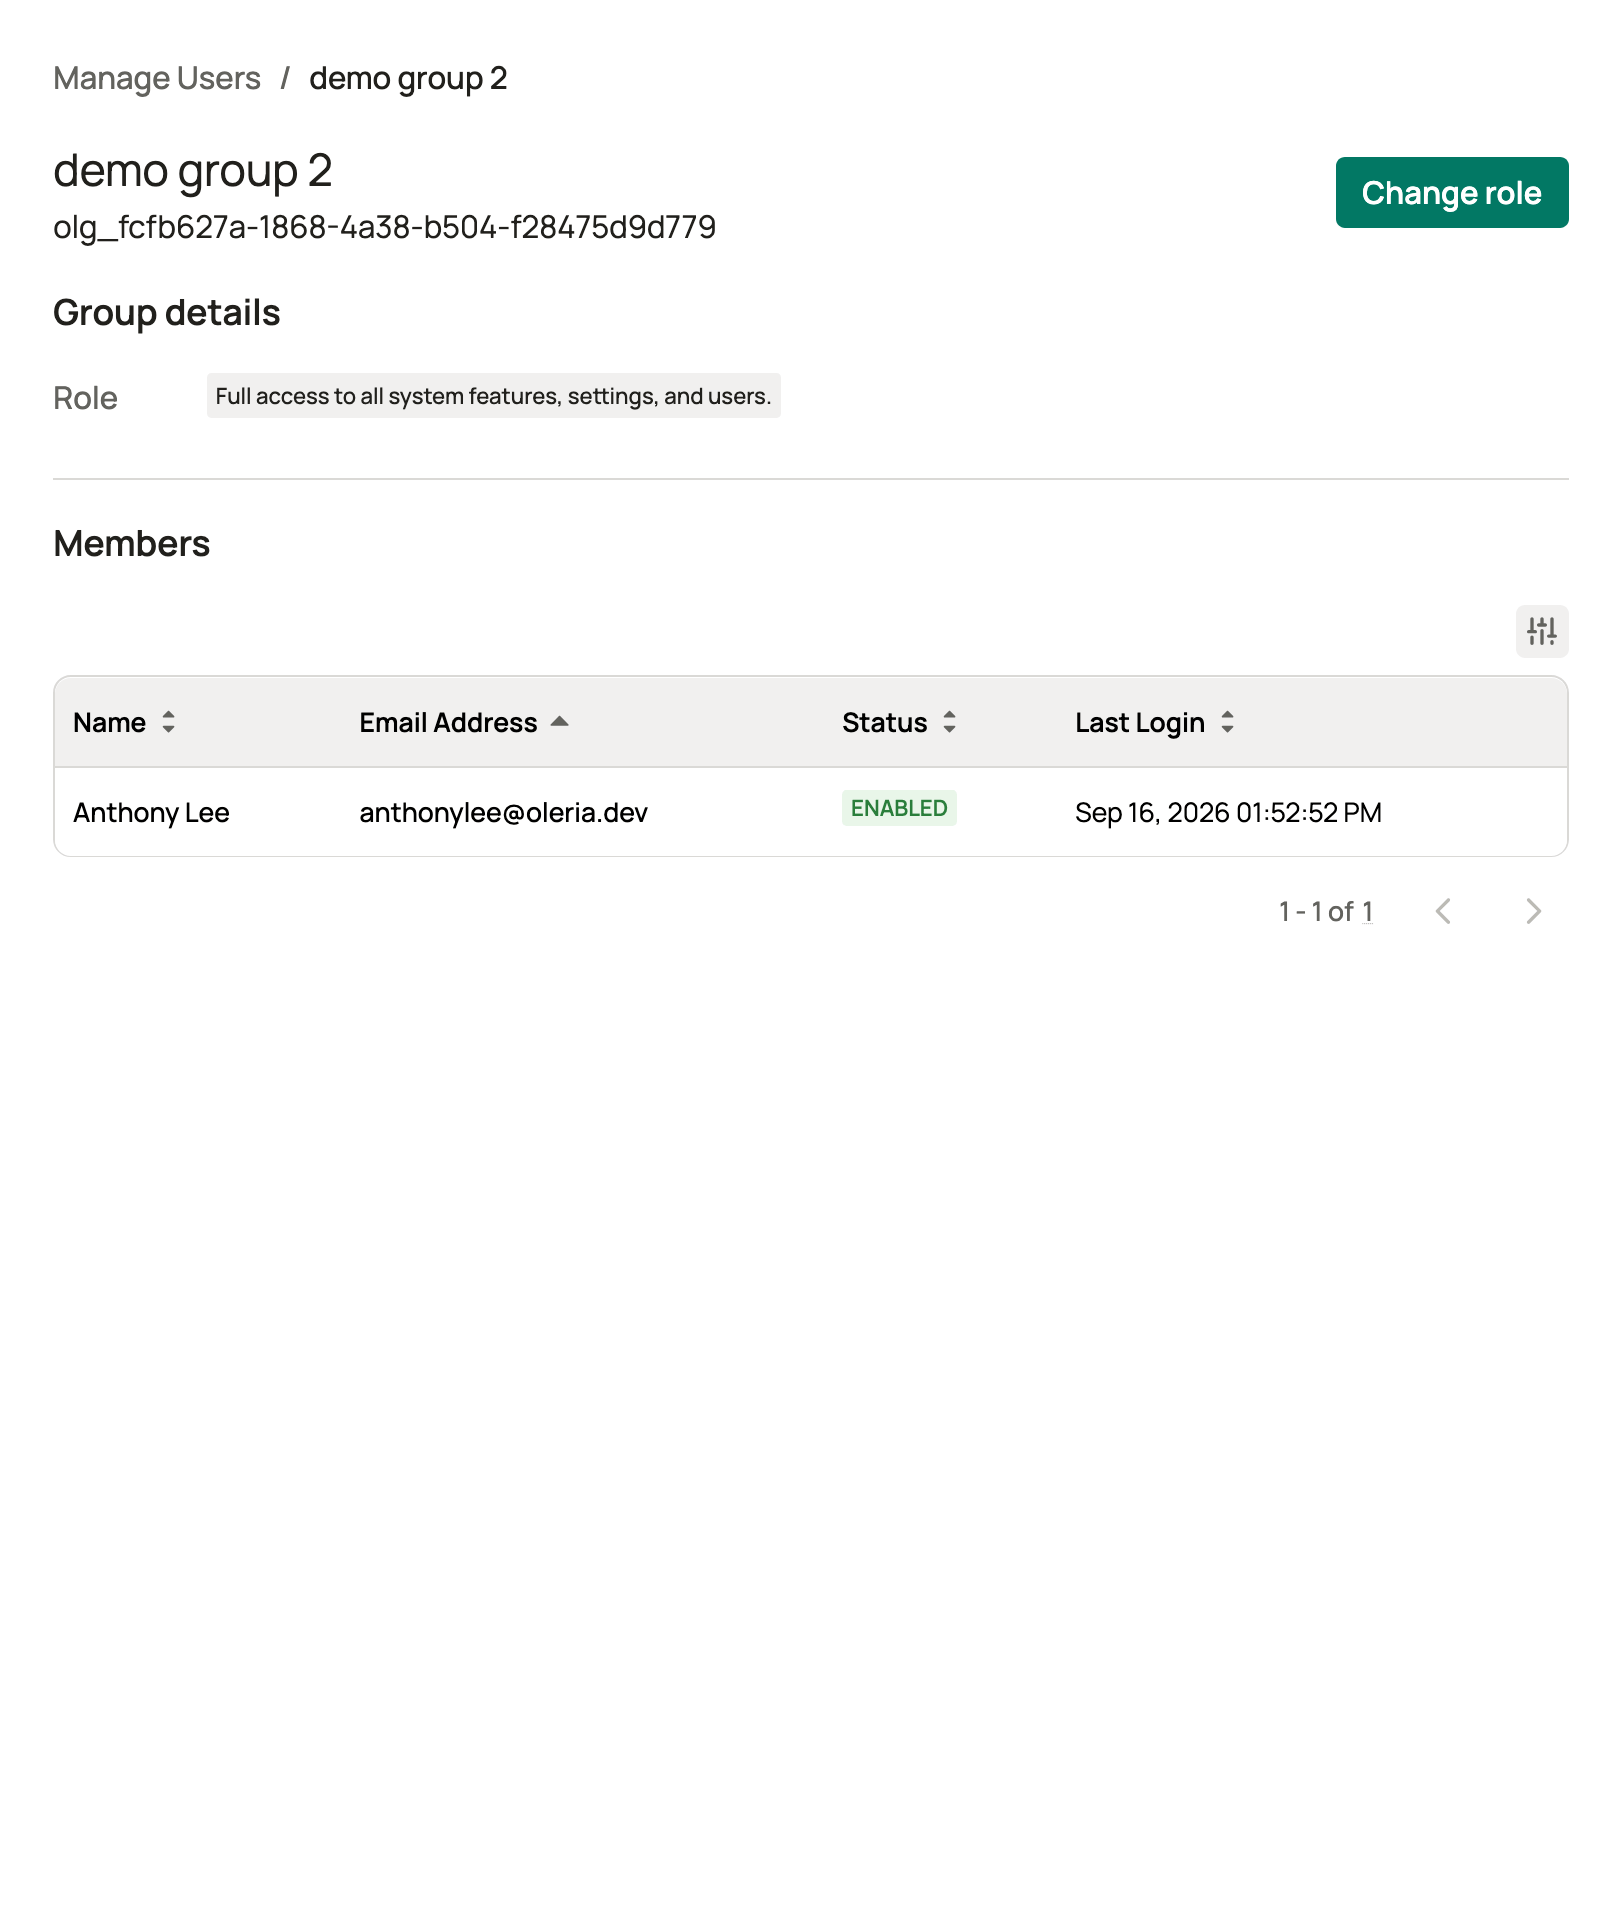
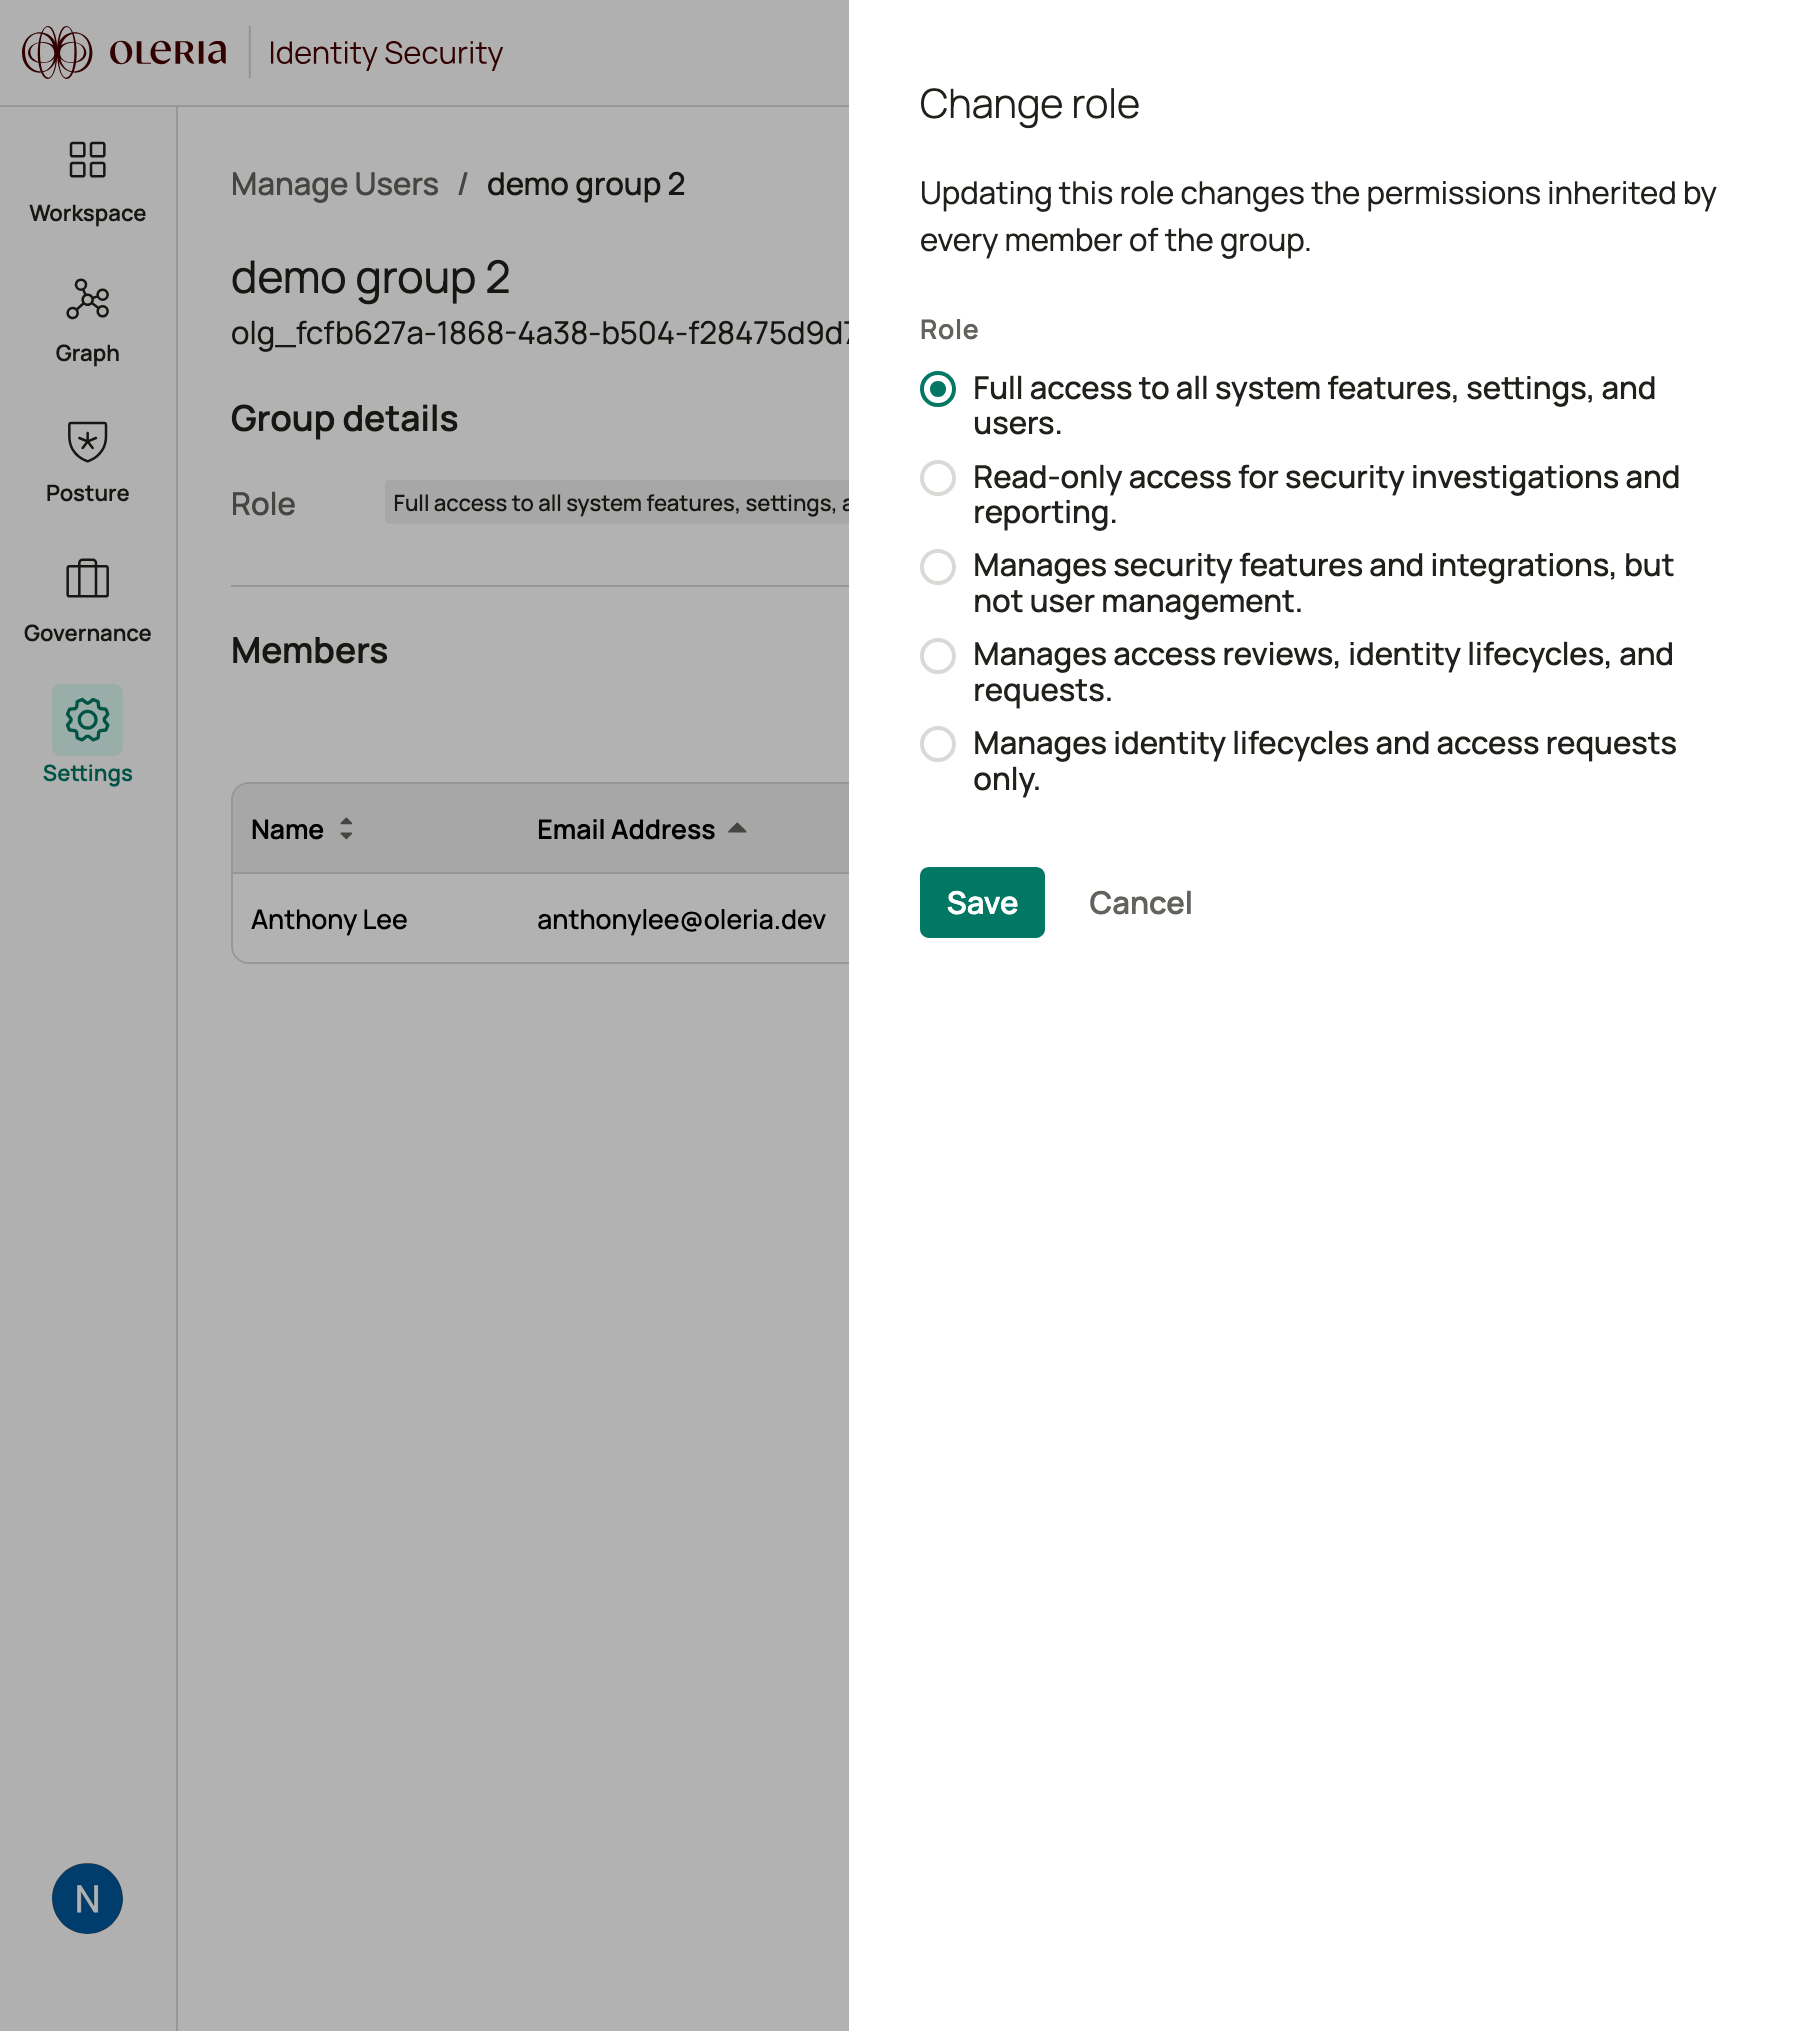
In Oleria, under Settings open Manage Users, select the Groups tab, and for each group you push, select it, click Change role, choose the role it should map to, and click Save. Every current and future member of the group inherits that role. See Assign a role to a group for the full walkthrough.Oleria’s Manage Users page:The detail page for a particular group:Changing the role mapping for that group:
8
Assign and provision
Assign the users or groups who should get Oleria accounts to the app (Main Workspace: via the groups you just pushed; Governance App: directly, or via any group). Okta provisions matching users into Oleria within its usual sync interval.
9
Verify
In Oleria, confirm the new users appear (Main Workspace: in Manage Users with the expected role; Governance App: in the governance reviewer list). Deactivate or unassign a test user in Okta and confirm they lose access in Oleria.
Alternative for the Governance App: if you don’t need directory-driven deprovisioning and don’t want to build the Okta provisioning connector above, you can skip this Part entirely and use Oleria’s built-in automatic user provisioning instead - it only requires SSO (Part 1) to already be working. Follow Automatically provision reviewers to enable it and set allowed email domains. Remember this is not SCIM: it only creates accounts on sign-in and never deactivates them, so it’s not a substitute for SCIM if you need automatic offboarding.
If your Okta org isn’t entitled to LCM and adding it isn’t an option, you can still get most of the way there. What’s available depends on which workspace you’re provisioning.
There is no way to work around the LCM requirement from inside Okta. In particular, adding one of the generic SCIM 2.0 Test App integrations from the Okta Integration Network doesn’t help: LCM gates the Provisioning tab on catalog apps exactly as it does on custom apps, and those test apps authenticate with a static bearer token or basic auth rather than the OAuth 2.0 Client Credentials flow Oleria’s SCIM API expects. Okta Workflows is not a workaround either - it’s licensed as part of Lifecycle Management and Okta Identity Governance.
Option
Applies to
What you get
What you give up
Automatic user provisioning (recommended for reviewers)
Governance App only
Accounts are created the first time someone signs in through Okta SSO, with no provisioning connector in Okta at all. Only Part 1 is required. See Automatically provision reviewers.
No deprovisioning - accounts are never deactivated automatically. Scoped by email domain rather than by Okta group or app assignment.
Manage users by hand
Main Workspace, Governance App
Full control over roles with no IdP-side setup. Practical for the small workspace admin population. See Manage Users.
Every join, role change, and departure is a manual step in Oleria.
Drive Oleria’s SCIM API directly
Main Workspace, Governance App
Oleria’s SCIM endpoints are standard SCIM 2.0 and don’t care what calls them. A script or integration platform can read group membership from Okta’s own Users and Groups API - available to every Okta org, no LCM needed - and create, update, and deactivate the matching Oleria users and groups. See SCIM user provisioning.
You own the sync logic, scheduling, and error handling that Okta’s provisioning engine would otherwise provide.
A common split is automatic user provisioning for the Governance App reviewer population plus hand-managed Main Workspace admins - that combination needs only SSO, and no LCM.
Okta has no restriction on reusing the same Audience URI (SP Entity ID) or SCIM base URL pattern across multiple apps, so connecting the second workspace is simply repeating Part 1 and Part 2 with a second, separately-named Okta app pointed at the second workspace’s Oleria details and SCIM credentials. You do not need to reuse or share anything between the two Okta apps.
Okta is a cloud identity service. It holds your organization’s user accounts and groups, and it’s what your people authenticate against when they open the Okta dashboard or any application your organization has connected to it.Connecting it to Oleria means those same work accounts sign in to Oleria, and, once SCIM is on, that Okta decides who has an Oleria account at all.Where those accounts originate doesn’t matter to Oleria. Okta’s Universal Directory may hold them natively, or they may be synced in from on-premises Active Directory or an HR system. Oleria only ever talks to Okta, so the accounts, groups, and attributes it sees are the ones that exist in Okta.
What is an identity provider, and what is a service provider?
An identity provider (IdP) is the system that holds user accounts and vouches for who someone is. A service provider (SP) is the application the person is trying to reach, which trusts the identity provider instead of storing passwords itself. In this setup, Okta is the identity provider and Oleria is the service provider.A SAML sign-in runs like this:
The user opens Oleria’s sign-in page and selects your identity provider.
Oleria redirects their browser to Okta, which authenticates them with whatever your org requires (password, MFA, sign-on policies).
Okta sends the browser back to Oleria’s ACS URL carrying a digitally signed SAML assertion that says who the user is.
Oleria checks the signature against the certificate in the metadata you gave it, and signs the user in.
Oleria never sees the user’s Okta password, and it can’t sign anyone in that Okta hasn’t vouched for.
What are the Entity ID and ACS URL Oleria gives me?
They are Oleria’s two identifiers in the SAML handshake, and you paste both into Okta’s Configure SAML step:
Entity ID (Okta calls it Audience URI (SP Entity ID)) - the unique name of Oleria as a service provider. It’s a name, not a page you can open. Okta includes it in the assertion so Oleria can confirm the assertion was meant for it.
ACS URL (Okta calls it Single sign-on URL) - the Assertion Consumer Service URL, the exact address Okta posts the signed assertion to. It has to match character for character.
Where is the Okta Admin Console, and what is an org?
Your org is your organization’s own instance of Okta: your users, your groups, your applications. It has a URL like https://acme.okta.com, which is where end users land, and an Admin Console at https://acme-admin.okta.com. From the end-user dashboard you can also reach it with the Admin button. Everything on this page happens in the Admin Console, under Applications → Applications.Many organizations also have a preview org, usually https://acme.oktapreview.com, that mirrors production. It’s a good place to walk through this setup once before doing it for real, as long as you point it at a matching Oleria workspace.
What is an app integration, and why create a custom one?
An app integration is the object in your org that represents an outside application your people use, along with the settings for how sign-in and provisioning work with it. Creating one doesn’t install anything; it records that your org trusts that application and who is allowed to use it.The Okta Integration Network (OIN) is Okta’s catalog of applications with the SAML and SCIM fields pre-filled. Oleria isn’t in the OIN, so you create a custom SAML 2.0 app integration and fill in the URLs and attribute statements yourself, which is what Part 1 walks through.When Okta offers a choice between the Integration Wizard and the Classic experience while creating it, choose Classic experience. The Integration Wizard is not supported for this setup at this time.
What are Okta Identity Engine and Classic Engine, and which am I on?
They are two generations of Okta’s underlying authentication engine. Identity Engine (OIE) is the default for new orgs and for most orgs today; Classic Engine is the older one some long-standing orgs still run.It matters here for one reason: on Identity Engine, attribute statements aren’t part of the Configure SAML page, and you add them afterward on the app’s Sign On tab under Attribute Statements. On Classic Engine they appear further down the Configure SAML page itself. Same result, different page.To check which you’re on, look at the Okta version number in the Admin Console footer. A version ending in E, such as 2026.02.0 E, means Identity Engine.
What are attribute statements, and what is the NameID?
An attribute statement is one fact about the signed-in user that Okta includes in the SAML assertion. Oleria needs three things in total:
Name ID format set to Persistent. Application username decides what value goes into it; this setup uses Email.
Two attribute statements named exactly email and name, both with Name formatUnspecified. Unspecified is what keeps the names arriving as plain email and name rather than wrapped in a namespace URI, which is what Oleria looks for.
If any of the three is missing or shaped differently, Oleria rejects the sign-in.
What Okta admin role do I need to do this?
Use a super admin account. Okta’s own guidance for enabling SCIM provisioning on a custom app is to sign in as a super admin, and narrower roles such as application administrator may not render the Provisioning setting at all, which looks identical to not being licensed for it.If a section described here is missing or read-only for you, check the admin role you signed in with before assuming it’s a licensing problem, then check Okta Lifecycle Management is required for SCIM.
How do I tell whether we have Lifecycle Management?
Outbound SCIM provisioning is part of Okta Lifecycle Management (LCM), which is licensed separately from SSO. The quickest check is to open any other app in your org that provisions users, such as a directory app, and look for a working Provisioning tab. If no app in the org has one, your org doesn’t have LCM.Okta Lifecycle Management is required for SCIM covers which Okta plans include it, and Alternatives without Lifecycle Management covers what to do if adding it isn’t an option. SSO in Part 1 needs no LCM.
What's the difference between assigning a user and provisioning a user?
Assignment, on the app’s Assignments tab, controls who is allowed to use the app: who can sign in through it, and, once provisioning is on, who Okta pushes to Oleria.With SSO alone, assignment creates nothing in Oleria. An assigned user who has no Oleria account can complete the Okta half of the sign-in and still be denied, until an account exists for them through SCIM, automatic user provisioning, or Manage Users. With SCIM and Create Users enabled, assigning someone is what triggers Okta to create their Oleria account.
How quickly does Okta push changes to Oleria?
Outbound provisioning is event-driven rather than scheduled. When you assign someone, change their profile, or deactivate them, Okta pushes that change to Oleria as it happens, usually within a minute or two, and retries on failure. There’s no sync cycle to wait for the way there is with a scheduled directory import.Group membership is the exception worth knowing: use Push now on the app’s Push Groups tab to force a group and its membership through immediately instead of waiting for the next change to trigger it.
Where does Okta log what happened?
Two places, and picking the right one saves time:
Reports → System Log for everything. Filter by the Oleria app to see both sign-in events and provisioning events, including the error Oleria returned when it refused a SCIM request.
The Admin Console’s Tasks page, where Okta collects provisioning actions that failed and need attention, so a broken push doesn’t only live in the log.
Okta’s log is almost always more specific about a SAML failure than what the user sees in the browser. Check it first when a sign-in doesn’t work.
Does connecting Okta to Oleria change anything in my Okta org?
No. Provisioning is a one-way push from Okta into Oleria: Okta creates, updates, and deactivates Oleria accounts, and Oleria never writes back into your directory. SSO doesn’t change how anyone authenticates to Okta; it only lets Oleria accept the result.Deleting the app integration later stops both sign-in and provisioning. It doesn’t remove the Oleria accounts that already exist, so remove those in Manage Users if you need them gone.This is also why the Okta integration under Integrations is a separate thing: that one reads your org so Oleria can analyze it, and it has no bearing on who can sign in.
Okta says the user isn't assigned to this application
The person isn’t assigned to the app integration. Open the app’s Assignments tab and add them, or add a group they belong to. Okta blocks everyone else by design, which is what makes assignment your access control for Oleria sign-in.
Okta reports a SAML error about the destination or audience
The Single sign-on URL or Audience URI (SP Entity ID) in Okta doesn’t exactly match Oleria’s ACS URL and Entity ID. Trailing slashes, http instead of https, and a truncated paste all count as a mismatch. Re-copy both values from Settings → SSO Configuration in Oleria and paste them again on the app’s Configure SAML step.
Okta signs the user in, then Oleria rejects them
Authentication succeeded and the content of the assertion is the problem. Check, in this order:
Name ID format is Persistent, with Application username set to Email.
Attribute statements named exactly email and name exist, both with Name formatUnspecified.
If you turned on Sign requests, Oleria’s request signing certificate is uploaded to Okta under Signature Certificate, and Signed Requests is set to Validate SAML requests with signature certificates.
If you turned on Encrypt SAML responses, Assertion Encryption is set to Encrypted and Oleria’s response encryption certificate is uploaded next to Encryption Certificate.
I can't find Attribute Statements on the Configure SAML page
Your org is on Okta Identity Engine, where attribute statements live on the app’s Sign On tab under Attribute Statements rather than on Configure SAML. Finish the SAML configuration, then add them there. Only legacy Classic Engine orgs show them on the Configure SAML page.
The user signs in successfully but has no access to Oleria
Sign-in worked and the person has no Oleria account, or has one that’s been deactivated. SSO authenticates people; it never creates accounts. Depending on the workspace:
Main Workspace - the account has to come from SCIM or from Manage Users.
Governance App - the same, unless you turn on automatic user provisioning and add the person’s email domain to the allowed list.
Sign-in worked for months and suddenly stopped
If you pasted metadata XML instead of a URL when you first set the identity provider up, then the certificate provided in the metadata may have expired or been rotated. The XML is a snapshot rather than a live document, so changes to it are not captured by Oleria automatically.
Get fresh metadata from the app’s Sign On tab, then open the provider in Settings → SSO Configuration, edit it, and save the Identity Provider metadata XML again.
The user signs in but lands on a different account than SCIM provisioned
The SAML email attribute statement resolves to a different address than the one SCIM provisioned, so Oleria can’t match the sign-in to the existing account. All three have to point at the same address: the email attribute statement on the Sign On tab, Application username, and the app’s email attribute mapping under Provisioning → To App. See Confirm userName and email carry the same address.
Oleria rejects the identity provider when I add or edit it
This is an Oleria-side validation failure rather than an Okta problem: the metadata URL is unreachable, the name is already taken, or the metadata XML is incomplete. Oleria names the specific reason in the error it shows. See Troubleshoot identity provider errors for every message and what to do about each.
How should I test sign-in?
Two Okta tools are useful while you configure: Preview the SAML Assertion on the Configure SAML step shows the exact assertion Okta will send, which is the fastest way to confirm the NameID format and the email and name attribute names without signing anyone in. The System Log shows what Okta thought happened on a real attempt.Treat signing in at https://www.oleria.com/sign-in as the real test, because that’s the service-provider-initiated flow your users actually take. Launching the app from the Okta dashboard tile is a different, identity-provider-initiated flow.
In most cases your org isn’t entitled to Okta Lifecycle Management, and Okta renders no Provisioning options at all rather than greying them out. See Okta Lifecycle Management is required for SCIM, and Alternatives without Lifecycle Management if you can’t add it.Two other causes worth ruling out: you’re signed in with an admin role narrower than super admin, or the app was created through the Okta API or Terraform rather than the Admin Console, which can leave the provisioning options absent.
Test API Credentials fails
Work through the integration fields in order:
SCIM connector base URL is Oleria’s SCIM Base URL, not Oleria’s sign-in address.
Unique identifier is userName.
Authentication Mode is OAuth 2 with Grant Type set to Client Credentials, not HTTP Header. Oleria’s SCIM API only issues short-lived tokens through this exchange and never accepts a static bearer token.
The access token endpoint is Oleria’s OAuth Token URL.
Client ID and Client Secret are pasted whole, with no leading or trailing spaces.
Confirm you copied all four values from the correct tab of Settings → SCIM Configuration. The Main Workspace and Governance App have separate credentials and separate base URLs, and using one workspace’s secret against the other’s URL fails here.
Provisioning is configured but nobody appears in Oleria
In rough order of likelihood:
Create Users isn’t enabled under Provisioning → To App. Turning on SCIM doesn’t enable the individual provisioning actions.
Nobody is assigned to the app on the Assignments tab.
You pushed a group under Push Groups but never assigned it. Pushing a group creates the group in Oleria; assignment is what provisions the people in it. They’re separate actions on separate tabs.
The push failed and is waiting in the Admin Console’s Tasks page, or recorded as an error in Reports → System Log.
Users sync but groups don't (Main Workspace)
Three causes, all common:
Push Groups wasn’t checked in the app’s Provisioning → Integration settings, so Okta never pushes groups at all.
The group hasn’t been added on the Push Groups tab. Okta pushes only the groups you list there, one at a time, not every group in the org.
Use Push now on the Push Groups tab to force an immediate push once the setup is right.
Provisioned users have the wrong role, or no access (Main Workspace)
Oleria grants roles through group membership, never on the user record, and Okta’s Push Groups can’t set a role on the group it creates. Until you map it, its members fall back to Oleria’s read-only analyst role.In Oleria, go to Settings → Manage Users, select the Groups tab, select the group, click Change role, and choose the role it should grant. Every current and future member inherits it. See How Oleria maps roles and groups.This doesn’t apply to the Governance App, where every provisioned user gets the reviewer role automatically.
Someone I deactivated or unassigned in Okta still has access to Oleria
Deactivate Users has to be enabled under Provisioning → To App. Without it, Okta pushes creates and updates but never tells Oleria to disable anyone, so unassigning someone in Okta silently leaves their Oleria account active.With it enabled, the change travels within a minute or two. Confirm it in Reports → System Log, then in Manage Users. If nothing happened, check that the person was removed from every group assigned to the app, not just one.
Provisioned users have a wrong username or email address
Okta sends the app username as userName, and the app username format is set per app. If your users arrive in Oleria identified by their Okta username rather than their email, set Application username to Email on the app’s Sign On tab, which also keeps SSO and SCIM identifying people the same way.For any other attribute that arrives wrong, check the profile mappings under Provisioning → To App, then push one affected user again rather than waiting for their next change.
Provisioning reports duplicate or conflict errors, or provisioned users never update
Okta matches existing users on userName. If the address Okta sends as userName doesn’t match the one Oleria stored, Okta can’t find the account it already created and tries to create it again, which Oleria rejects as a duplicate.Confirm Application username is Email and that the app’s email attribute maps to user.email, so userName and emails agree. See Confirm userName and email carry the same address.
{"docsConfig":{"theme":"mint","$schema":"https://mintlify.com/docs.json","name":"Oleria Identity Security","colors":{"primary":"#027864","light":"#027864","dark":"#58D5BA"},"logo":{"light":"https://mintcdn.com/oleria/KyPIHO-0OF6fE_DF/images/OleriaLightMode-1.png?fit=max\u0026auto=format\u0026n=KyPIHO-0OF6fE_DF\u0026q=85\u0026s=906d33a8c505e2a96b7c6a1583335e1d","dark":"https://mintcdn.com/oleria/9Xgkiz4uBKa5_MIM/images/Oleria_Dark_2.png?fit=max\u0026auto=format\u0026n=9Xgkiz4uBKa5_MIM\u0026q=85\u0026s=eed2ceca9aaaa1597123d7edabce3ce2"},"favicon":"https://mintcdn.com/oleria/rpFX8xIzvg2xF0B0/images/favicon.png?fit=max\u0026auto=format\u0026n=rpFX8xIzvg2xF0B0\u0026q=85\u0026s=b2b79fcf5eaf05bffa7866fe11571fd9","appearance":{"default":"light"},"background":{"color":{"light":"#ffffff"}},"navbar":{"links":[{"href":"mailto:support@oleria.com","label":"Support"}]},"footer":{"socials":{"website":"https://oleria.com"}},"styling":{"latex":false},"navigation":{"pages":[]}},"deployment":{"deploymentMetadataValue":{"subdomain":"oleria","hasAudioNarration":false,"actualSubdomain":"oleria","customDomains":["docs.oleria.com"],"gitSource":{"type":"github","owner":"roanokedatasecurity","repo":"oleria-docs","deployBranch":"main","contentDirectory":"","isPrivate":true,"mountPath":"","label":""},"chroma":{"liveDeploymentHistoryId":"6aeace4bfeac5b4749625236","collectionId":"2edfd769-349b-438c-87bc-d9700635ec79","schemaVersion":"v3","latestBuiltDeploymentHistoryId":"6aeace4bfeac5b4749625236"},"feedback":{"thumbs":true},"entitlements":{"AI_CHAT":{"status":"ENABLED"},"WEB_MCP":{"status":"ENABLED"},"NARRATION":{"status":"ENABLED"}},"buildId":"6aead2ddcd71ec77215afae7","clientVersion":"0.0.4054","searchFilterCounts":[{"language":"default","tag":"Integrations","count":370},{"language":"default","tag":"Applications","count":312},{"language":"default","tag":"API Reference","count":91},{"language":"default","tag":"Inventory \u0026 Actions","count":72},{"language":"default","tag":"Product","count":69},{"language":"default","tag":"Security and compliance","count":52},{"language":"default","tag":"Developer tools","count":48},{"language":"default","tag":"Collaboration and productivity","count":39},{"language":"default","tag":"Data and analytics","count":34},{"language":"default","tag":"Finance and operations","count":29}]},"assistantConfig":{"enableAskAiButton":false,"enableStarterQuestions":false,"enableAskAiSearchBar":true,"deflection":{"enabled":true,"email":"support@oleria.com","showHelpButton":true}},"basePath":"","hasChatPermissions":true,"hasWebMcpPermissions":true,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"rbac-expansion","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"full-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"byok-sep-25","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"vite-origin","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-updated-9-15","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-sso-scim","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-signup","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-dual-write","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-enabled","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"approve-review-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"sso-setup-deadline-banner","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"googleFontsInlined":false},"customCss":[],"page":{"pagePath":"administration/okta-sso-scim-setup","slug":"/administration/okta-sso-scim-setup","pageMetadata":{"title":"Okta: end-to-end SSO and SCIM setup","description":"Connect Okta to Oleria for single sign-on and user provisioning, covering both the Main Workspace and the Governance App.","href":"/administration/okta-sso-scim-setup"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"Connect Okta to Oleria for single sign-on and user provisioning, covering both the Main Workspace and the Governance App.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,code:`code`,em:`em`,li:`li`,ol:`ol`,p:`p`,strong:`strong`,tbody:`tbody`,td:`td`,th:`th`,thead:`thead`,tr:`tr`,ul:`ul`,..._provideComponents(),...props.components},{Accordion,AccordionGroup,Heading,Note,OptimizedImage,Step,Steps,Table,Warning}=_components;if(!Accordion)_missingMdxReference(`Accordion`,true);if(!AccordionGroup)_missingMdxReference(`AccordionGroup`,true);if(!Heading)_missingMdxReference(`Heading`,true);if(!Note)_missingMdxReference(`Note`,true);if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);if(!Step)_missingMdxReference(`Step`,true);if(!Steps)_missingMdxReference(`Steps`,true);if(!Table)_missingMdxReference(`Table`,true);if(!Warning)_missingMdxReference(`Warning`,true);return _jsxs(_Fragment,{children:[_jsxs(_components.p,{children:[`This page walks through connecting Okta to Oleria from a blank slate: creating the Okta app, wiring up single sign-on (SSO), and turning on directory provisioning (SCIM), for whichever combination of Main Workspace and Governance App you need. It draws on `,_jsx(_components.a,{href:`/administration/sso-configuration`,children:`SSO configuration`}),`, `,_jsx(_components.a,{href:`/administration/scim-user-provisioning`,children:`SCIM user provisioning`}),`, and `,_jsx(_components.a,{href:`/administration/scim-governance-provisioning`,children:`Governance App SCIM provisioning`}),` - see those pages for the full request/response reference and troubleshooting detail; this page focuses on getting from zero to a working Okta connection.`]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`This page is about signing in to Oleria and provisioning Oleria accounts from Okta. It is not the same as the `,_jsx(_components.a,{href:`/integrations/okta`,children:`Okta integration`}),` under `,_jsx(_components.strong,{children:`Integrations`}),`, which connects Okta as a data source so Oleria can analyze your Okta tenant’s identities and access. That integration does not affect who can sign in to Oleria or how.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`overview`,children:`Overview`}),`\n`,_jsx(Heading,{level:`3`,id:`main-workspace-vs-governance-app`,children:`Main Workspace vs. Governance App`}),`\n`,_jsx(_components.p,{children:`Oleria has two independent surfaces, each with its own sign-in and provisioning configuration:`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Main Workspace`}),` - where administrators, operators, and analysts run Oleria itself: posture, access graph, workflows, and settings.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Governance App`}),` - a separate portal where reviewers and approvers complete `,_jsx(_components.a,{href:`/governance/access-review`,children:`access reviews`}),`, act on access requests, and work governance queues. Governance app users are a distinct population from workspace users, typically much larger (anyone in the org who might approve or review something), and usually don’t need any other access to Oleria.`]}),`\n`]}),`\n`,_jsxs(_components.p,{children:[`Each surface has its own tab in `,_jsx(_components.strong,{children:`Settings → SSO Configuration`}),` and its own tab in `,_jsx(_components.strong,{children:`Settings → SCIM Configuration`}),`, with separate identity provider lists, separate SCIM credentials, and separate SCIM base URLs. You can connect Okta to one, the other, or both - they don’t have to match. For example, it’s common to enable SSO and SCIM for the Governance App (so every employee can be provisioned as a reviewer automatically) while managing the smaller set of Main Workspace administrators by hand.`]}),`\n`,_jsx(Heading,{level:`3`,id:`sso-vs-scim-vs-automatic-user-provisioning`,children:`SSO vs. SCIM vs. automatic user provisioning`}),`\n`,_jsx(_components.p,{children:`Oleria has three related but independent mechanisms. SSO is for authentication only, where as SCIM and automatic user provisioning are for provisioning.`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{style:{textAlign:`left`}}),_jsx(_components.th,{style:{textAlign:`left`},children:`SSO`}),_jsx(_components.th,{style:{textAlign:`left`},children:`SCIM`}),_jsx(_components.th,{style:{textAlign:`left`},children:`Automatic user provisioning`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`Solves`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Authentication - how a user proves who they are when signing in`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Provisioning - how an Oleria account gets created, updated, and removed`}),_jsx(_components.td,{style:{textAlign:`left`},children:`An Oleria setting that creates an account the moment someone signs in and doesn’t already have one`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`Direction`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta redirects the user’s browser to Oleria with a signed SAML assertion at sign-in time`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta’s provisioning engine calls Oleria’s SCIM API directly, independent of anyone signing in`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Triggered as a side effect of a successful SAML or social sign-in; nothing is pushed from Okta`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`Configured where`}),_jsxs(_components.td,{style:{textAlign:`left`},children:[_jsx(_components.strong,{children:`Settings → SSO Configuration`}),`, either tab`]}),_jsxs(_components.td,{style:{textAlign:`left`},children:[_jsx(_components.strong,{children:`Settings → SCIM Configuration`}),`, either tab`]}),_jsxs(_components.td,{style:{textAlign:`left`},children:[_jsx(_components.strong,{children:`Settings → SSO Configuration`}),`, `,_jsx(_components.strong,{children:`Governance App`}),` tab only`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`Can deactivate/remove users`}),_jsx(_components.td,{style:{textAlign:`left`},children:`No`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Yes`}),_jsx(_components.td,{style:{textAlign:`left`},children:`No - it only ever creates accounts`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`Without it`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Users sign in with a social login or in rare cases a local account`}),_jsx(_components.td,{style:{textAlign:`left`},children:`An administrator adds, updates, and removes users by hand`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Only administrators, or SCIM, create accounts`})]})]})]}),`\n`,_jsxs(_components.p,{children:[`See `,_jsx(_components.a,{href:`/administration/sso-configuration#automatically-provision-reviewers`,children:`Automatically provision reviewers`}),` for the full detail on that setting - `,_jsx(_components.a,{href:`#part-2-set-up-scim`,children:`Part 2`}),` of this page is about SCIM, not automatic user provisioning.`]}),`\n`,_jsx(Heading,{level:`3`,id:`possible-provisioning-flows`,children:`Possible provisioning flows`}),`\n`,_jsx(_components.p,{children:`Because these mechanisms are independent, and each applies per workspace, several combinations are all valid. Pick the one that matches what you’re trying to achieve before you start:`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{style:{textAlign:`left`},children:`Flow`}),_jsx(_components.th,{style:{textAlign:`left`},children:`Main Workspace`}),_jsx(_components.th,{style:{textAlign:`left`},children:`Governance App`}),_jsx(_components.th,{style:{textAlign:`left`},children:`When to use it`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`SSO + SCIM (recommended)`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta SAML + SCIM`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta SAML + SCIM`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Full end-to-end: Okta group membership determines who has an Oleria account and what role they hold, and the same Okta credentials sign them in, including automatic deactivation when someone is unassigned. This is what the rest of this page sets up.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`SSO only`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta SAML`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta SAML`}),_jsxs(_components.td,{style:{textAlign:`left`},children:[`Small, stable user list you’re comfortable adding by hand in `,_jsx(_components.a,{href:`/administration/manage-users`,children:`Manage Users`}),`, but want Okta credentials for sign-in. Apply to either tab independently, or both.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`SCIM only`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta SCIM`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta SCIM`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Users should come from Okta automatically, but you’re not ready to move sign-in off social login yet. Apply to either workspace independently, or both.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`SSO + automatic user provisioning`}),_jsx(_components.td,{style:{textAlign:`left`},children:`N/A - Governance App only`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta SAML + Oleria’s automatic user provisioning toggle`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Lighter-weight than SCIM - no provisioning connector to build in Okta, accounts just appear the first time someone signs in - but there’s no automatic deprovisioning, and it’s gated only by email domain, not Okta group/app assignment. Good for “let anyone at the company become a reviewer” without building a directory sync.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:`Split by surface`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Manual, or a different IdP`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Okta SAML + SCIM`}),_jsx(_components.td,{style:{textAlign:`left`},children:`Common when only the Governance App needs to reach a broad, automatically-provisioned population (for example, every employee as a potential reviewer), while a small workspace admin team is managed separately`})]})]})]}),`\n`,_jsxs(_components.p,{children:[`This page sets up the recommended SSO + SCIM flow, one workspace at a time. If you’d rather use automatic user provisioning instead of SCIM for the Governance App, see the `,_jsx(_components.a,{href:`#part-2-set-up-scim`,children:`note at the end of Part 2`}),`.`]}),`\n`,_jsx(Heading,{level:`2`,id:`prerequisites`,children:`Prerequisites`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Administrator access to your Oleria workspace`}),`\n`,_jsxs(_components.li,{children:[`Okta `,_jsx(_components.strong,{children:`super admin`}),` access - Okta’s own guidance for enabling SCIM on a custom app is to sign in as a super admin, and lesser admin roles may not see the setting.`]}),`\n`,_jsxs(_components.li,{children:[`Decide which workspaces - `,_jsx(_components.strong,{children:`Main Workspace`}),`, `,_jsx(_components.strong,{children:`Governance App`}),`, or both - you’re connecting Okta to, and whether you want SSO, SCIM, or both for each. See `,_jsx(_components.a,{href:`#possible-provisioning-flows`,children:`Possible provisioning flows`}),` above.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`For SCIM only:`}),` your Okta org must have `,_jsx(_components.strong,{children:`Okta Lifecycle Management (LCM)`}),` entitlements. LCM is a separate Okta product from SSO, and without it the `,_jsx(_components.strong,{children:`Provisioning`}),` setting never appears on the app. Check this before you start - it’s the most common reason this setup can’t be completed. See `,_jsx(_components.a,{href:`#okta-lifecycle-management-is-required-for-scim`,children:`Okta Lifecycle Management is required for SCIM`}),` below. SSO (`,_jsx(_components.a,{href:`#part-1-set-up-sso`,children:`Part 1`}),`) does not require LCM.`]}),`\n`,_jsxs(_components.li,{children:[`For SCIM into the `,_jsx(_components.strong,{children:`Main Workspace`}),`: know which Oleria roles (`,_jsx(_components.code,{children:`admin`}),`, `,_jsx(_components.code,{children:`operator`}),`, `,_jsx(_components.code,{children:`analyst`}),`, `,_jsx(_components.code,{children:`governance-operator`}),`, `,_jsx(_components.code,{children:`identity-lifecycle-operator`}),`) your Okta groups should map to. See `,_jsx(_components.a,{href:`/administration/scim-user-provisioning#how-oleria-maps-roles-and-groups`,children:`How Oleria maps roles and groups`}),`.`]}),`\n`]}),`\n`,_jsx(Heading,{level:`2`,id:`part-1-set-up-sso`,children:`Part 1: Set up SSO`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open Oleria's SSO configuration page`,children:_jsxs(_components.p,{children:[`In Oleria, go to `,_jsx(_components.strong,{children:`Settings → SSO Configuration`}),`, select the `,_jsx(_components.strong,{children:`Main Workspace`}),` or `,_jsx(_components.strong,{children:`Governance App`}),` tab depending on which application you’re connecting first, and click `,_jsx(_components.strong,{children:`Add IdP`}),` in the `,_jsx(_components.strong,{children:`SAML IdP`}),` card.`]})}),_jsxs(Step,{title:`Create the Okta app`,children:[_jsxs(_components.p,{children:[`In the Okta Admin Console, go to `,_jsx(_components.strong,{children:`Applications → Applications → Create App Integration`}),`, select `,_jsx(_components.strong,{children:`Classic experience`}),` since `,_jsx(_components.strong,{children:`Integration Wizard`}),` is `,_jsx(_components.strong,{children:`not supported at this time`}),`. Select `,_jsx(_components.strong,{children:`SAML 2.0`}),`, and name it something that identifies which Oleria workspace it’s for (for example `,_jsx(_components.code,{children:`Oleria - Main Workspace`}),` or `,_jsx(_components.code,{children:`Oleria - Governance App`}),`) - this matters once you’ve done this twice for both workspaces.`]}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_create_application_classic.png?fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=c3d92ddd7a0b1de85de7e5b8f041a67f`,alt:`Image of the Integration Wizard vs Classic experience prompt`,\"data-og-width\":`1600`,width:`1600`,\"data-og-height\":`1120`,height:`1120`,\"data-path\":`images/administration/sso/okta/okta_create_application_classic.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_create_application_classic.png?w=280\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=0615347d1621467fd788f71237a9beb6 280w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_create_application_classic.png?w=560\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=a1949ed84e1401dcd6555361ae3e7789 560w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_create_application_classic.png?w=840\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=eb06155a2a36235713eec7783f5e9624 840w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_create_application_classic.png?w=1100\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=e0608a5aceb0506e248ab0064d3c1d3c 1100w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_create_application_classic.png?w=1650\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=53929d43ecdd563a6ee3604f3aa83eec 1650w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_create_application_classic.png?w=2500\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=3fbf5a0561259d67e188eb5b41b99cee 2500w`})]}),_jsxs(Step,{title:`Copy Oleria's SP details into Okta`,children:[_jsxs(_components.p,{children:[`On Oleria’s `,_jsx(_components.strong,{children:`Oleria details`}),` step, copy the `,_jsx(_components.strong,{children:`Entity ID`}),` and `,_jsx(_components.strong,{children:`ACS URL`}),`. On Okta’s `,_jsx(_components.strong,{children:`Configure SAML`}),` step, enter them as the `,_jsx(_components.strong,{children:`Audience URI (SP Entity ID)`}),` and `,_jsx(_components.strong,{children:`Single sign-on URL`}),`. Copy or download the `,_jsx(_components.strong,{children:`Request signing certificate`}),` shown on Oleria’s `,_jsx(_components.strong,{children:`Oleria details`}),` step - you’ll need it later in this Part if you turn on `,_jsx(_components.strong,{children:`Sign requests`}),`.`]}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_configure_saml.png?fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=2adb57fbc584e9e15e8d46f9e59a4ec4`,alt:`Image of Okta's Configure SAML page`,\"data-og-width\":`1440`,width:`1440`,\"data-og-height\":`1074`,height:`1074`,\"data-path\":`images/administration/sso/okta/okta_configure_saml.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_configure_saml.png?w=280\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=45540106bf90b89a53be9667adb30595 280w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_configure_saml.png?w=560\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=0ae9f41c9d28165d5fec96d28b4d31db 560w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_configure_saml.png?w=840\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=7e1bab49a8a1d044e06269caf50e92b7 840w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_configure_saml.png?w=1100\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=908675058879e6963352acd0582c7d9f 1100w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_configure_saml.png?w=1650\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=f37d1c2a478ab492a09d9e0afedc3cbb 1650w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_configure_saml.png?w=2500\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=b697c8ba699679d313b88e9544ea4f6b 2500w`})]}),_jsxs(Step,{title:`Configure the NameID`,children:[_jsxs(_components.p,{children:[`Still on `,_jsx(_components.strong,{children:`Configure SAML`}),`, set `,_jsx(_components.strong,{children:`Name ID format`}),` to `,_jsx(_components.strong,{children:`Persistent`}),` and `,_jsx(_components.strong,{children:`Application username`}),` to `,_jsx(_components.strong,{children:`Email`}),`.`]}),_jsx(Warning,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Application username`}),` is also the value Okta sends as `,_jsx(_components.code,{children:`userName`}),` when you add SCIM in `,_jsx(_components.a,{href:`#part-2-set-up-scim`,children:`Part 2`}),`, so leave it on `,_jsx(_components.strong,{children:`Email`}),` rather than `,_jsx(_components.strong,{children:`Okta username`}),` or a custom expression. Oleria identifies an account by one email address, and Okta’s matching queries look that address up by `,_jsx(_components.code,{children:`userName`}),`. If `,_jsx(_components.strong,{children:`Application username`}),` resolves to something other than the user’s email - a `,_jsx(_components.code,{children:`user.login`}),` on a different domain, say - then `,_jsx(_components.code,{children:`userName`}),` and the provisioned `,_jsx(_components.code,{children:`emails`}),` value disagree, Okta can’t find the account it created, and it retries the create on every sync. Keep `,_jsx(_components.strong,{children:`Application username`}),`, the app’s `,_jsx(_components.code,{children:`email`}),` attribute mapping, and the `,_jsx(_components.code,{children:`email`}),` attribute statement in the next step all pointing at the user’s email.`]})})]}),_jsxs(Step,{title:`Add the required attribute statements`,children:[_jsx(Note,{children:_jsxs(_components.p,{children:[`This step is on a `,_jsx(_components.strong,{children:`different page`}),` than the previous one for most Okta orgs today. On Okta Identity Engine (OIE) orgs - the default for new orgs - Attribute Statements aren’t part of the `,_jsx(_components.strong,{children:`Configure SAML`}),` page at all; add them afterward on the app’s `,_jsx(_components.strong,{children:`Sign On`}),` tab, under `,_jsx(_components.strong,{children:`Attribute Statements`}),`. Only on legacy Okta Classic Engine orgs do they appear further down the same `,_jsx(_components.strong,{children:`Configure SAML`}),` page.`]})}),_jsxs(_components.p,{children:[`Add an attribute statement `,_jsx(_components.strong,{children:`Name`}),` `,_jsx(_components.code,{children:`email`}),`, `,_jsx(_components.strong,{children:`Name format`}),` `,_jsx(_components.code,{children:`Unspecified`}),`, `,_jsx(_components.strong,{children:`Value`}),` `,_jsx(_components.code,{children:`user.profile.email`}),`, and a second `,_jsx(_components.strong,{children:`Name`}),` `,_jsx(_components.code,{children:`name`}),`, `,_jsx(_components.strong,{children:`Name format`}),` `,_jsx(_components.code,{children:`Unspecified`}),`, `,_jsx(_components.strong,{children:`Value`}),` `,_jsx(_components.code,{children:`user.profile.firstName + \" \" + user.profile.lastName`}),`.`]}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_attribute_statements.png?fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=a8dcdff7f42374f0fb6f8aeba24b2737`,alt:`Image of Okta's Sign On tab with Attribute Statements section`,\"data-og-width\":`1440`,width:`1440`,\"data-og-height\":`832`,height:`832`,\"data-path\":`images/administration/sso/okta/okta_attribute_statements.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_attribute_statements.png?w=280\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=03906b64b62f308df0100d219205dfe4 280w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_attribute_statements.png?w=560\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=2cfa7e48ef04b039f1994eef7f139a13 560w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_attribute_statements.png?w=840\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=1dea15bd41e37db74c426768bfcffd41 840w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_attribute_statements.png?w=1100\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=df1a3cf1981cce44b193719a964ff49c 1100w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_attribute_statements.png?w=1650\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=2dcc46ead36ad597a8c514a562cda320 1650w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/sso/okta/okta_attribute_statements.png?w=2500\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=5fa6392aae534af11a775605103b3b3f 2500w`}),_jsxs(_components.p,{children:[`See `,_jsx(_components.a,{href:`/administration/sso-configuration#connect-a-saml-identity-provider`,children:`Connect a SAML identity provider`}),` for why each of these is required.`]})]}),_jsx(Step,{title:`Assign users`,children:_jsx(_components.p,{children:`Assign the app to the users or groups who should be able to sign in to Oleria.`})}),_jsx(Step,{title:`Enter the SAML IdP details in Oleria`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Sign On`}),` tab copy the `,_jsx(_components.strong,{children:`Identity Provider metadata`}),` URL.\nBack in Oleria, complete the `,_jsx(_components.strong,{children:`SAML IdP details`}),` step: give the identity provider a `,_jsx(_components.strong,{children:`Name`}),`, paste the Okta metadata URL into `,_jsx(_components.strong,{children:`Metadata`}),`, and decide whether to turn on `,_jsx(_components.strong,{children:`Sign requests`}),` and/or `,_jsx(_components.strong,{children:`Encrypt SAML responses`}),`. Click `,_jsx(_components.strong,{children:`Add identity provider`}),`.`]})}),_jsxs(Step,{title:`If you turned on Sign requests: upload the request signing certificate to Okta`,children:[_jsxs(_components.p,{children:[`Skip this step if you left `,_jsx(_components.strong,{children:`Sign requests`}),` off. Otherwise, go back to the Okta app’s `,_jsx(_components.strong,{children:`General`}),` tab, open `,_jsx(_components.strong,{children:`SAML Settings → Edit`}),`, and click `,_jsx(_components.strong,{children:`Show Advanced Settings`}),`. Upload Oleria’s `,_jsx(_components.strong,{children:`Request signing certificate`}),` (downloaded in `,_jsx(_components.strong,{children:`pem`}),` format earlier in this Part) next to `,_jsx(_components.strong,{children:`Signature Certificate`}),`, then set `,_jsx(_components.strong,{children:`Signed Requests`}),` to `,_jsx(_components.strong,{children:`Validate SAML requests with signature certificates`}),`.`]}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_saml_request_signing_cert.png?fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=6c6727f8bbde40b602dfc88968cad842`,alt:`Image of Okta's SAML Settings advanced settings with Signature Certificate upload`,\"data-og-width\":`1154`,width:`1154`,\"data-og-height\":`1826`,height:`1826`,\"data-path\":`images/administration/sso/okta/okta_saml_request_signing_cert.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_saml_request_signing_cert.png?w=280\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=3c2f929d21fd5f178a808177ace962db 280w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_saml_request_signing_cert.png?w=560\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=7d35f0641ae8213ac6a27969ac81ad31 560w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_saml_request_signing_cert.png?w=840\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=86f7d3f6e9a100c10f2577af9dc8f9e7 840w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_saml_request_signing_cert.png?w=1100\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=52603e51dd78bbd694d758e34b722228 1100w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_saml_request_signing_cert.png?w=1650\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=fabb38e247883aa48ff095bee5ae3553 1650w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_saml_request_signing_cert.png?w=2500\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=388213b523db1d0b283b90ff752fa55e 2500w`})]}),_jsxs(Step,{title:`If you turned on Encrypt SAML responses: download and upload the response encryption certificate`,children:[_jsxs(_components.p,{children:[`Skip this step if you left `,_jsx(_components.strong,{children:`Encrypt SAML responses`}),` off. Otherwise, back in Oleria you’ll see a prompt to download the `,_jsx(_components.strong,{children:`Response encryption certificate`}),` generated specifically for this identity provider - download it in `,_jsx(_components.strong,{children:`pem`}),` format. In Okta, in that same `,_jsx(_components.strong,{children:`Show Advanced Settings`}),` view, set `,_jsx(_components.strong,{children:`Assertion Encryption`}),` to `,_jsx(_components.strong,{children:`Encrypted`}),` and upload the certificate next to `,_jsx(_components.strong,{children:`Encryption Certificate`}),`.`]}),_jsx(_components.p,{children:`Before:`}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_before.png?fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=3f578ed25b2c90de0cce956879414466`,alt:`Image of Okta's SAML Settings advanced settings before setting Assertion Encryption to Encrypted`,\"data-og-width\":`1154`,width:`1154`,\"data-og-height\":`1416`,height:`1416`,\"data-path\":`images/administration/sso/okta/okta_response_encryption_before.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_before.png?w=280\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=d5ac34c7c4b67230a8c35791a8a0c51b 280w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_before.png?w=560\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=4f3ee9120f0bb1ccf24a34641870e506 560w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_before.png?w=840\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=18611a87ee0bb19f3e48b10bc809f1f5 840w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_before.png?w=1100\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=f3ef3eae8010b3b1bc9b75145a866676 1100w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_before.png?w=1650\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=bd90d8e9fbb829cbe7a334e97f1b49d5 1650w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_before.png?w=2500\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=fd34d0b3b5ded3dce85e161521acb31a 2500w`}),_jsx(_components.p,{children:`After:`}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_after.png?fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=37711f8aa51e6ce92dead1563cd6a946`,alt:`Image of Okta's SAML Settings advanced settings after setting Assertion Encryption to Encrypted`,\"data-og-width\":`1162`,width:`1162`,\"data-og-height\":`1710`,height:`1710`,\"data-path\":`images/administration/sso/okta/okta_response_encryption_after.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_after.png?w=280\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=851809dd5be18c954a0a3b052a2e13e8 280w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_after.png?w=560\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=382b8a5220224ca8f546b189a0a862fd 560w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_after.png?w=840\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=9e9d7800cc00efa54494642b9376744b 840w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_after.png?w=1100\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=773767631543c07ad3785b939bab9779 1100w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_after.png?w=1650\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=65830f60b2888c2d0fef4db1f0c3e741 1650w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/sso/okta/okta_response_encryption_after.png?w=2500\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=958d46d8ca1b013b4f4fe5d276ef9749 2500w`})]}),_jsx(Step,{title:`Confirm sign-in works`,children:_jsxs(_components.p,{children:[`Sign out of Oleria, go to `,_jsx(_components.a,{href:`https://www.oleria.com/sign-in`,children:`https://www.oleria.com/sign-in`}),`, select the new identity provider, and confirm you land back in Oleria signed in.`]})})]}),`\n`,_jsx(Heading,{level:`2`,id:`part-2-set-up-scim`,children:`Part 2: Set up SCIM`}),`\n`,_jsx(_components.p,{children:`You can add SCIM provisioning to the same Okta app you just created for SSO - Okta supports provisioning on custom SAML apps once you turn it on, provided your org is licensed for it.`}),`\n`,_jsx(Heading,{level:`3`,id:`okta-lifecycle-management-is-required-for-scim`,children:`Okta Lifecycle Management is required for SCIM`}),`\n`,_jsxs(Warning,{children:[_jsxs(_components.p,{children:[`Outbound SCIM provisioning is part of `,_jsx(_components.strong,{children:`Okta Lifecycle Management (LCM)`}),`, a separate Okta product from SSO. If your org isn’t entitled to LCM, the `,_jsx(_components.strong,{children:`Provisioning`}),` setting simply isn’t rendered: the `,_jsx(_components.strong,{children:`App Settings`}),` dialog shows only `,_jsx(_components.strong,{children:`Application label`}),`, `,_jsx(_components.strong,{children:`Application visibility`}),`, `,_jsx(_components.strong,{children:`Auto-launch`}),`, and the two notes fields, with no `,_jsx(_components.strong,{children:`Provisioning`}),` options to select. Nothing is greyed out, so it reads as though the setting doesn’t exist.`]}),_jsxs(_components.p,{children:[`LCM is included in Okta’s `,_jsx(_components.strong,{children:`Essentials`}),`, `,_jsx(_components.strong,{children:`Professional`}),`, and `,_jsx(_components.strong,{children:`Enterprise`}),` suites and in the `,_jsx(_components.strong,{children:`Okta Identity Governance`}),` add-on. It is `,_jsx(_components.em,{children:`not`}),` included in the `,_jsx(_components.strong,{children:`Starter`}),` or `,_jsx(_components.strong,{children:`Core Essentials`}),` plans, where it’s a paid add-on.`]}),_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Quickest way to check:`}),` in the Okta Admin Console, look at any other app in your org that should provision users (for example a directory app like Google Workspace). If no app in the org has a working `,_jsx(_components.strong,{children:`Provisioning`}),` tab, your org doesn’t have LCM. Your Okta account team can confirm whether it’s in your contract or needs to be added.`]}),_jsxs(_components.p,{children:[`If you can’t add LCM, Oleria still has working options - see `,_jsx(_components.a,{href:`#alternatives-without-lifecycle-management`,children:`Alternatives without Lifecycle Management`}),`.`]})]}),`\n`,_jsxs(Steps,{children:[_jsxs(Step,{title:`Enable provisioning on the Okta app`,children:[_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_app_settings_provisioning.png?fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=8abc5f84bb7e1b3dd3695dd6d2e26027`,alt:`Image showing the expected Provisioning radio group in App Settings`,\"data-og-width\":`1136`,width:`1136`,\"data-og-height\":`1086`,height:`1086`,\"data-path\":`images/administration/scim/okta/okta_app_settings_provisioning.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_app_settings_provisioning.png?w=280\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=9a4c8f88d40fc307e4faf42dbfd16361 280w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_app_settings_provisioning.png?w=560\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=7ce80576b36d0cab22d3d0394a0497c3 560w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_app_settings_provisioning.png?w=840\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=3ab965bb9a2ff36387cc66f361a7e570 840w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_app_settings_provisioning.png?w=1100\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=c40988d948c5db50b9c5890bc746415c 1100w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_app_settings_provisioning.png?w=1650\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=94e5946a7b39da5480081343cfed44f5 1650w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_app_settings_provisioning.png?w=2500\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=fb2e46cf208ff5b7992dc6494243aca0 2500w`}),_jsxs(_components.p,{children:[`Open the same Okta app from Part 1. On the `,_jsx(_components.strong,{children:`General`}),` tab, click `,_jsx(_components.strong,{children:`Edit`}),` next to `,_jsx(_components.strong,{children:`App Settings`}),`, then set `,_jsx(_components.strong,{children:`Provisioning`}),` to `,_jsx(_components.strong,{children:`SCIM`}),` - some Okta orgs show this as a `,_jsx(_components.strong,{children:`Enable SCIM provisioning`}),` checkbox instead of a radio group - and click `,_jsx(_components.strong,{children:`Save`}),`. A new `,_jsx(_components.strong,{children:`Provisioning`}),` tab appears on the app.`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`No `,_jsx(_components.strong,{children:`Provisioning`}),` setting in the dialog? The most likely cause is that your org isn’t entitled to LCM, as described above. Two other causes: the app is an `,_jsx(_components.strong,{children:`OIDC`}),` integration rather than `,_jsx(_components.strong,{children:`SAML 2.0`}),` or `,_jsx(_components.strong,{children:`SWA`}),` (Okta doesn’t support SCIM on custom OIDC apps created in the Classic experience), or the app was created through the Okta API or Terraform rather than the Admin Console, which can leave the provisioning options absent or unconfigurable. If the app is a SAML 2.0 app created in the Admin Console and your org does have LCM, contact Okta Support to check whether the provisioning feature needs activating for your org.`]})})]}),_jsx(Step,{title:`Get Oleria's SCIM credentials`,children:_jsxs(_components.p,{children:[`In Oleria, go to `,_jsx(_components.strong,{children:`Settings → SCIM Configuration`}),` and select the same workspace you used in Part 1 (`,_jsx(_components.strong,{children:`Main Workspace`}),` or `,_jsx(_components.strong,{children:`Governance App`}),`). Copy the `,_jsx(_components.strong,{children:`SCIM Base URL`}),`, `,_jsx(_components.strong,{children:`Client ID`}),`, `,_jsx(_components.strong,{children:`Client Secret`}),`, and `,_jsx(_components.strong,{children:`OAuth Token URL`}),`.`]})}),_jsxs(Step,{title:`Configure the API integration`,children:[_jsxs(_components.p,{children:[`On the Okta app’s `,_jsx(_components.strong,{children:`Provisioning`}),` tab, select `,_jsx(_components.strong,{children:`Integration`}),`, click `,_jsx(_components.strong,{children:`Edit`}),`. Enter Oleria’s `,_jsx(_components.strong,{children:`SCIM Base URL`}),` as the `,_jsx(_components.strong,{children:`SCIM connector base URL`}),`, for unique identifier enter `,_jsx(_components.strong,{children:`userName`}),`, and check `,_jsx(_components.strong,{children:`Push New Users`}),`, `,_jsx(_components.strong,{children:`Push Profile Updates`}),`, and `,_jsx(_components.strong,{children:`Push Groups`}),`.\nSet `,_jsx(_components.strong,{children:`Authentication Mode`}),` to `,_jsx(_components.strong,{children:`OAuth 2`}),`, under `,_jsx(_components.strong,{children:`OAuth 2`}),` set `,_jsx(_components.strong,{children:`Grant Type`}),` to `,_jsx(_components.strong,{children:`Client Credentials`}),`, and enter Oleria’s `,_jsx(_components.strong,{children:`OAuth Token URL`}),` as the access token endpoint along with the `,_jsx(_components.strong,{children:`Client ID`}),` and `,_jsx(_components.strong,{children:`Client Secret`}),` you copied.`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`Oleria’s SCIM API only issues short-lived tokens through this client credentials exchange - it does not accept a single, static, long-lived bearer token. Use `,_jsx(_components.strong,{children:`OAuth 2 / Client Credentials`}),` here, not the `,_jsx(_components.strong,{children:`HTTP Header`}),` (bearer token) authentication mode. Okta mints and automatically refreshes its own token from the Client ID and Client Secret, so there’s nothing to manually re-enter later. See `,_jsx(_components.a,{href:`/administration/scim-user-provisioning#authenticate-to-the-scim-api`,children:`Authenticate to the SCIM API`}),` for how this same OAuth 2.0 Client Credentials flow works if you’re ever calling the API directly instead of through Okta.`]})}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_scim_connection.png?fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=cf8c5c3bfaf1d2fd711b07f871681b64`,alt:`Image of Okta's SCIM connection settings`,\"data-og-width\":`1395`,width:`1395`,\"data-og-height\":`1273`,height:`1273`,\"data-path\":`images/administration/scim/okta/okta_scim_connection.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_scim_connection.png?w=280\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=839c5a29c79488ece24576e7d691c2a2 280w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_scim_connection.png?w=560\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=8600655658d47c42ce6c6cf3f3a35be7 560w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_scim_connection.png?w=840\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=2e748967ddb4acbf1ea6fb6d098b20e2 840w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_scim_connection.png?w=1100\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=d9cfebec310d32352e57150e06b46fe0 1100w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_scim_connection.png?w=1650\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=8d2b1e78cc76d9236c6fe1aa71d1930f 1650w, https://mintcdn.com/oleria/ufskJaMSpQIvEZ7z/images/administration/scim/okta/okta_scim_connection.png?w=2500\u0026fit=max\u0026auto=format\u0026n=ufskJaMSpQIvEZ7z\u0026q=85\u0026s=c0c66f025d5d47cd55773993ff5ca27e 2500w`})]}),_jsx(Step,{title:`Turn on the provisioning actions you need`,children:_jsxs(_components.p,{children:[`Under `,_jsx(_components.strong,{children:`Provisioning → To App`}),`, click `,_jsx(_components.strong,{children:`Edit`}),` and enable `,_jsx(_components.strong,{children:`Create Users`}),`, `,_jsx(_components.strong,{children:`Update User Attributes`}),`, and `,_jsx(_components.strong,{children:`Deactivate Users`}),`.`]})}),_jsxs(Step,{title:`Confirm userName and email carry the same address`,children:[_jsxs(_components.p,{children:[`Still under `,_jsx(_components.strong,{children:`Provisioning → To App`}),`, scroll to `,_jsx(_components.strong,{children:`Oleria Attribute Mappings`}),` and confirm the app’s `,_jsx(_components.code,{children:`email`}),` attribute maps to Okta’s `,_jsx(_components.code,{children:`user.email`}),`, which is the default. Combined with `,_jsx(_components.strong,{children:`Application username`}),` set to `,_jsx(_components.strong,{children:`Email`}),` in `,_jsx(_components.a,{href:`#part-1-set-up-sso`,children:`Part 1`}),`, that makes `,_jsx(_components.code,{children:`userName`}),` and `,_jsx(_components.code,{children:`emails`}),` carry the same address - which is what Oleria stores and what Okta’s matching queries search on.`]}),_jsxs(_components.p,{children:[`Okta requires an email on every user, so there’s no fallback to configure here. The two ways this drifts are changing `,_jsx(_components.strong,{children:`Application username`}),` away from `,_jsx(_components.strong,{children:`Email`}),`, and remapping `,_jsx(_components.code,{children:`email`}),` to something other than `,_jsx(_components.code,{children:`user.email`}),`; either one leaves the two values disagreeing for some users, which shows up as repeated create attempts for users who already exist in Oleria.`]})]}),_jsxs(Step,{title:`Main Workspace only: push groups from Okta`,children:[_jsxs(Note,{children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Main Workspace only:`}),` Oleria grants roles through group membership, not directly on the user (see `,_jsx(_components.a,{href:`/administration/scim-user-provisioning#how-oleria-maps-roles-and-groups`,children:`How Oleria maps roles and groups`}),`).`]}),_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Governance App:`}),` there is no group-to-role mapping to configure - every provisioned user is assigned the single `,_jsx(_components.code,{children:`reviewer`}),` role automatically. You only need users pushed, not groups.`]})]}),_jsxs(_components.p,{children:[`In Okta, go to the app’s `,_jsx(_components.strong,{children:`Push Groups`}),` tab and push each Okta group whose members should get Oleria access. Okta then creates the matching group in Oleria automatically via SCIM, with membership synced, but without a role set. Okta’s Push Groups doesn’t support mapping a role or any other custom attribute onto the group it creates, so a newly-created group falls back to Oleria’s read-only `,_jsx(_components.code,{children:`analyst`}),` role until you assign it a different one in the next step.`]})]}),_jsxs(Step,{title:`Main Workspace only: assign each group a role in Oleria`,children:[_jsxs(_components.p,{children:[`In Oleria, under `,_jsx(_components.strong,{children:`Settings`}),` open `,_jsx(_components.strong,{children:`Manage Users`}),`, select the `,_jsx(_components.strong,{children:`Groups`}),` tab, and for each group you push, select it, click `,_jsx(_components.strong,{children:`Change role`}),`, choose the role it should map to, and click `,_jsx(_components.strong,{children:`Save`}),`. Every current and future member of the group inherits that role. See `,_jsx(_components.a,{href:`/administration/manage-users#assign-a-role-to-a-group`,children:`Assign a role to a group`}),` for the full walkthrough.`]}),_jsx(_components.p,{children:`Oleria’s Manage Users page:`}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_groups.png?fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=47ef3191effa59264dba6ba975ed838f`,alt:`Image of Oleria's Manage Users page on Groups tab`,\"data-og-width\":`1622`,width:`1622`,\"data-og-height\":`1924`,height:`1924`,\"data-path\":`images/administration/scim/oleria_manage_users_groups.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_groups.png?w=280\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=29e2664ba2dcc58b57c39cf76363de95 280w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_groups.png?w=560\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=04c8b50a908ce0154917da38e7644f4a 560w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_groups.png?w=840\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=c34d28c62c2217fb6c10cbab9a7692d6 840w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_groups.png?w=1100\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=3d5e11e7160e4d20d81d530451c7bc27 1100w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_groups.png?w=1650\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=067d9e3941ba01a6826579041dac067b 1650w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_groups.png?w=2500\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=25d28fbdb11c4f2d60cebe984c860b7e 2500w`}),_jsx(_components.p,{children:`The detail page for a particular group:`}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_demo_group_detail.png?fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=a324b809d50a7a9c02c6fedb929d7fd5`,alt:`Image of a particular group's detail page`,\"data-og-width\":`1622`,width:`1622`,\"data-og-height\":`1924`,height:`1924`,\"data-path\":`images/administration/scim/oleria_manage_users_demo_group_detail.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_demo_group_detail.png?w=280\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=f30d0e5faab1ca367d18c671cf956d40 280w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_demo_group_detail.png?w=560\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=edb08587814ccc0cf0ddb945adbc8b72 560w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_demo_group_detail.png?w=840\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=503a86c5a8a1e394c2c19783676a812b 840w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_demo_group_detail.png?w=1100\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=a906dbe4175112cd7768149f12e4307c 1100w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_demo_group_detail.png?w=1650\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=007cfdf8d22b5981675dd4695799be3f 1650w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_demo_group_detail.png?w=2500\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=db613d4e4bef7abf1eb2c4df0018f152 2500w`}),_jsx(_components.p,{children:`Changing the role mapping for that group:`}),_jsx(OptimizedImage,{src:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_change_group_role_mapping.png?fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=6ffa63c8bac4a918bac17f55320b35af`,alt:`Image of the Change role dialog`,\"data-og-width\":`1800`,width:`1800`,\"data-og-height\":`2031`,height:`2031`,\"data-path\":`images/administration/scim/oleria_manage_users_change_group_role_mapping.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_change_group_role_mapping.png?w=280\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=9a0fa3334ab65d038be4ff2d15d56a5c 280w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_change_group_role_mapping.png?w=560\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=36acaf75ce286c56b0ac9c69c94bd7de 560w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_change_group_role_mapping.png?w=840\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=e96c747230da26d5e6466fa0b43ec58a 840w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_change_group_role_mapping.png?w=1100\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=619ba79db146925982351769ebc573bd 1100w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_change_group_role_mapping.png?w=1650\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=cefc5119d55f8a8658f99d9ea0119537 1650w, https://mintcdn.com/oleria/jnDRXaHYTJdbgSxu/images/administration/scim/oleria_manage_users_change_group_role_mapping.png?w=2500\u0026fit=max\u0026auto=format\u0026n=jnDRXaHYTJdbgSxu\u0026q=85\u0026s=1b4625155a558f0f5cc0986f841f7f5d 2500w`})]}),_jsx(Step,{title:`Assign and provision`,children:_jsxs(_components.p,{children:[`Assign the users or groups who should get Oleria accounts to the app (`,_jsx(_components.strong,{children:`Main Workspace`}),`: via the groups you just pushed; `,_jsx(_components.strong,{children:`Governance App`}),`: directly, or via any group). Okta provisions matching users into Oleria within its usual sync interval.`]})}),_jsx(Step,{title:`Verify`,children:_jsxs(_components.p,{children:[`In Oleria, confirm the new users appear (`,_jsx(_components.strong,{children:`Main Workspace`}),`: in `,_jsx(_components.a,{href:`/administration/manage-users`,children:`Manage Users`}),` with the expected role; `,_jsx(_components.strong,{children:`Governance App`}),`: in the governance reviewer list). Deactivate or unassign a test user in Okta and confirm they lose access in Oleria.`]})})]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Alternative for the Governance App:`}),` if you don’t need directory-driven deprovisioning and don’t want to build the Okta provisioning connector above, you can skip this Part entirely and use Oleria’s built-in automatic user provisioning instead - it only requires SSO (Part 1) to already be working. Follow `,_jsx(_components.a,{href:`/administration/sso-configuration#automatically-provision-reviewers`,children:`Automatically provision reviewers`}),` to enable it and set allowed email domains. Remember this is not SCIM: it only creates accounts on sign-in and never deactivates them, so it’s not a substitute for SCIM if you need automatic offboarding.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`alternatives-without-lifecycle-management`,children:`Alternatives without Lifecycle Management`}),`\n`,_jsx(_components.p,{children:`If your Okta org isn’t entitled to LCM and adding it isn’t an option, you can still get most of the way there. What’s available depends on which workspace you’re provisioning.`}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`There is no way to work around the LCM requirement from inside Okta. In particular, adding one of the generic `,_jsx(_components.strong,{children:`SCIM 2.0 Test App`}),` integrations from the Okta Integration Network doesn’t help: LCM gates the `,_jsx(_components.strong,{children:`Provisioning`}),` tab on catalog apps exactly as it does on custom apps, and those test apps authenticate with a static bearer token or basic auth rather than the OAuth 2.0 Client Credentials flow Oleria’s SCIM API expects. `,_jsx(_components.strong,{children:`Okta Workflows`}),` is not a workaround either - it’s licensed as part of Lifecycle Management and Okta Identity Governance.`]})}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{style:{textAlign:`left`},children:`Option`}),_jsx(_components.th,{style:{textAlign:`left`},children:`Applies to`}),_jsx(_components.th,{style:{textAlign:`left`},children:`What you get`}),_jsx(_components.th,{style:{textAlign:`left`},children:`What you give up`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsxs(_components.td,{style:{textAlign:`left`},children:[_jsx(_components.strong,{children:`Automatic user provisioning`}),` (recommended for reviewers)`]}),_jsx(_components.td,{style:{textAlign:`left`},children:`Governance App only`}),_jsxs(_components.td,{style:{textAlign:`left`},children:[`Accounts are created the first time someone signs in through Okta SSO, with no provisioning connector in Okta at all. Only `,_jsx(_components.a,{href:`#part-1-set-up-sso`,children:`Part 1`}),` is required. See `,_jsx(_components.a,{href:`/administration/sso-configuration#automatically-provision-reviewers`,children:`Automatically provision reviewers`}),`.`]}),_jsx(_components.td,{style:{textAlign:`left`},children:`No deprovisioning - accounts are never deactivated automatically. Scoped by email domain rather than by Okta group or app assignment.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:_jsx(_components.strong,{children:`Manage users by hand`})}),_jsx(_components.td,{style:{textAlign:`left`},children:`Main Workspace, Governance App`}),_jsxs(_components.td,{style:{textAlign:`left`},children:[`Full control over roles with no IdP-side setup. Practical for the small workspace admin population. See `,_jsx(_components.a,{href:`/administration/manage-users`,children:`Manage Users`}),`.`]}),_jsx(_components.td,{style:{textAlign:`left`},children:`Every join, role change, and departure is a manual step in Oleria.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{style:{textAlign:`left`},children:_jsx(_components.strong,{children:`Drive Oleria’s SCIM API directly`})}),_jsx(_components.td,{style:{textAlign:`left`},children:`Main Workspace, Governance App`}),_jsxs(_components.td,{style:{textAlign:`left`},children:[`Oleria’s SCIM endpoints are standard SCIM 2.0 and don’t care what calls them. A script or integration platform can read group membership from Okta’s own Users and Groups API - available to every Okta org, no LCM needed - and create, update, and deactivate the matching Oleria users and groups. See `,_jsx(_components.a,{href:`/administration/scim-user-provisioning`,children:`SCIM user provisioning`}),`.`]}),_jsx(_components.td,{style:{textAlign:`left`},children:`You own the sync logic, scheduling, and error handling that Okta’s provisioning engine would otherwise provide.`})]})]})]}),`\n`,_jsx(_components.p,{children:`A common split is automatic user provisioning for the Governance App reviewer population plus hand-managed Main Workspace admins - that combination needs only SSO, and no LCM.`}),`\n`,_jsx(Heading,{level:`2`,id:`set-up-the-second-workspace`,children:`Set up the second workspace`}),`\n`,_jsxs(_components.p,{children:[`Okta has no restriction on reusing the same `,_jsx(_components.strong,{children:`Audience URI (SP Entity ID)`}),` or SCIM base URL pattern across multiple apps, so connecting the second workspace is simply repeating `,_jsx(_components.a,{href:`#part-1-set-up-sso`,children:`Part 1`}),` and `,_jsx(_components.a,{href:`#part-2-set-up-scim`,children:`Part 2`}),` with a second, separately-named Okta app pointed at the second workspace’s Oleria details and SCIM credentials. You do not need to reuse or share anything between the two Okta apps.`]}),`\n`,_jsx(Heading,{level:`2`,id:`faq`,children:`FAQ`}),`\n`,_jsx(Heading,{level:`3`,id:`okta-and-identity-provider-basics`,children:`Okta and identity provider basics`}),`\n`,_jsxs(AccordionGroup,{children:[_jsxs(Accordion,{title:`What is Okta?`,id:`what-is-okta`,children:[_jsx(_components.p,{children:`Okta is a cloud identity service. It holds your organization’s user accounts and groups, and it’s what your people authenticate against when they open the Okta dashboard or any application your organization has connected to it.`}),_jsx(_components.p,{children:`Connecting it to Oleria means those same work accounts sign in to Oleria, and, once SCIM is on, that Okta decides who has an Oleria account at all.`}),_jsx(_components.p,{children:`Where those accounts originate doesn’t matter to Oleria. Okta’s Universal Directory may hold them natively, or they may be synced in from on-premises Active Directory or an HR system. Oleria only ever talks to Okta, so the accounts, groups, and attributes it sees are the ones that exist in Okta.`})]}),_jsxs(Accordion,{title:`What is an identity provider, and what is a service provider?`,id:`what-is-an-identity-provider-and-what-is-a-service-provider`,children:[_jsx(_components.p,{children:`An identity provider (IdP) is the system that holds user accounts and vouches for who someone is. A service provider (SP) is the application the person is trying to reach, which trusts the identity provider instead of storing passwords itself. In this setup, Okta is the identity provider and Oleria is the service provider.`}),_jsx(_components.p,{children:`A SAML sign-in runs like this:`}),_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`The user opens Oleria’s sign-in page and selects your identity provider.`}),`\n`,_jsx(_components.li,{children:`Oleria redirects their browser to Okta, which authenticates them with whatever your org requires (password, MFA, sign-on policies).`}),`\n`,_jsxs(_components.li,{children:[`Okta sends the browser back to Oleria’s `,_jsx(_components.strong,{children:`ACS URL`}),` carrying a digitally signed SAML assertion that says who the user is.`]}),`\n`,_jsx(_components.li,{children:`Oleria checks the signature against the certificate in the metadata you gave it, and signs the user in.`}),`\n`]}),_jsx(_components.p,{children:`Oleria never sees the user’s Okta password, and it can’t sign anyone in that Okta hasn’t vouched for.`})]}),_jsxs(Accordion,{title:`What are the Entity ID and ACS URL Oleria gives me?`,id:`what-are-the-entity-id-and-acs-url-oleria-gives-me`,children:[_jsxs(_components.p,{children:[`They are Oleria’s two identifiers in the SAML handshake, and you paste both into Okta’s `,_jsx(_components.strong,{children:`Configure SAML`}),` step:`]}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Entity ID`}),` (Okta calls it `,_jsx(_components.strong,{children:`Audience URI (SP Entity ID)`}),`) - the unique name of Oleria as a service provider. It’s a name, not a page you can open. Okta includes it in the assertion so Oleria can confirm the assertion was meant for it.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`ACS URL`}),` (Okta calls it `,_jsx(_components.strong,{children:`Single sign-on URL`}),`) - the Assertion Consumer Service URL, the exact address Okta posts the signed assertion to. It has to match character for character.`]}),`\n`]})]}),_jsxs(Accordion,{title:`Where is the Okta Admin Console, and what is an org?`,id:`where-is-the-okta-admin-console-and-what-is-an-org`,children:[_jsxs(_components.p,{children:[`Your org is your organization’s own instance of Okta: your users, your groups, your applications. It has a URL like `,_jsx(_components.code,{children:`https://acme.okta.com`}),`, which is where end users land, and an Admin Console at `,_jsx(_components.code,{children:`https://acme-admin.okta.com`}),`. From the end-user dashboard you can also reach it with the `,_jsx(_components.strong,{children:`Admin`}),` button. Everything on this page happens in the Admin Console, under `,_jsx(_components.strong,{children:`Applications → Applications`}),`.`]}),_jsxs(_components.p,{children:[`Many organizations also have a preview org, usually `,_jsx(_components.code,{children:`https://acme.oktapreview.com`}),`, that mirrors production. It’s a good place to walk through this setup once before doing it for real, as long as you point it at a matching Oleria workspace.`]})]}),_jsxs(Accordion,{title:`What is an app integration, and why create a custom one?`,id:`what-is-an-app-integration-and-why-create-a-custom-one`,children:[_jsx(_components.p,{children:`An app integration is the object in your org that represents an outside application your people use, along with the settings for how sign-in and provisioning work with it. Creating one doesn’t install anything; it records that your org trusts that application and who is allowed to use it.`}),_jsxs(_components.p,{children:[`The Okta Integration Network (OIN) is Okta’s catalog of applications with the SAML and SCIM fields pre-filled. Oleria isn’t in the OIN, so you create a custom `,_jsx(_components.strong,{children:`SAML 2.0`}),` app integration and fill in the URLs and attribute statements yourself, which is what `,_jsx(_components.a,{href:`#part-1-set-up-sso`,children:`Part 1`}),` walks through.`]}),_jsxs(_components.p,{children:[`When Okta offers a choice between the `,_jsx(_components.strong,{children:`Integration Wizard`}),` and the `,_jsx(_components.strong,{children:`Classic experience`}),` while creating it, choose `,_jsx(_components.strong,{children:`Classic experience`}),`. The Integration Wizard is not supported for this setup at this time.`]})]}),_jsxs(Accordion,{title:`What are Okta Identity Engine and Classic Engine, and which am I on?`,id:`what-are-okta-identity-engine-and-classic-engine-and-which-am-i-on`,children:[_jsx(_components.p,{children:`They are two generations of Okta’s underlying authentication engine. Identity Engine (OIE) is the default for new orgs and for most orgs today; Classic Engine is the older one some long-standing orgs still run.`}),_jsxs(_components.p,{children:[`It matters here for one reason: on Identity Engine, attribute statements aren’t part of the `,_jsx(_components.strong,{children:`Configure SAML`}),` page, and you add them afterward on the app’s `,_jsx(_components.strong,{children:`Sign On`}),` tab under `,_jsx(_components.strong,{children:`Attribute Statements`}),`. On Classic Engine they appear further down the `,_jsx(_components.strong,{children:`Configure SAML`}),` page itself. Same result, different page.`]}),_jsxs(_components.p,{children:[`To check which you’re on, look at the Okta version number in the Admin Console footer. A version ending in `,_jsx(_components.code,{children:`E`}),`, such as `,_jsx(_components.code,{children:`2026.02.0 E`}),`, means Identity Engine.`]})]}),_jsxs(Accordion,{title:`What are attribute statements, and what is the NameID?`,id:`what-are-attribute-statements-and-what-is-the-nameid`,children:[_jsx(_components.p,{children:`An attribute statement is one fact about the signed-in user that Okta includes in the SAML assertion. Oleria needs three things in total:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Name ID format`}),` set to `,_jsx(_components.strong,{children:`Persistent`}),`. `,_jsx(_components.strong,{children:`Application username`}),` decides what value goes into it; this setup uses `,_jsx(_components.strong,{children:`Email`}),`.`]}),`\n`,_jsxs(_components.li,{children:[`Two attribute statements named exactly `,_jsx(_components.code,{children:`email`}),` and `,_jsx(_components.code,{children:`name`}),`, both with `,_jsx(_components.strong,{children:`Name format`}),` `,_jsx(_components.code,{children:`Unspecified`}),`. `,_jsx(_components.code,{children:`Unspecified`}),` is what keeps the names arriving as plain `,_jsx(_components.code,{children:`email`}),` and `,_jsx(_components.code,{children:`name`}),` rather than wrapped in a namespace URI, which is what Oleria looks for.`]}),`\n`]}),_jsx(_components.p,{children:`If any of the three is missing or shaped differently, Oleria rejects the sign-in.`})]}),_jsxs(Accordion,{title:`What Okta admin role do I need to do this?`,id:`what-okta-admin-role-do-i-need-to-do-this`,children:[_jsxs(_components.p,{children:[`Use a `,_jsx(_components.strong,{children:`super admin`}),` account. Okta’s own guidance for enabling SCIM provisioning on a custom app is to sign in as a super admin, and narrower roles such as application administrator may not render the `,_jsx(_components.strong,{children:`Provisioning`}),` setting at all, which looks identical to not being licensed for it.`]}),_jsxs(_components.p,{children:[`If a section described here is missing or read-only for you, check the admin role you signed in with before assuming it’s a licensing problem, then check `,_jsx(_components.a,{href:`#okta-lifecycle-management-is-required-for-scim`,children:`Okta Lifecycle Management is required for SCIM`}),`.`]})]}),_jsxs(Accordion,{title:`How do I tell whether we have Lifecycle Management?`,id:`how-do-i-tell-whether-we-have-lifecycle-management`,children:[_jsxs(_components.p,{children:[`Outbound SCIM provisioning is part of Okta Lifecycle Management (LCM), which is licensed separately from SSO. The quickest check is to open any other app in your org that provisions users, such as a directory app, and look for a working `,_jsx(_components.strong,{children:`Provisioning`}),` tab. If no app in the org has one, your org doesn’t have LCM.`]}),_jsxs(_components.p,{children:[_jsx(_components.a,{href:`#okta-lifecycle-management-is-required-for-scim`,children:`Okta Lifecycle Management is required for SCIM`}),` covers which Okta plans include it, and `,_jsx(_components.a,{href:`#alternatives-without-lifecycle-management`,children:`Alternatives without Lifecycle Management`}),` covers what to do if adding it isn’t an option. SSO in `,_jsx(_components.a,{href:`#part-1-set-up-sso`,children:`Part 1`}),` needs no LCM.`]})]}),_jsxs(Accordion,{title:`What's the difference between assigning a user and provisioning a user?`,id:`whats-the-difference-between-assigning-a-user-and-provisioning-a-user`,children:[_jsxs(_components.p,{children:[`Assignment, on the app’s `,_jsx(_components.strong,{children:`Assignments`}),` tab, controls who is `,_jsx(_components.em,{children:`allowed`}),` to use the app: who can sign in through it, and, once provisioning is on, who Okta pushes to Oleria.`]}),_jsxs(_components.p,{children:[`With SSO alone, assignment creates nothing in Oleria. An assigned user who has no Oleria account can complete the Okta half of the sign-in and still be denied, until an account exists for them through SCIM, automatic user provisioning, or `,_jsx(_components.a,{href:`/administration/manage-users`,children:`Manage Users`}),`. With SCIM and `,_jsx(_components.strong,{children:`Create Users`}),` enabled, assigning someone is what triggers Okta to create their Oleria account.`]})]}),_jsxs(Accordion,{title:`How quickly does Okta push changes to Oleria?`,id:`how-quickly-does-okta-push-changes-to-oleria`,children:[_jsx(_components.p,{children:`Outbound provisioning is event-driven rather than scheduled. When you assign someone, change their profile, or deactivate them, Okta pushes that change to Oleria as it happens, usually within a minute or two, and retries on failure. There’s no sync cycle to wait for the way there is with a scheduled directory import.`}),_jsxs(_components.p,{children:[`Group membership is the exception worth knowing: use `,_jsx(_components.strong,{children:`Push now`}),` on the app’s `,_jsx(_components.strong,{children:`Push Groups`}),` tab to force a group and its membership through immediately instead of waiting for the next change to trigger it.`]})]}),_jsxs(Accordion,{title:`Where does Okta log what happened?`,id:`where-does-okta-log-what-happened`,children:[_jsx(_components.p,{children:`Two places, and picking the right one saves time:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Reports → System Log`}),` for everything. Filter by the Oleria app to see both sign-in events and provisioning events, including the error Oleria returned when it refused a SCIM request.`]}),`\n`,_jsxs(_components.li,{children:[`The Admin Console’s `,_jsx(_components.strong,{children:`Tasks`}),` page, where Okta collects provisioning actions that failed and need attention, so a broken push doesn’t only live in the log.`]}),`\n`]}),_jsx(_components.p,{children:`Okta’s log is almost always more specific about a SAML failure than what the user sees in the browser. Check it first when a sign-in doesn’t work.`})]}),_jsxs(Accordion,{title:`Does connecting Okta to Oleria change anything in my Okta org?`,id:`does-connecting-okta-to-oleria-change-anything-in-my-okta-org`,children:[_jsx(_components.p,{children:`No. Provisioning is a one-way push from Okta into Oleria: Okta creates, updates, and deactivates Oleria accounts, and Oleria never writes back into your directory. SSO doesn’t change how anyone authenticates to Okta; it only lets Oleria accept the result.`}),_jsxs(_components.p,{children:[`Deleting the app integration later stops both sign-in and provisioning. It doesn’t remove the Oleria accounts that already exist, so remove those in `,_jsx(_components.a,{href:`/administration/manage-users`,children:`Manage Users`}),` if you need them gone.`]}),_jsxs(_components.p,{children:[`This is also why the `,_jsx(_components.a,{href:`/integrations/okta`,children:`Okta integration`}),` under `,_jsx(_components.strong,{children:`Integrations`}),` is a separate thing: that one reads your org so Oleria can analyze it, and it has no bearing on who can sign in.`]})]})]}),`\n`,_jsx(Heading,{level:`3`,id:`sign-in-troubleshooting`,children:`Sign-in troubleshooting`}),`\n`,_jsxs(AccordionGroup,{children:[_jsx(Accordion,{title:`Okta says the user isn't assigned to this application`,id:`okta-says-the-user-isnt-assigned-to-this-application`,children:_jsxs(_components.p,{children:[`The person isn’t assigned to the app integration. Open the app’s `,_jsx(_components.strong,{children:`Assignments`}),` tab and add them, or add a group they belong to. Okta blocks everyone else by design, which is what makes assignment your access control for Oleria sign-in.`]})}),_jsx(Accordion,{title:`Okta reports a SAML error about the destination or audience`,id:`okta-reports-a-saml-error-about-the-destination-or-audience`,children:_jsxs(_components.p,{children:[`The `,_jsx(_components.strong,{children:`Single sign-on URL`}),` or `,_jsx(_components.strong,{children:`Audience URI (SP Entity ID)`}),` in Okta doesn’t exactly match Oleria’s `,_jsx(_components.strong,{children:`ACS URL`}),` and `,_jsx(_components.strong,{children:`Entity ID`}),`. Trailing slashes, `,_jsx(_components.code,{children:`http`}),` instead of `,_jsx(_components.code,{children:`https`}),`, and a truncated paste all count as a mismatch. Re-copy both values from `,_jsx(_components.strong,{children:`Settings → SSO Configuration`}),` in Oleria and paste them again on the app’s `,_jsx(_components.strong,{children:`Configure SAML`}),` step.`]})}),_jsxs(Accordion,{title:`Okta signs the user in, then Oleria rejects them`,id:`okta-signs-the-user-in-then-oleria-rejects-them`,children:[_jsx(_components.p,{children:`Authentication succeeded and the content of the assertion is the problem. Check, in this order:`}),_jsxs(_components.ol,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Name ID format`}),` is `,_jsx(_components.strong,{children:`Persistent`}),`, with `,_jsx(_components.strong,{children:`Application username`}),` set to `,_jsx(_components.strong,{children:`Email`}),`.`]}),`\n`,_jsxs(_components.li,{children:[`Attribute statements named exactly `,_jsx(_components.code,{children:`email`}),` and `,_jsx(_components.code,{children:`name`}),` exist, both with `,_jsx(_components.strong,{children:`Name format`}),` `,_jsx(_components.code,{children:`Unspecified`}),`.`]}),`\n`,_jsxs(_components.li,{children:[`If you turned on `,_jsx(_components.strong,{children:`Sign requests`}),`, Oleria’s request signing certificate is uploaded to Okta under `,_jsx(_components.strong,{children:`Signature Certificate`}),`, and `,_jsx(_components.strong,{children:`Signed Requests`}),` is set to `,_jsx(_components.strong,{children:`Validate SAML requests with signature certificates`}),`.`]}),`\n`,_jsxs(_components.li,{children:[`If you turned on `,_jsx(_components.strong,{children:`Encrypt SAML responses`}),`, `,_jsx(_components.strong,{children:`Assertion Encryption`}),` is set to `,_jsx(_components.strong,{children:`Encrypted`}),` and Oleria’s response encryption certificate is uploaded next to `,_jsx(_components.strong,{children:`Encryption Certificate`}),`.`]}),`\n`]}),_jsxs(_components.p,{children:[_jsx(_components.a,{href:`/administration/sso-configuration#troubleshoot-sign-in-failures`,children:`Troubleshoot sign-in failures`}),` covers the certificate cases in more detail.`]})]}),_jsx(Accordion,{title:`I can't find Attribute Statements on the Configure SAML page`,id:`i-cant-find-attribute-statements-on-the-configure-saml-page`,children:_jsxs(_components.p,{children:[`Your org is on Okta Identity Engine, where attribute statements live on the app’s `,_jsx(_components.strong,{children:`Sign On`}),` tab under `,_jsx(_components.strong,{children:`Attribute Statements`}),` rather than on `,_jsx(_components.strong,{children:`Configure SAML`}),`. Finish the SAML configuration, then add them there. Only legacy Classic Engine orgs show them on the `,_jsx(_components.strong,{children:`Configure SAML`}),` page.`]})}),_jsxs(Accordion,{title:`The user signs in successfully but has no access to Oleria`,id:`the-user-signs-in-successfully-but-has-no-access-to-oleria`,children:[_jsx(_components.p,{children:`Sign-in worked and the person has no Oleria account, or has one that’s been deactivated. SSO authenticates people; it never creates accounts. Depending on the workspace:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Main Workspace`}),` - the account has to come from SCIM or from `,_jsx(_components.a,{href:`/administration/manage-users`,children:`Manage Users`}),`.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Governance App`}),` - the same, unless you turn on `,_jsx(_components.a,{href:`/administration/sso-configuration#automatically-provision-reviewers`,children:`automatic user provisioning`}),` and add the person’s email domain to the allowed list.`]}),`\n`]})]}),_jsx(Accordion,{title:`Sign-in worked for months and suddenly stopped`,id:`sign-in-worked-for-months-and-suddenly-stopped`,children:_jsxs(_components.p,{children:[`If you pasted metadata XML instead of a URL when you first set the identity provider up, then the certificate provided in the metadata may have expired or been rotated. The XML is a snapshot rather than a live document, so changes to it are not captured by Oleria automatically.\nGet fresh metadata from the app’s `,_jsx(_components.strong,{children:`Sign On`}),` tab, then open the provider in `,_jsx(_components.strong,{children:`Settings → SSO Configuration`}),`, edit it, and save the `,_jsx(_components.strong,{children:`Identity Provider metadata`}),` XML again.`]})}),_jsx(Accordion,{title:`The user signs in but lands on a different account than SCIM provisioned`,id:`the-user-signs-in-but-lands-on-a-different-account-than-scim-provisioned`,children:_jsxs(_components.p,{children:[`The SAML `,_jsx(_components.code,{children:`email`}),` attribute statement resolves to a different address than the one SCIM provisioned, so Oleria can’t match the sign-in to the existing account. All three have to point at the same address: the `,_jsx(_components.code,{children:`email`}),` attribute statement on the `,_jsx(_components.strong,{children:`Sign On`}),` tab, `,_jsx(_components.strong,{children:`Application username`}),`, and the app’s `,_jsx(_components.code,{children:`email`}),` attribute mapping under `,_jsx(_components.strong,{children:`Provisioning → To App`}),`. See `,_jsx(_components.a,{href:`#part-2-set-up-scim`,children:`Confirm userName and email carry the same address`}),`.`]})}),_jsx(Accordion,{title:`Oleria rejects the identity provider when I add or edit it`,id:`oleria-rejects-the-identity-provider-when-i-add-or-edit-it`,children:_jsxs(_components.p,{children:[`This is an Oleria-side validation failure rather than an Okta problem: the metadata URL is unreachable, the name is already taken, or the metadata XML is incomplete. Oleria names the specific reason in the error it shows. See `,_jsx(_components.a,{href:`/administration/sso-configuration#troubleshoot-identity-provider-errors`,children:`Troubleshoot identity provider errors`}),` for every message and what to do about each.`]})}),_jsxs(Accordion,{title:`How should I test sign-in?`,id:`how-should-i-test-sign-in`,children:[_jsxs(_components.p,{children:[`Two Okta tools are useful while you configure: `,_jsx(_components.strong,{children:`Preview the SAML Assertion`}),` on the `,_jsx(_components.strong,{children:`Configure SAML`}),` step shows the exact assertion Okta will send, which is the fastest way to confirm the NameID format and the `,_jsx(_components.code,{children:`email`}),` and `,_jsx(_components.code,{children:`name`}),` attribute names without signing anyone in. The System Log shows what Okta thought happened on a real attempt.`]}),_jsxs(_components.p,{children:[`Treat signing in at `,_jsx(_components.a,{href:`https://www.oleria.com/sign-in`,children:`https://www.oleria.com/sign-in`}),` as the real test, because that’s the service-provider-initiated flow your users actually take. Launching the app from the Okta dashboard tile is a different, identity-provider-initiated flow.`]})]})]}),`\n`,_jsx(Heading,{level:`3`,id:`provisioning-troubleshooting`,children:`Provisioning troubleshooting`}),`\n`,_jsxs(AccordionGroup,{children:[_jsxs(Accordion,{title:`There's no Provisioning setting on the app`,id:`theres-no-provisioning-setting-on-the-app`,children:[_jsxs(_components.p,{children:[`In most cases your org isn’t entitled to Okta Lifecycle Management, and Okta renders no `,_jsx(_components.strong,{children:`Provisioning`}),` options at all rather than greying them out. See `,_jsx(_components.a,{href:`#okta-lifecycle-management-is-required-for-scim`,children:`Okta Lifecycle Management is required for SCIM`}),`, and `,_jsx(_components.a,{href:`#alternatives-without-lifecycle-management`,children:`Alternatives without Lifecycle Management`}),` if you can’t add it.`]}),_jsx(_components.p,{children:`Two other causes worth ruling out: you’re signed in with an admin role narrower than super admin, or the app was created through the Okta API or Terraform rather than the Admin Console, which can leave the provisioning options absent.`})]}),_jsxs(Accordion,{title:`Test API Credentials fails`,id:`test-api-credentials-fails`,children:[_jsx(_components.p,{children:`Work through the integration fields in order:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`SCIM connector base URL`}),` is Oleria’s `,_jsx(_components.strong,{children:`SCIM Base URL`}),`, not Oleria’s sign-in address.`]}),`\n`,_jsxs(_components.li,{children:[`Unique identifier is `,_jsx(_components.code,{children:`userName`}),`.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Authentication Mode`}),` is `,_jsx(_components.strong,{children:`OAuth 2`}),` with `,_jsx(_components.strong,{children:`Grant Type`}),` set to `,_jsx(_components.strong,{children:`Client Credentials`}),`, not `,_jsx(_components.strong,{children:`HTTP Header`}),`. Oleria’s SCIM API only issues short-lived tokens through this exchange and never accepts a static bearer token.`]}),`\n`,_jsxs(_components.li,{children:[`The access token endpoint is Oleria’s `,_jsx(_components.strong,{children:`OAuth Token URL`}),`.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Client ID`}),` and `,_jsx(_components.strong,{children:`Client Secret`}),` are pasted whole, with no leading or trailing spaces.`]}),`\n`]}),_jsxs(_components.p,{children:[`Confirm you copied all four values from the correct tab of `,_jsx(_components.strong,{children:`Settings → SCIM Configuration`}),`. The `,_jsx(_components.strong,{children:`Main Workspace`}),` and `,_jsx(_components.strong,{children:`Governance App`}),` have separate credentials and separate base URLs, and using one workspace’s secret against the other’s URL fails here.`]})]}),_jsxs(Accordion,{title:`Provisioning is configured but nobody appears in Oleria`,id:`provisioning-is-configured-but-nobody-appears-in-oleria`,children:[_jsx(_components.p,{children:`In rough order of likelihood:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Create Users`}),` isn’t enabled under `,_jsx(_components.strong,{children:`Provisioning → To App`}),`. Turning on SCIM doesn’t enable the individual provisioning actions.`]}),`\n`,_jsxs(_components.li,{children:[`Nobody is assigned to the app on the `,_jsx(_components.strong,{children:`Assignments`}),` tab.`]}),`\n`,_jsxs(_components.li,{children:[`You pushed a group under `,_jsx(_components.strong,{children:`Push Groups`}),` but never assigned it. Pushing a group creates the group in Oleria; assignment is what provisions the people in it. They’re separate actions on separate tabs.`]}),`\n`,_jsxs(_components.li,{children:[`The push failed and is waiting in the Admin Console’s `,_jsx(_components.strong,{children:`Tasks`}),` page, or recorded as an error in `,_jsx(_components.strong,{children:`Reports → System Log`}),`.`]}),`\n`]})]}),_jsxs(Accordion,{title:`Users sync but groups don't (Main Workspace)`,id:`users-sync-but-groups-dont-main-workspace`,children:[_jsx(_components.p,{children:`Three causes, all common:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Push Groups`}),` wasn’t checked in the app’s `,_jsx(_components.strong,{children:`Provisioning → Integration`}),` settings, so Okta never pushes groups at all.`]}),`\n`,_jsxs(_components.li,{children:[`The group hasn’t been added on the `,_jsx(_components.strong,{children:`Push Groups`}),` tab. Okta pushes only the groups you list there, one at a time, not every group in the org.`]}),`\n`,_jsxs(_components.li,{children:[`Group provisioning requires Lifecycle Management, exactly as user provisioning does. See `,_jsx(_components.a,{href:`#okta-lifecycle-management-is-required-for-scim`,children:`Okta Lifecycle Management is required for SCIM`}),`.`]}),`\n`]}),_jsxs(_components.p,{children:[`Use `,_jsx(_components.strong,{children:`Push now`}),` on the `,_jsx(_components.strong,{children:`Push Groups`}),` tab to force an immediate push once the setup is right.`]})]}),_jsxs(Accordion,{title:`Provisioned users have the wrong role, or no access (Main Workspace)`,id:`provisioned-users-have-the-wrong-role-or-no-access-main-workspace`,children:[_jsxs(_components.p,{children:[`Oleria grants roles through group membership, never on the user record, and Okta’s Push Groups can’t set a role on the group it creates. Until you map it, its members fall back to Oleria’s read-only `,_jsx(_components.code,{children:`analyst`}),` role.`]}),_jsxs(_components.p,{children:[`In Oleria, go to `,_jsx(_components.strong,{children:`Settings → Manage Users`}),`, select the `,_jsx(_components.strong,{children:`Groups`}),` tab, select the group, click `,_jsx(_components.strong,{children:`Change role`}),`, and choose the role it should grant. Every current and future member inherits it. See `,_jsx(_components.a,{href:`/administration/scim-user-provisioning#how-oleria-maps-roles-and-groups`,children:`How Oleria maps roles and groups`}),`.`]}),_jsxs(_components.p,{children:[`This doesn’t apply to the `,_jsx(_components.strong,{children:`Governance App`}),`, where every provisioned user gets the `,_jsx(_components.code,{children:`reviewer`}),` role automatically.`]})]}),_jsxs(Accordion,{title:`Someone I deactivated or unassigned in Okta still has access to Oleria`,id:`someone-i-deactivated-or-unassigned-in-okta-still-has-access-to-oleria`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Deactivate Users`}),` has to be enabled under `,_jsx(_components.strong,{children:`Provisioning → To App`}),`. Without it, Okta pushes creates and updates but never tells Oleria to disable anyone, so unassigning someone in Okta silently leaves their Oleria account active.`]}),_jsxs(_components.p,{children:[`With it enabled, the change travels within a minute or two. Confirm it in `,_jsx(_components.strong,{children:`Reports → System Log`}),`, then in `,_jsx(_components.a,{href:`/administration/manage-users`,children:`Manage Users`}),`. If nothing happened, check that the person was removed from every group assigned to the app, not just one.`]})]}),_jsxs(Accordion,{title:`Provisioned users have a wrong username or email address`,id:`provisioned-users-have-a-wrong-username-or-email-address`,children:[_jsxs(_components.p,{children:[`Okta sends the app username as `,_jsx(_components.code,{children:`userName`}),`, and the app username format is set per app. If your users arrive in Oleria identified by their Okta username rather than their email, set `,_jsx(_components.strong,{children:`Application username`}),` to `,_jsx(_components.strong,{children:`Email`}),` on the app’s `,_jsx(_components.strong,{children:`Sign On`}),` tab, which also keeps SSO and SCIM identifying people the same way.`]}),_jsxs(_components.p,{children:[`For any other attribute that arrives wrong, check the profile mappings under `,_jsx(_components.strong,{children:`Provisioning → To App`}),`, then push one affected user again rather than waiting for their next change.`]})]}),_jsxs(Accordion,{title:`Provisioning reports duplicate or conflict errors, or provisioned users never update`,id:`provisioning-reports-duplicate-or-conflict-errors-or-provisioned-users-never-update`,children:[_jsxs(_components.p,{children:[`Okta matches existing users on `,_jsx(_components.code,{children:`userName`}),`. If the address Okta sends as `,_jsx(_components.code,{children:`userName`}),` doesn’t match the one Oleria stored, Okta can’t find the account it already created and tries to create it again, which Oleria rejects as a duplicate.`]}),_jsxs(_components.p,{children:[`Confirm `,_jsx(_components.strong,{children:`Application username`}),` is `,_jsx(_components.strong,{children:`Email`}),` and that the app’s `,_jsx(_components.code,{children:`email`}),` attribute maps to `,_jsx(_components.code,{children:`user.email`}),`, so `,_jsx(_components.code,{children:`userName`}),` and `,_jsx(_components.code,{children:`emails`}),` agree. See `,_jsx(_components.a,{href:`#part-2-set-up-scim`,children:`Confirm userName and email carry the same address`}),`.`]})]})]}),`\n`,_jsxs(_components.p,{children:[`For the request and response shape of every SCIM endpoint, see the `,_jsx(_components.a,{href:`/administration/scim-user-provisioning`,children:`SCIM user provisioning`}),` and `,_jsx(_components.a,{href:`/administration/scim-governance-provisioning`,children:`Governance App SCIM provisioning`}),` reference pages.`]}),`\n`,_jsx(Heading,{level:`2`,id:`contact-us`,children:`Contact us`}),`\n`,_jsxs(_components.p,{children:[`For questions, contact us at `,_jsx(_components.a,{href:`mailto:support@oleria.com`,children:`support@oleria.com`}),`.`]})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"config":{},"pageMetadata":{"title":"Okta: end-to-end SSO and SCIM setup","description":"Connect Okta to Oleria for single sign-on and user provisioning, covering both the Main Workspace and the Governance App.","href":"/administration/okta-sso-scim-setup"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[{"title":"Overview","slug":"overview","depth":2,"children":[{"title":"Main Workspace vs. Governance App","slug":"main-workspace-vs-governance-app","depth":3,"children":[]},{"title":"SSO vs. SCIM vs. automatic user provisioning","slug":"sso-vs-scim-vs-automatic-user-provisioning","depth":3,"children":[]},{"title":"Possible provisioning flows","slug":"possible-provisioning-flows","depth":3,"children":[]}]},{"title":"Prerequisites","slug":"prerequisites","depth":2,"children":[]},{"title":"Part 1: Set up SSO","slug":"part-1-set-up-sso","depth":2,"children":[]},{"title":"Part 2: Set up SCIM","slug":"part-2-set-up-scim","depth":2,"children":[{"title":"Okta Lifecycle Management is required for SCIM","slug":"okta-lifecycle-management-is-required-for-scim","depth":3,"children":[]}]},{"title":"Alternatives without Lifecycle Management","slug":"alternatives-without-lifecycle-management","depth":2,"children":[]},{"title":"Set up the second workspace","slug":"set-up-the-second-workspace","depth":2,"children":[]},{"title":"FAQ","slug":"faq","depth":2,"children":[{"title":"Okta and identity provider basics","slug":"okta-and-identity-provider-basics","depth":3,"children":[]},{"title":"Sign-in troubleshooting","slug":"sign-in-troubleshooting","depth":3,"children":[]},{"title":"Provisioning troubleshooting","slug":"provisioning-troubleshooting","depth":3,"children":[]}]},{"title":"Contact us","slug":"contact-us","depth":2,"children":[]}],"codeExamples":{}},"jsLinks":[],"subdomain":"oleria","siteName":"Oleria Identity Security","title":"Okta: end-to-end SSO and SCIM setup - Oleria Identity Security","navMaps":{"firstHrefInVersion":{},"firstHrefInLanguage":{}},"lastModified":"2026-09-23T18:16:53.953Z","originalFileLocation":"administration/okta-sso-scim-setup.mdx"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"light\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"Connect Okta to Oleria for single sign-on and user provisioning, covering both the Main Workspace and the Governance App.\">\u003cmeta data-mint-head name=\"application-name\" content=\"Oleria Identity Security\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"Okta: end-to-end SSO and SCIM setup - Oleria Identity Security\">\u003cmeta data-mint-head property=\"og:description\" content=\"Connect Okta to Oleria for single sign-on and user provisioning, covering both the Main Workspace and the Governance App.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"Oleria Identity Security\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://docs.oleria.com/administration/okta-sso-scim-setup\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://oleria.mintlify.app/_mintlify/api/og/v2?division=Identity+Provider+Setup+Guides\u0026amp;title=Okta%3A+end-to-end+SSO+and+SCIM+setup\u0026amp;description=Connect+Okta+to+Oleria+for+single+sign-on+and+user+provisioning%2C+covering+both+the+Main+Workspace+and+the+Governance+App.\u0026amp;theme=67101527a6023bf85b2b7e70\u0026amp;signature=872246c3fead8fe257a2ca06db28ed1dae66eddbea52e77c16c5597ea7e381d6\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"Okta: end-to-end SSO and SCIM setup - Oleria Identity Security\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"Connect Okta to Oleria for single sign-on and user provisioning, covering both the Main Workspace and the Governance App.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://oleria.mintlify.app/_mintlify/api/og/v2?division=Identity+Provider+Setup+Guides\u0026amp;title=Okta%3A+end-to-end+SSO+and+SCIM+setup\u0026amp;description=Connect+Okta+to+Oleria+for+single+sign-on+and+user+provisioning%2C+covering+both+the+Main+Workspace+and+the+Governance+App.\u0026amp;theme=67101527a6023bf85b2b7e70\u0026amp;signature=872246c3fead8fe257a2ca06db28ed1dae66eddbea52e77c16c5597ea7e381d6\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/mintlify-assets/_mintlify/favicons/oleria/VFsEjt_GQ9jb2s6K/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"Oleria Identity Security\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#027864\">\u003clink data-mint-head rel=\"canonical\" href=\"https://docs.oleria.com/administration/okta-sso-scim-setup\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/administration/okta-sso-scim-setup.md\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://docs.oleria.com/#organization\",\"name\":\"Oleria Identity Security\",\"url\":\"https://docs.oleria.com\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/oleria/KyPIHO-0OF6fE_DF/images/OleriaLightMode-1.png?fit=max\u0026auto=format\u0026n=KyPIHO-0OF6fE_DF\u0026q=85\u0026s=906d33a8c505e2a96b7c6a1583335e1d\"}},{\"@type\":\"WebSite\",\"@id\":\"https://docs.oleria.com#website\",\"name\":\"Oleria Identity Security\",\"url\":\"https://docs.oleria.com\",\"publisher\":{\"@id\":\"https://docs.oleria.com/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://docs.oleria.com/administration/okta-sso-scim-setup#webpage\",\"url\":\"https://docs.oleria.com/administration/okta-sso-scim-setup\",\"name\":\"Okta: end-to-end SSO and SCIM setup\",\"description\":\"Connect Okta to Oleria for single sign-on and user provisioning, covering both the Main Workspace and the Governance App.\",\"dateModified\":\"2026-09-23T18:16:53.953Z\",\"isPartOf\":{\"@id\":\"https://docs.oleria.com#website\"},\"breadcrumb\":{\"@id\":\"https://docs.oleria.com/administration/okta-sso-scim-setup#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://docs.oleria.com/administration/okta-sso-scim-setup#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Administration\",\"item\":\"https://docs.oleria.com/administration/user-management-overview\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Okta: end-to-end SSO and SCIM setup\",\"item\":\"https://docs.oleria.com/administration/okta-sso-scim-setup\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://docs.oleria.com/administration/okta-sso-scim-setup#article\",\"headline\":\"Okta: end-to-end SSO and SCIM setup\",\"name\":\"Okta: end-to-end SSO and SCIM setup\",\"description\":\"Connect Okta to Oleria for single sign-on and user provisioning, covering both the Main Workspace and the Governance App.\",\"url\":\"https://docs.oleria.com/administration/okta-sso-scim-setup\",\"mainEntityOfPage\":{\"@id\":\"https://docs.oleria.com/administration/okta-sso-scim-setup#webpage\"},\"dateModified\":\"2026-09-23T18:16:53.953Z\",\"publisher\":{\"@id\":\"https://docs.oleria.com/#organization\"},\"isPartOf\":{\"@id\":\"https://docs.oleria.com#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"Oleria Identity Security\",\"creator\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","siteName":"Oleria Identity Security","nav":{"global":null,"tabs":[{"tab":"Product","groups":[{"group":"Getting Started","pages":[{"title":"Oleria Identity Security","href":"/introduction/overview"},{"title":"Oleria AI","href":"/posture/oleria-ai"},{"group":"Oleria MCP","pages":[{"title":"Connect to Oleria MCP","href":"/introduction/oleria-mcp-setup"},{"title":"Oleria MCP tools","href":"/introduction/oleria-mcp-tools"},{"title":"What you can ask Oleria MCP","href":"/introduction/oleria-mcp-examples"}]}]},{"group":"Posture","pages":[{"title":"Adaptive Security","href":"/posture/oleria-adaptive-security-overview"},{"title":"Risk Monitoring","href":"/posture/risk-monitoring-overview"},{"group":"Access Graph","pages":[{"title":"Access Graph","href":"/posture/access-graph-overview"},{"title":"Read the Access Graph","href":"/posture/explore-access-graph"},{"title":"Navigate and search the Access Graph","href":"/posture/navigate-access-graph"}]},{"group":"Activity Analysis","pages":[{"title":"Activity Analysis","href":"/posture/activity-analysis-overview"},{"title":"Activity dashboard","href":"/posture/activity-dashboard"},{"title":"Activity details","href":"/posture/activity-details"}]},{"group":"Access Inventory","pages":[{"title":"Access Inventory","href":"/posture/access-inventory-overview"},{"title":"Using Access Inventory","href":"/posture/learn-access-inventory"}]},{"group":"Workflows","pages":[{"title":"Overview","href":"/posture/workflows-overview"},{"title":"Workflow templates","href":"/posture/workflow-templates"},{"title":"Disable dormant accounts","href":"/posture/disable-dormant-accounts-workflow"},{"title":"Security insights email","href":"/posture/security-insights-email-workflow"},{"title":"Enforce MFA compliance","href":"/posture/enforce-mfa-compliance-workflow"},{"title":"Manage stale SharePoint sites","href":"/posture/manage-stale-sharepoint-sites-workflow"},{"title":"NHI ownership assignment","href":"/posture/nhi-ownership-assignment-workflow"},{"title":"How Oleria assigns NHI ownership","href":"/posture/nhi-ownership-assignment-logic"},{"title":"NHI credential expiry","href":"/posture/nhi-credential-expiry-workflow"},{"title":"NHI review","href":"/posture/nhi-review-workflow"},{"title":"Detect and report Shadow IT","href":"/posture/detect-report-shadow-it-workflow"}]}]},{"group":"Governance","pages":[{"group":"Access Requests","pages":[{"title":"Access Requests","href":"/governance/access-requests"},{"title":"Approval Chains","href":"/governance/approval-chains"},{"title":"SSO Applications","href":"/governance/sso-applications"},{"title":"Integrated Applications","href":"/governance/integrated-applications"},{"title":"Custom Access","href":"/governance/custom-access"}]},{"group":"Access Reviews","pages":[{"title":"Access Reviews","href":"/governance/access-review"},{"title":"Employee access insights","href":"/governance/employee-access-insights"}]},{"group":"Account Hygiene","pages":[{"title":"Account Hygiene","href":"/governance/account-hygiene-overview"},{"title":"Password age","href":"/governance/last-password-change-insights"}]},{"title":"Application Hygiene","href":"/governance/application-hygiene-overview"},{"title":"Dormancy thresholds","href":"/governance/account-dormant-days"},{"group":"Employee Lifecycle","pages":[{"title":"Joiner","href":"/governance/employee-lifecycle-joiner"},{"title":"Mover","href":"/governance/employee-lifecycle-mover"},{"title":"Leaver","href":"/governance/employee-lifecycle-leaver"},{"title":"Access Bundles","href":"/governance/access-bundles-and-adaptive-recommendations"},{"title":"Access Bundle Presets","href":"/governance/access-bundle-presets"}]},{"title":"External access","href":"/governance/external-access"},{"title":"Group Hygiene","href":"/governance/group-hygiene-overview"},{"group":"Remediations","pages":[{"title":"Remediations","href":"/governance/remediations-overview"},{"title":"View remediation actions","href":"/governance/view-remediation-actions"},{"title":"Disable dormant accounts","href":"/governance/disable-dormant-accounts"},{"title":"Revoke external user access","href":"/governance/revoke-external-users-access-permissions"},{"title":"Remove an account from a group","href":"/governance/remove-account-from-group"}]}]},{"group":"Administration","pages":[{"title":"User management","href":"/administration/user-management-overview"},{"title":"Default user roles","href":"/administration/default-user-roles"},{"title":"Manage users","href":"/administration/manage-users"},{"title":"Update a user's role","href":"/administration/update-a-users-role"},{"title":"Remove a user","href":"/administration/remove-a-user"},{"title":"SCIM user provisioning","href":"/administration/scim-user-provisioning"},{"title":"Governance App SCIM provisioning","href":"/administration/scim-governance-provisioning"},{"title":"User attributes","href":"/administration/user-attributes"},{"title":"User profile settings","href":"/administration/user-profile-settings"},{"title":"Business rules","href":"/administration/workspace-settings-business-rules"},{"title":"Authentication methods","href":"/administration/authentication-methods"},{"title":"SSO configuration","description":"Let workspace users sign in with your identity provider using SAML single sign-on or social login, and provision governance reviewers automatically.","href":"/administration/sso-configuration"},{"group":"Identity Provider Setup Guides","pages":[{"title":"Okta: end-to-end SSO and SCIM setup","href":"/administration/okta-sso-scim-setup"},{"title":"Microsoft Entra ID: end-to-end SSO and SCIM setup","description":"Connect Microsoft Entra ID to Oleria for single sign-on and SCIM provisioning, covering both the Main Workspace and the Governance App, and Entra's one-Entity-ID-per-app rule.","href":"/administration/entra-sso-scim-setup"}]},{"title":"Email notifications","href":"/administration/email-notifications"},{"title":"Webhooks","href":"/administration/webhooks"},{"title":"Ticketing","href":"/workspace/ticketing-overview"},{"title":"Audit log","href":"/governance/audit-log-overview"}]},{"group":"Support","pages":[{"title":"Support","href":"/support/overview"},{"title":"Help","href":"/support/help"}]}]},{"tab":"Integrations","pages":[{"title":"Integrations","href":"/integrations/overview"}]},{"tab":"API Reference","pages":[{"title":"API Reference","href":"/developer-docs/api-reference/overview"}]},{"tab":"What's New","pages":[{"title":"What's New","href":"/release-notes"}]}]},"basePath":"","title":"Okta: end-to-end SSO and SCIM setup - Oleria Identity Security","buildId":"dpl_345ReqzYaAjzS9QpeJemsKdb7KDj","deploymentId":"dpl_345ReqzYaAjzS9QpeJemsKdb7KDj","dynamics":["a74be98ba7"],"chunks":["zoom-image-lightbox-B4-wUcHm.js","lightbox-handle-r17bVUz3.js"]}