

Overview
Main Workspace vs. Governance App
Oleria has two independent surfaces, each with its own sign-in and provisioning configuration:- Main Workspace - where administrators, operators, and analysts run Oleria itself: posture, access graph, workflows, and settings.
- Governance App - a separate portal where reviewers and approvers complete access reviews, act on access requests, and work governance queues. Governance app users are a distinct population from workspace users, typically much larger (anyone in the org who might approve or review something), and usually don’t need any other access to Oleria.
SSO vs. SCIM vs. automatic user provisioning
Oleria has three related but independent mechanisms. SSO is for authentication only, where as SCIM and automatic user provisioning are for provisioning.Possible provisioning flows
Because these mechanisms are independent, and each applies per workspace (Main Workspace vs Governance App), several combinations are all valid. Pick the one that matches what you’re trying to achieve before you start:Entra’s one-app-per-Entity-ID rule
Microsoft Entra requires every SAML relying party - every enterprise application configured for SAML SSO - to have a unique Entity ID (Identifier) within the tenant:“There cannot be two applications in a single Microsoft Entra tenant with the same entity identifier.” - Microsoft LearnEntra enforces this because it uses the Entity ID to work out which application should receive a given SAML response; without a unique identifier per app, it can’t disambiguate. This is sometimes described as one Entity ID per “relying party trust” (RPT) - that’s not a separate object you configure, it’s just what Entra calls an application once it’s set up for SAML SSO. Every enterprise app with SAML SSO configured is a relying party trust; there’s no way to do SAML SSO without one, and no way around the uniqueness rule by avoiding the term. This collides with Oleria’s design: as the SSO configuration page notes, the Main Workspace and Governance App tabs show the same Entity ID and ACS URL, because they share one Oleria service provider. If you create two separate Entra enterprise apps - one per Oleria workspace - both need Oleria’s Entity ID, and Entra will reject the second one with an error like “please enter an identifier which is unique within your organization.” The fix: use a single Entra enterprise application for both workspaces, rather than creating two. Complete Part 1 once to create that one app, then when you reach the SSO Configuration Governance App tab in Oleria, add its identity provider using the same Entra app’s federation metadata URL instead of creating a second app. One Entra app, one Entity ID, satisfies Entra’s rule, and both Oleria workspaces get a working IdP.
Prerequisites
- Administrator access to your Oleria workspace, and Global Administrator (or equivalent) access in Entra to create and configure enterprise applications.
- Decide which workspace(s) - Main Workspace, Governance App, or both - you’re connecting Entra to, and whether you want SSO, SCIM, or both for each. See Possible provisioning flows above.
- For SCIM into the Main Workspace: know which Oleria roles (
admin,operator,analyst,governance-operator,identity-lifecycle-operator) your Entra groups should map to. See How Oleria maps roles and groups. - For SCIM: a Microsoft Entra ID P1 or P2 license. Automatic provisioning is a premium Entra feature, and provisioning groups - which is how the Main Workspace grants roles - requires P1 at minimum. Check this before you start. See Entra ID P1 or P2 is required for SCIM below. SSO (Part 1) works on Entra ID Free, except for token encryption, which also needs P1 or P2.
Part 1: Set up SSO
Open Oleria's SSO configuration page
Create the Entra enterprise application
Oleria) - if you plan to share this one app across both workspace, avoid naming it after just one workspace.Copy Oleria's SP details into Entra
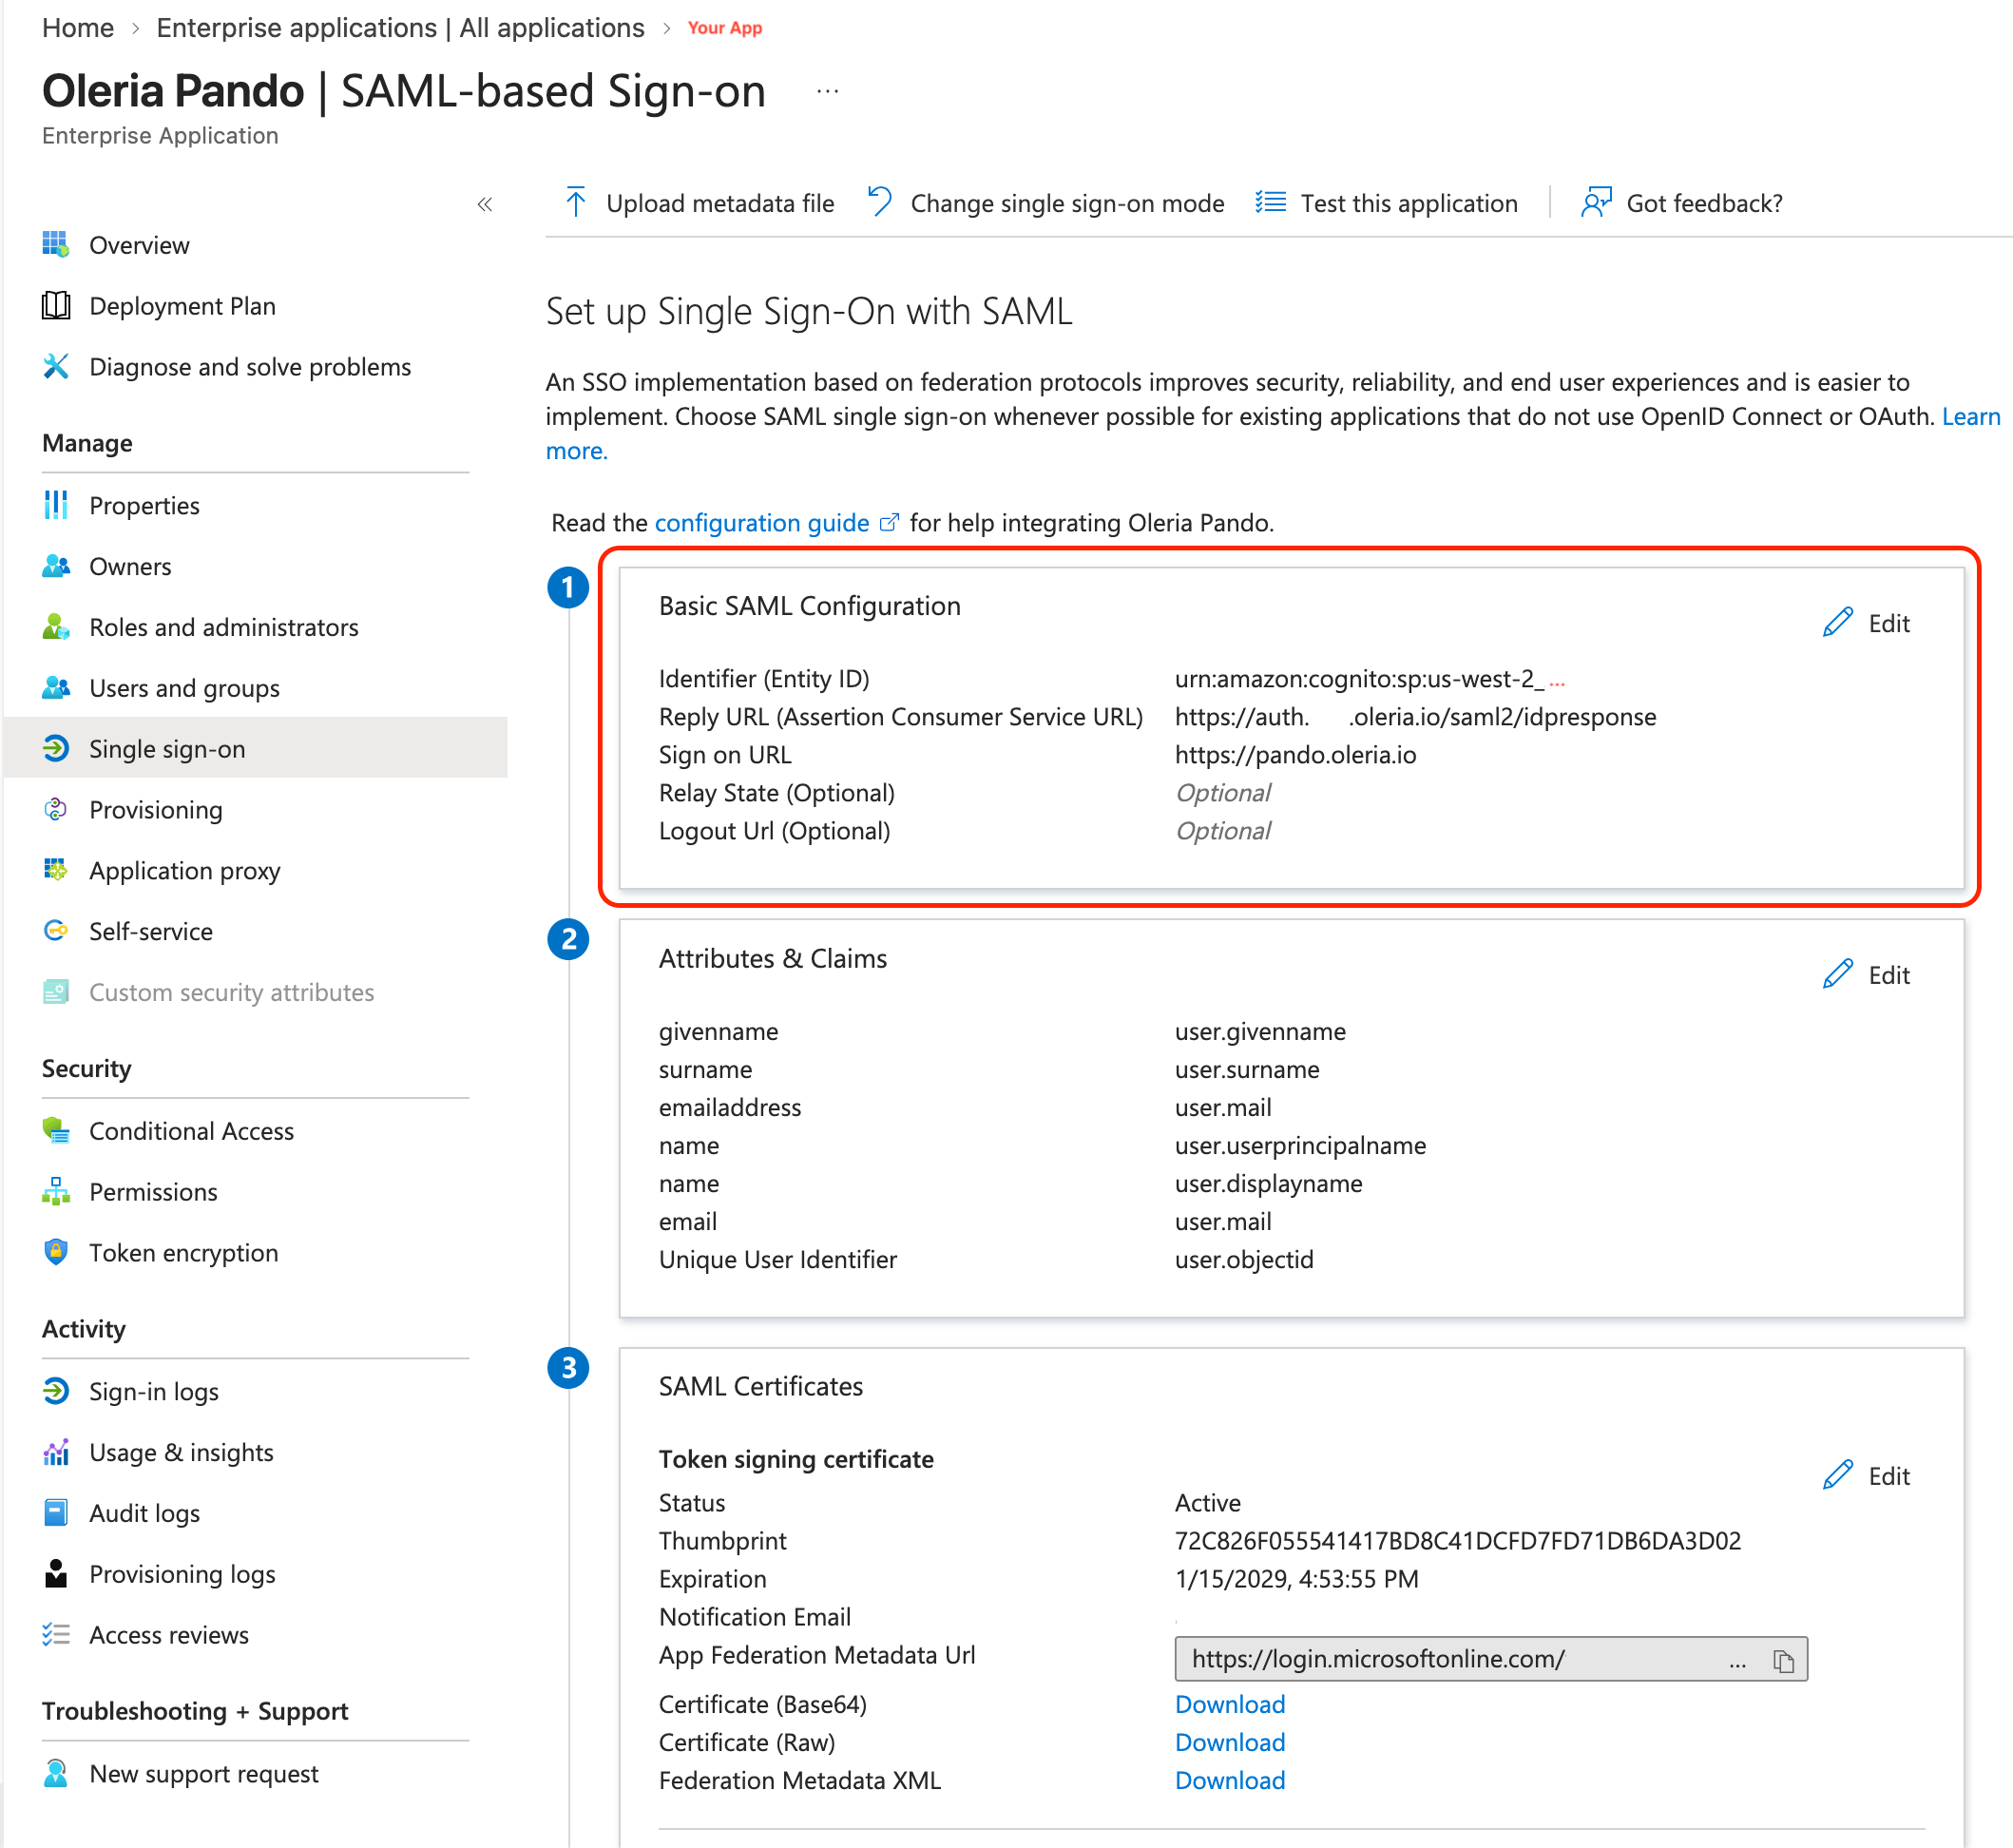
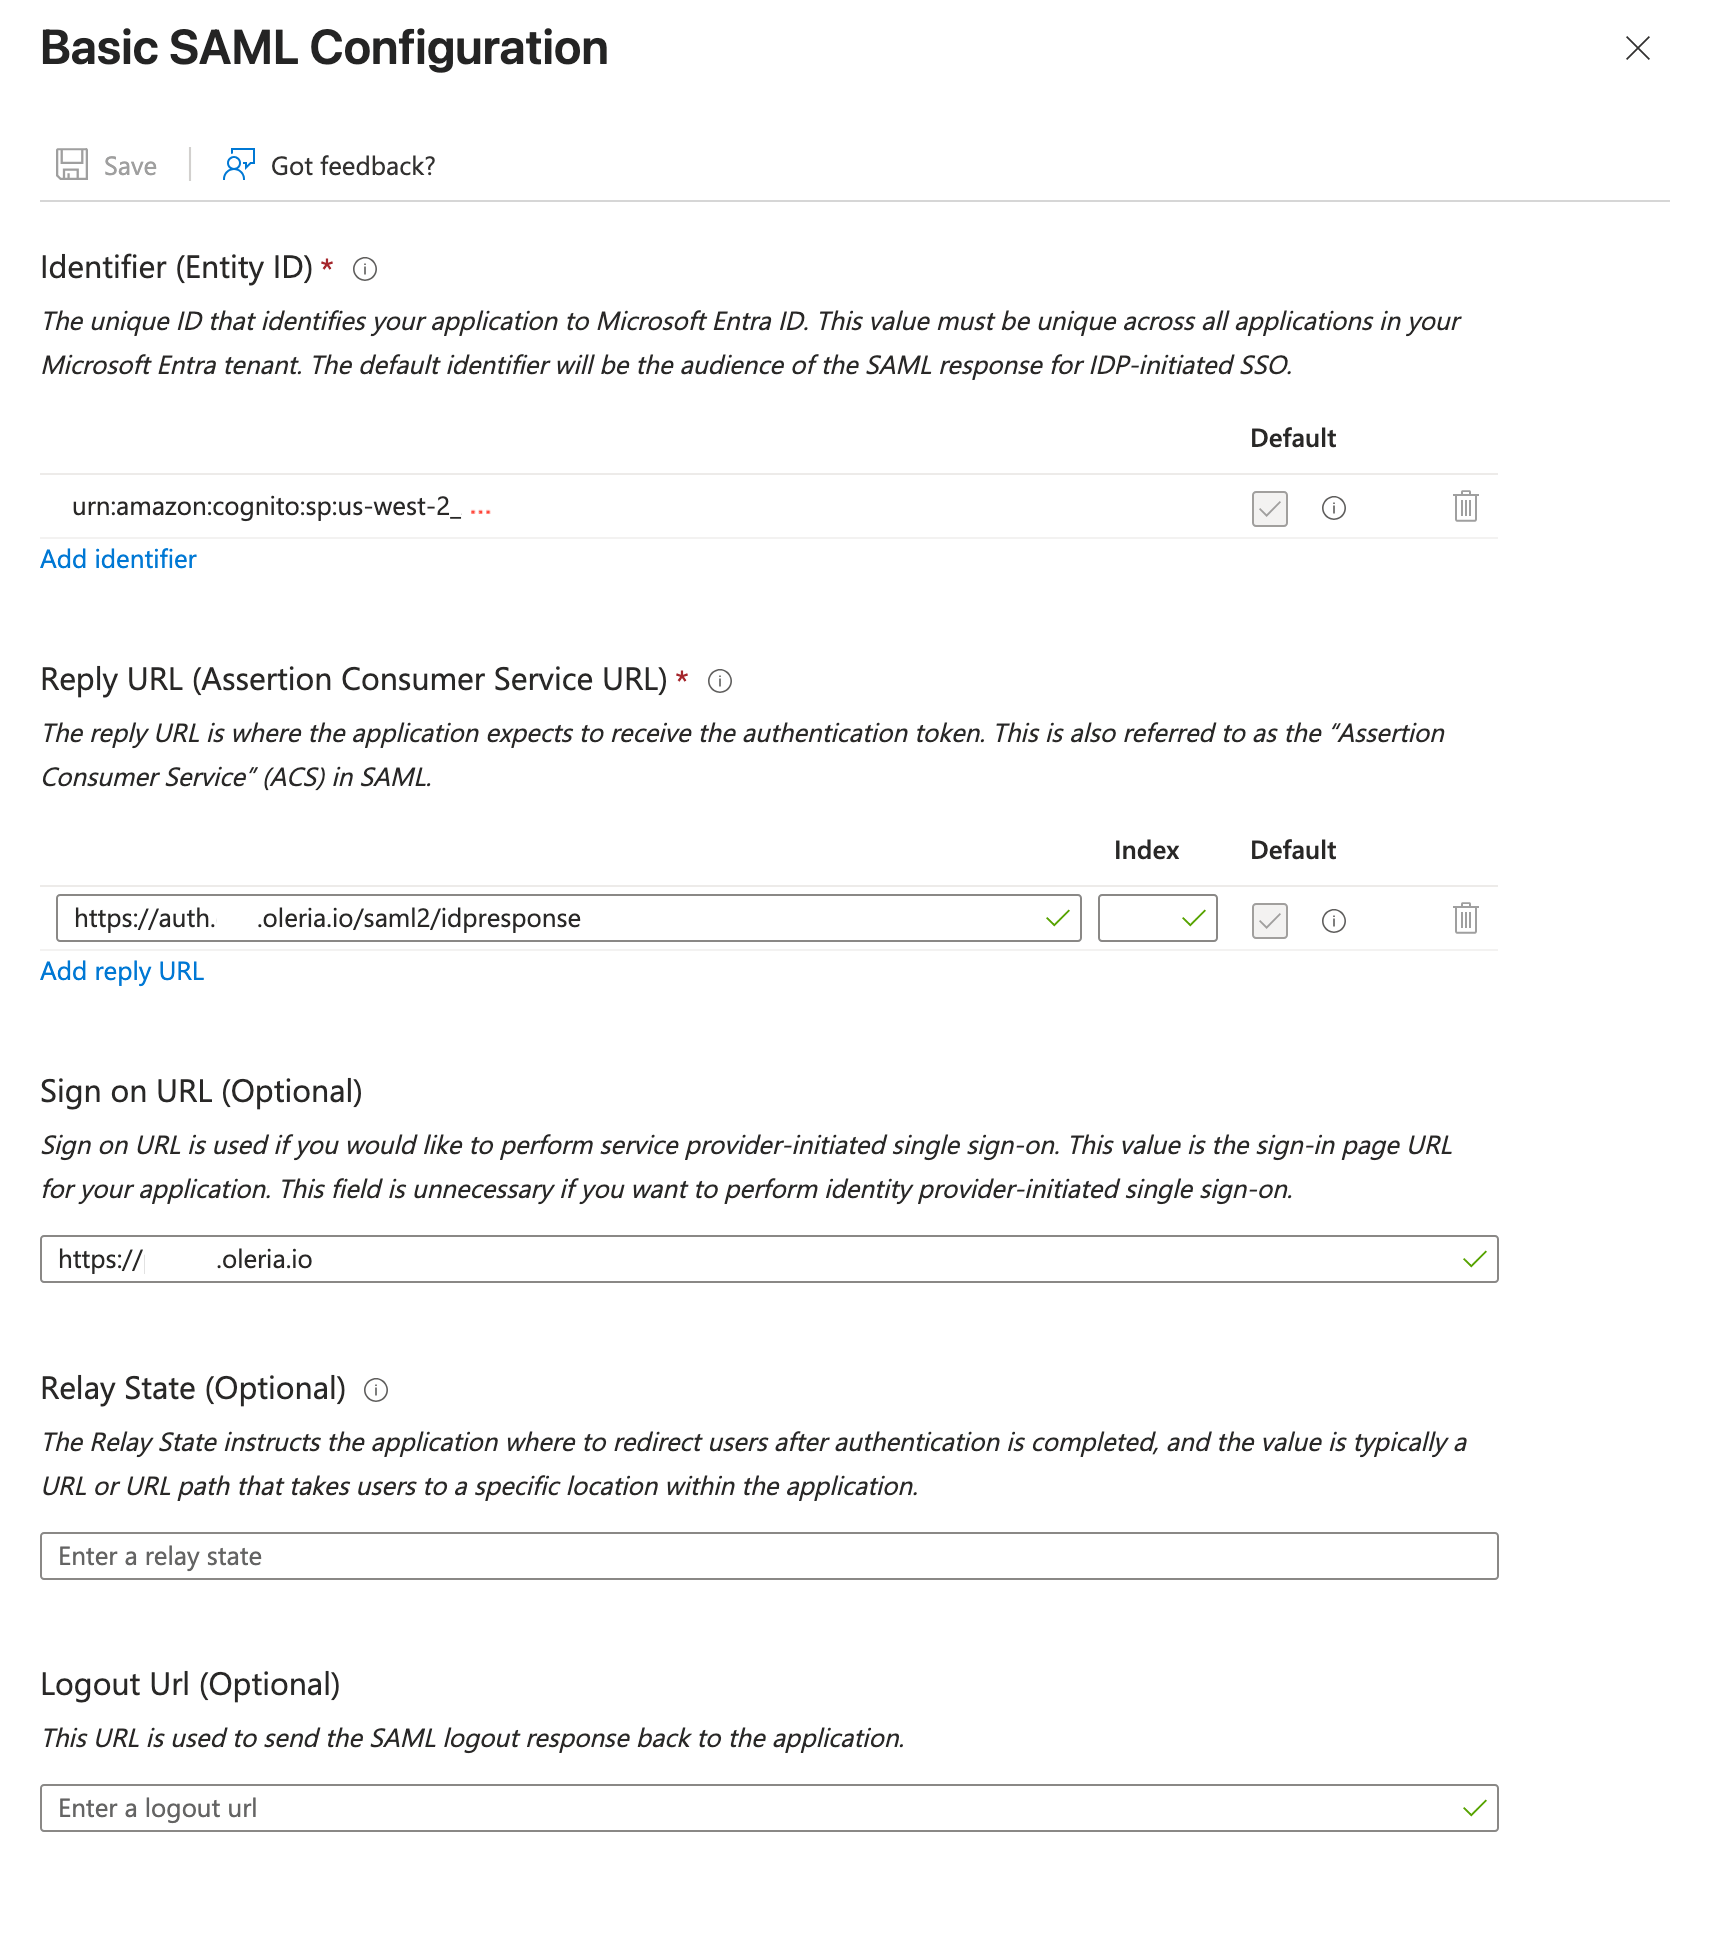
Configure the NameID and required claims
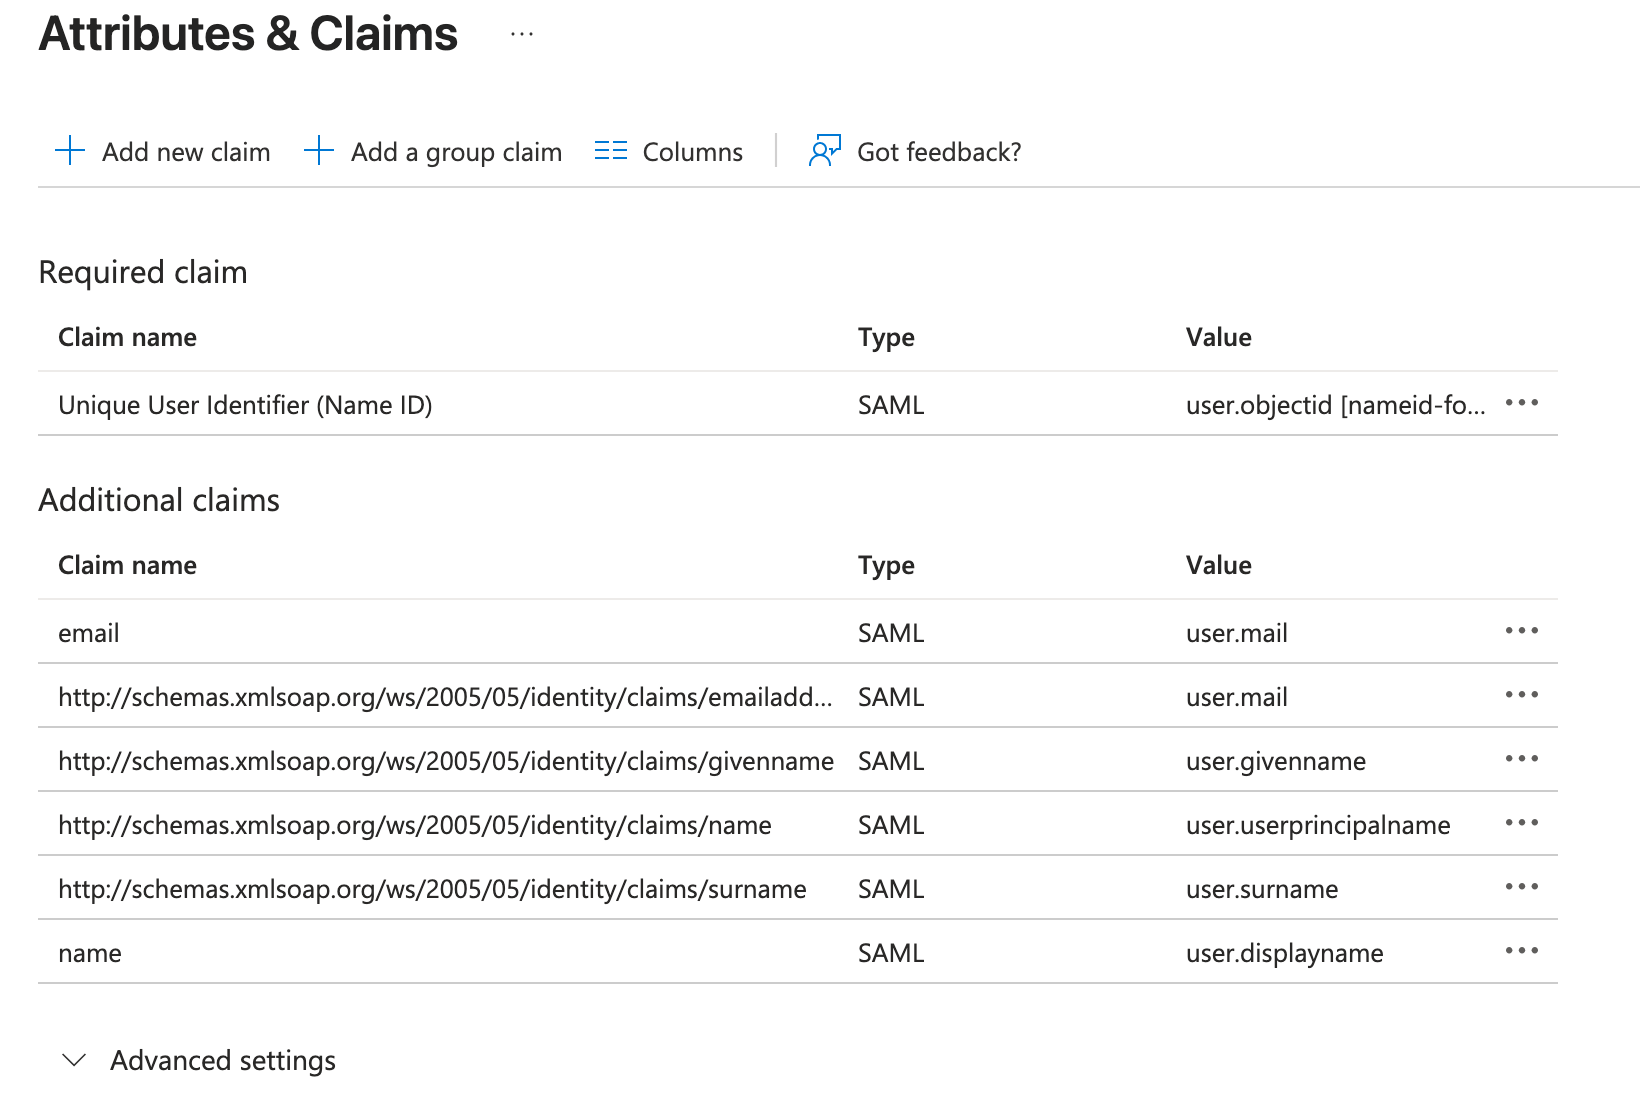
- Edit the Unique User Identifier (Name ID) claim, set Name identifier format to Persistent, and set the Source attribute to
user.objectid(or another stable, opaque identifier). - Add a new claim named
emailwith source attributeuser.mail, and another namednamewith source attributeuser.displayname. Leave Namespace blank on both - Oleria requires these two exact, short claim names. - If some users have no
mailvalue, add a Claim transformation to theemailclaim: sourceuser.mail, transformation IfEmpty, parameteruser.userprincipalname. That way every user gets an address in the claim.
Assign users and grab the metadata
Enter the SAML IdP details in Oleria
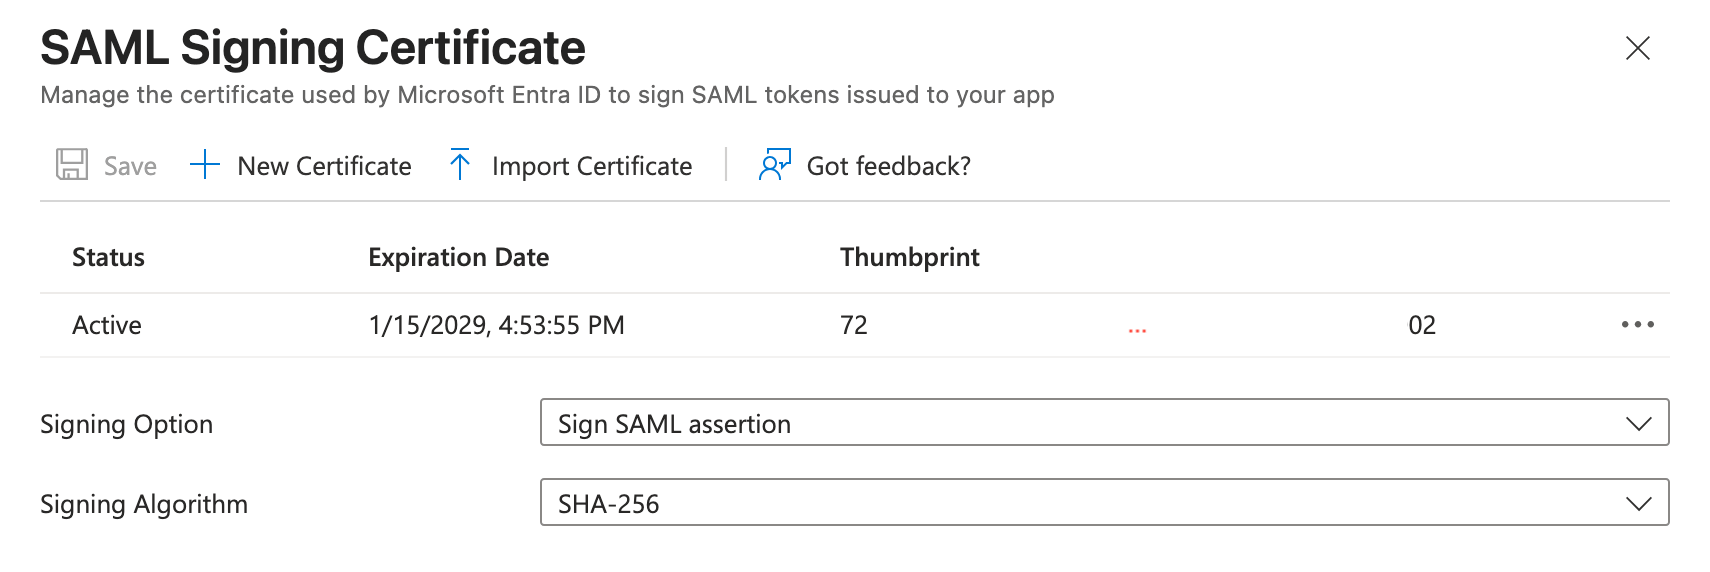
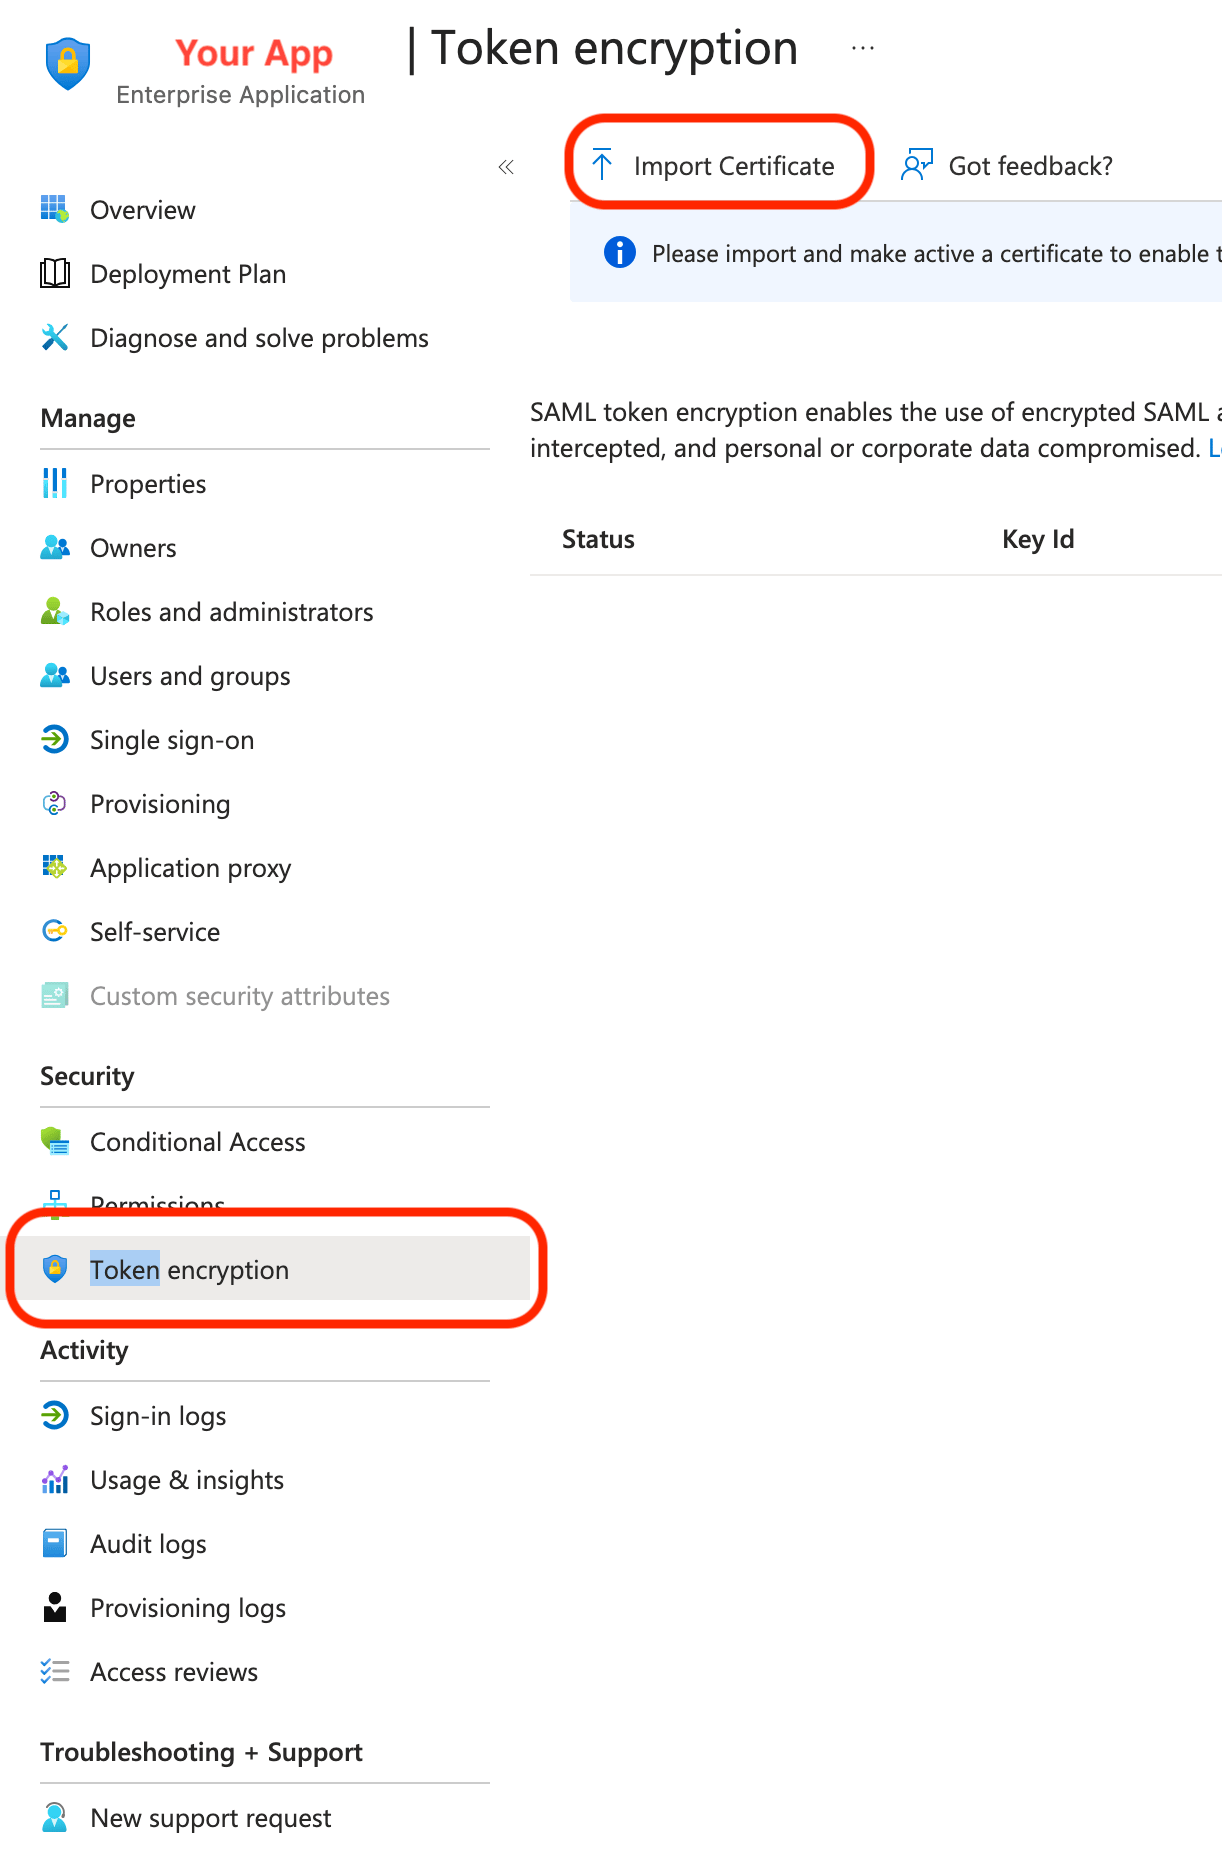
If you turned on Sign requests: upload the request signing certificate to Entra
If you turned on Encrypt SAML responses: download and upload the response encryption certificate
Confirm sign-in works
Part 2: Set up SCIM
Entra ID P1 or P2 is required for SCIM
Get Oleria's SCIM credentials
Open the Provisioning tab
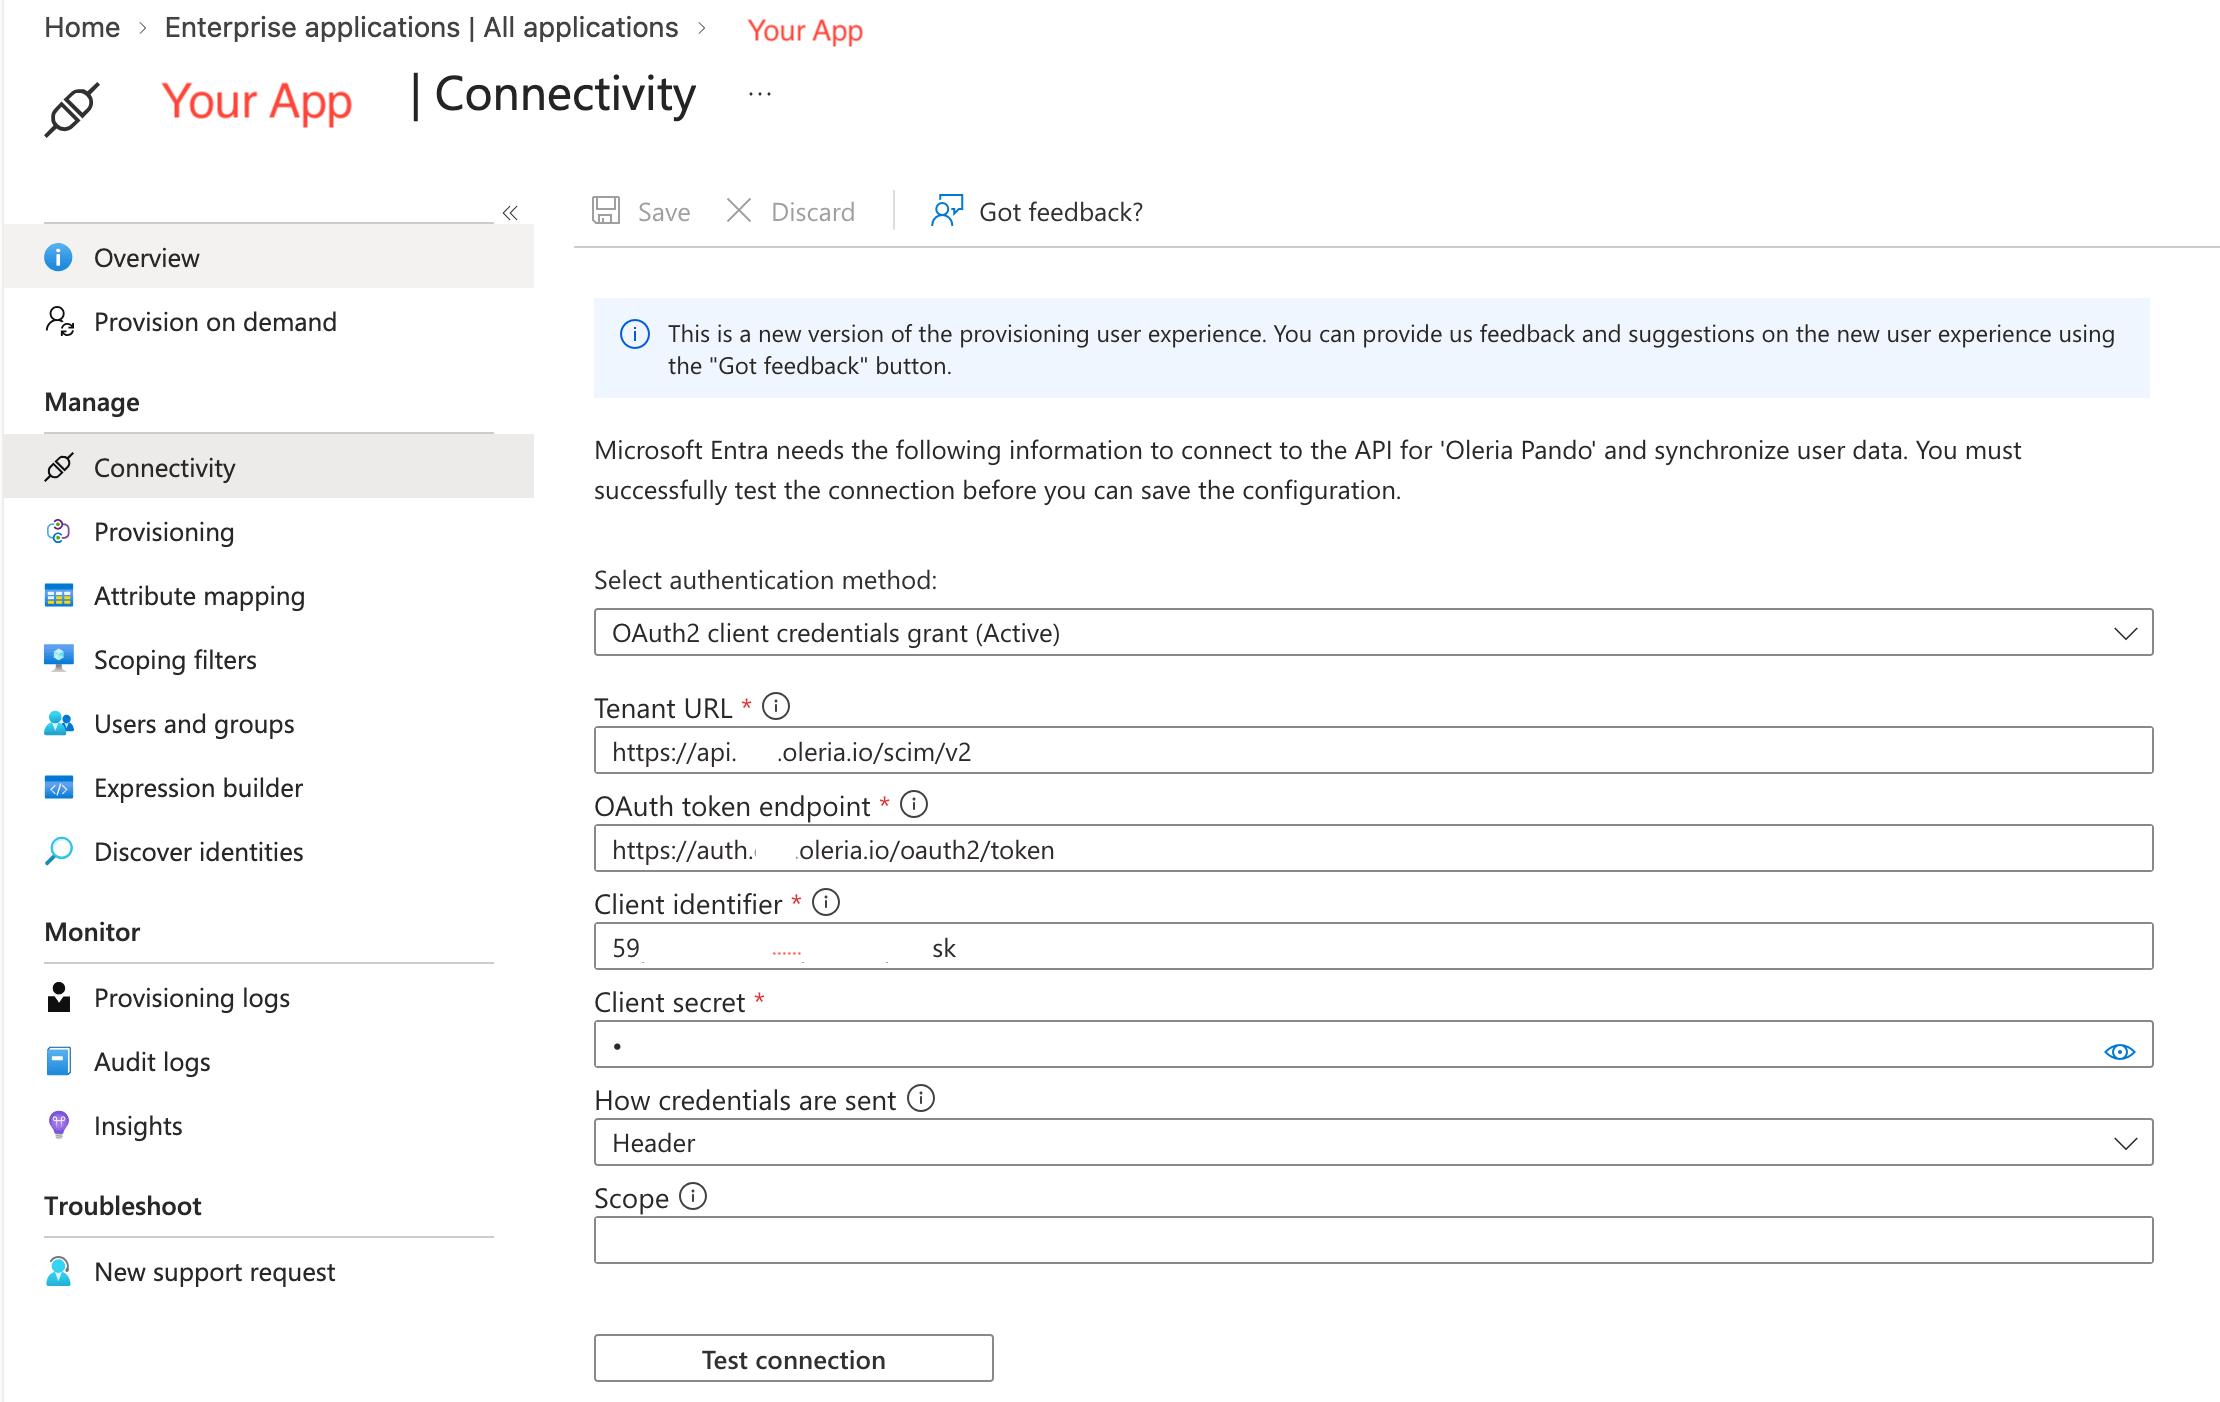
Enter the SCIM Connectivity details
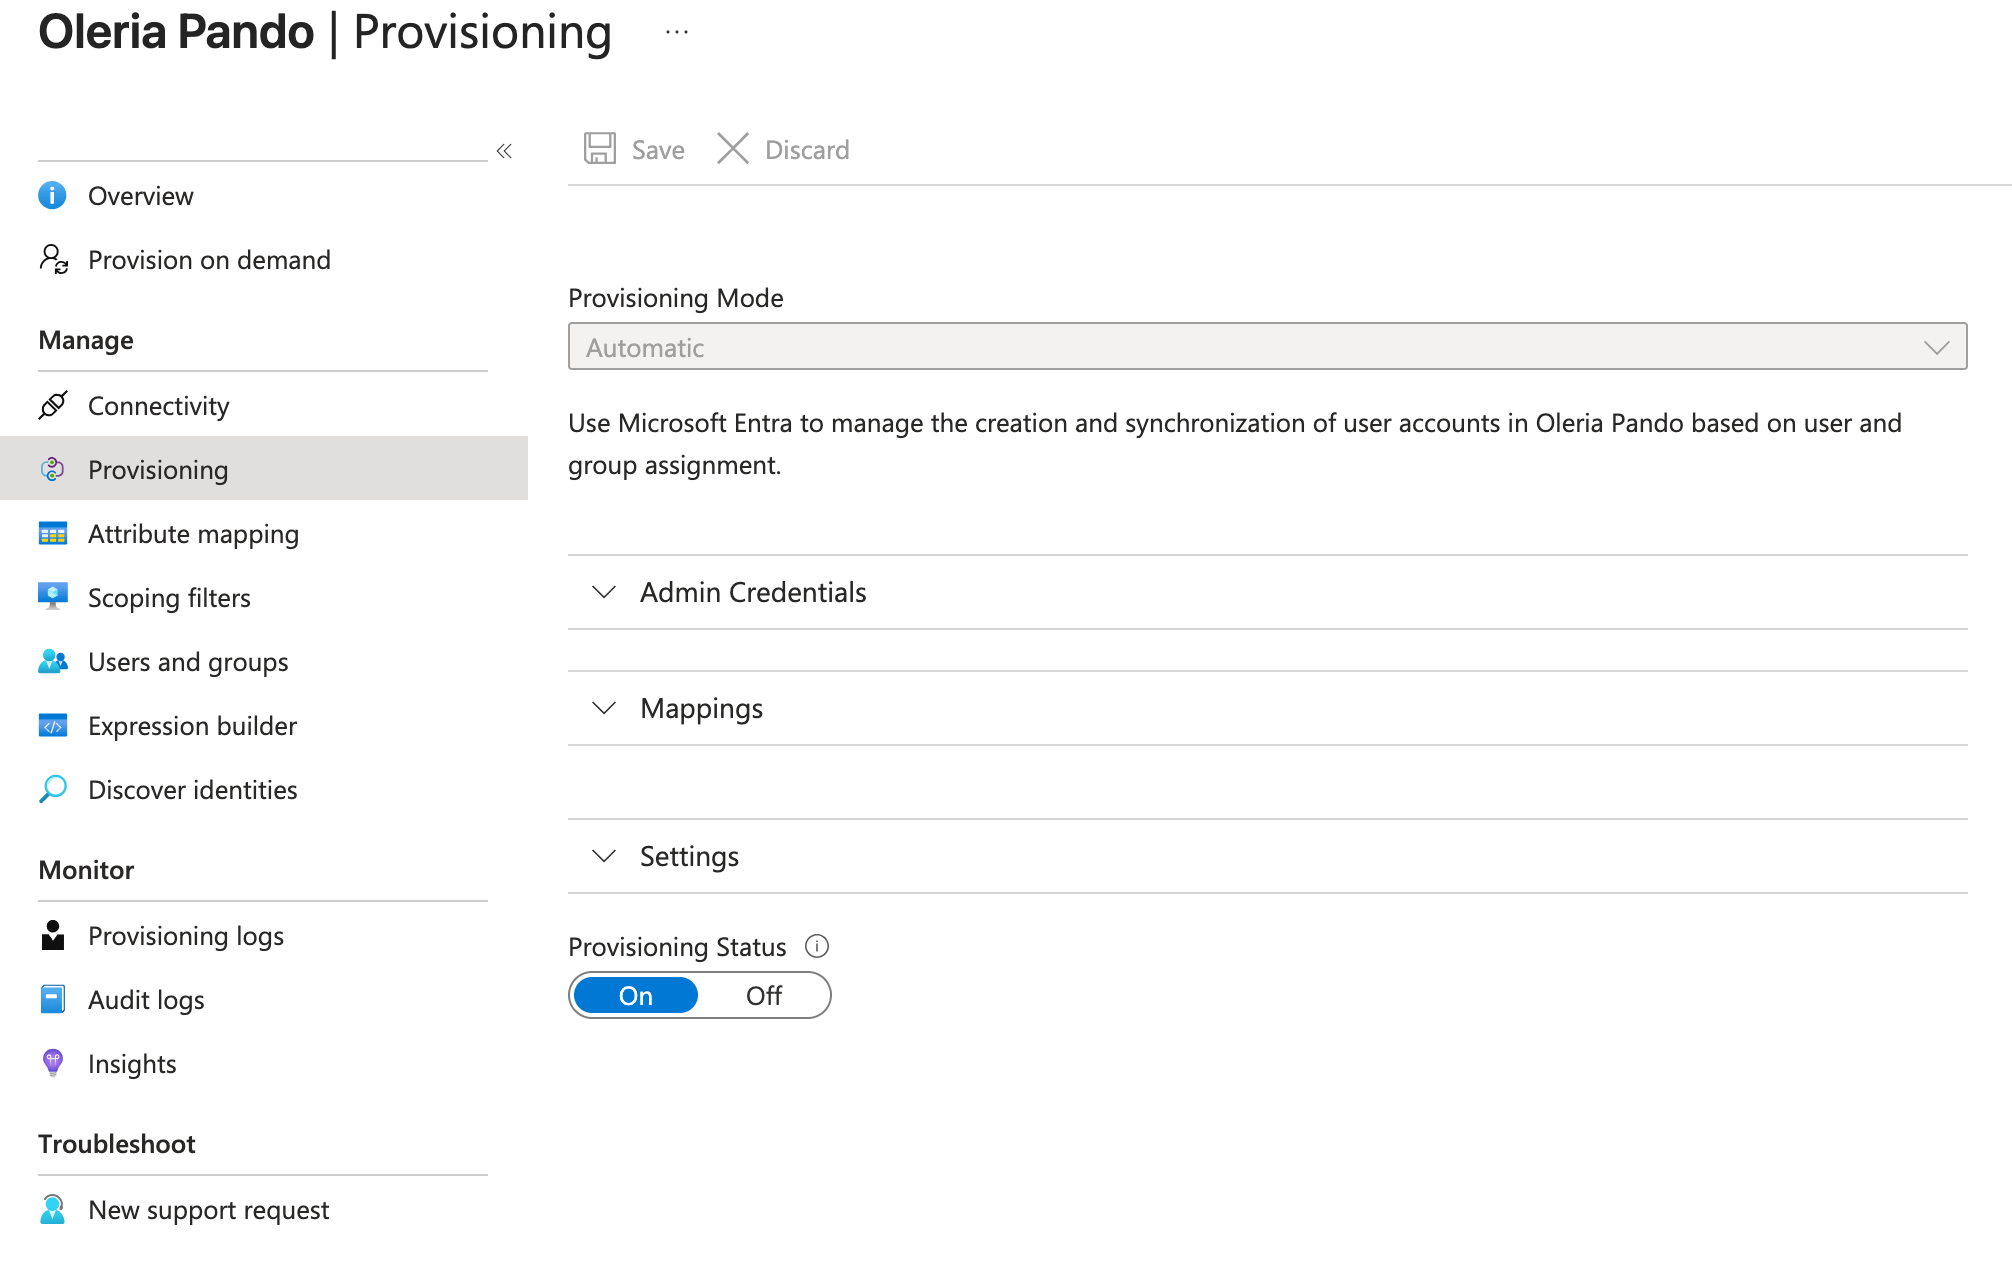
Turn on provisioning
Review the attribute mappings
- Map the same attribute to both
userNameandemails[type eq "work"].value, and make it the same attribute as the SAMLemailclaim from Part 1. Use the expressionCoalesce([mail], [userPrincipalName])for both: it prefersmail(correct for guest accounts, whoseuserPrincipalNameis not a real address) and falls back touserPrincipalNamefor users whosemailis empty. - Confirm that either the name parts or
name.formattedor both are mapped. This should exist by default.
reviewer role automatically. You can turn group provisioning off and provision users only.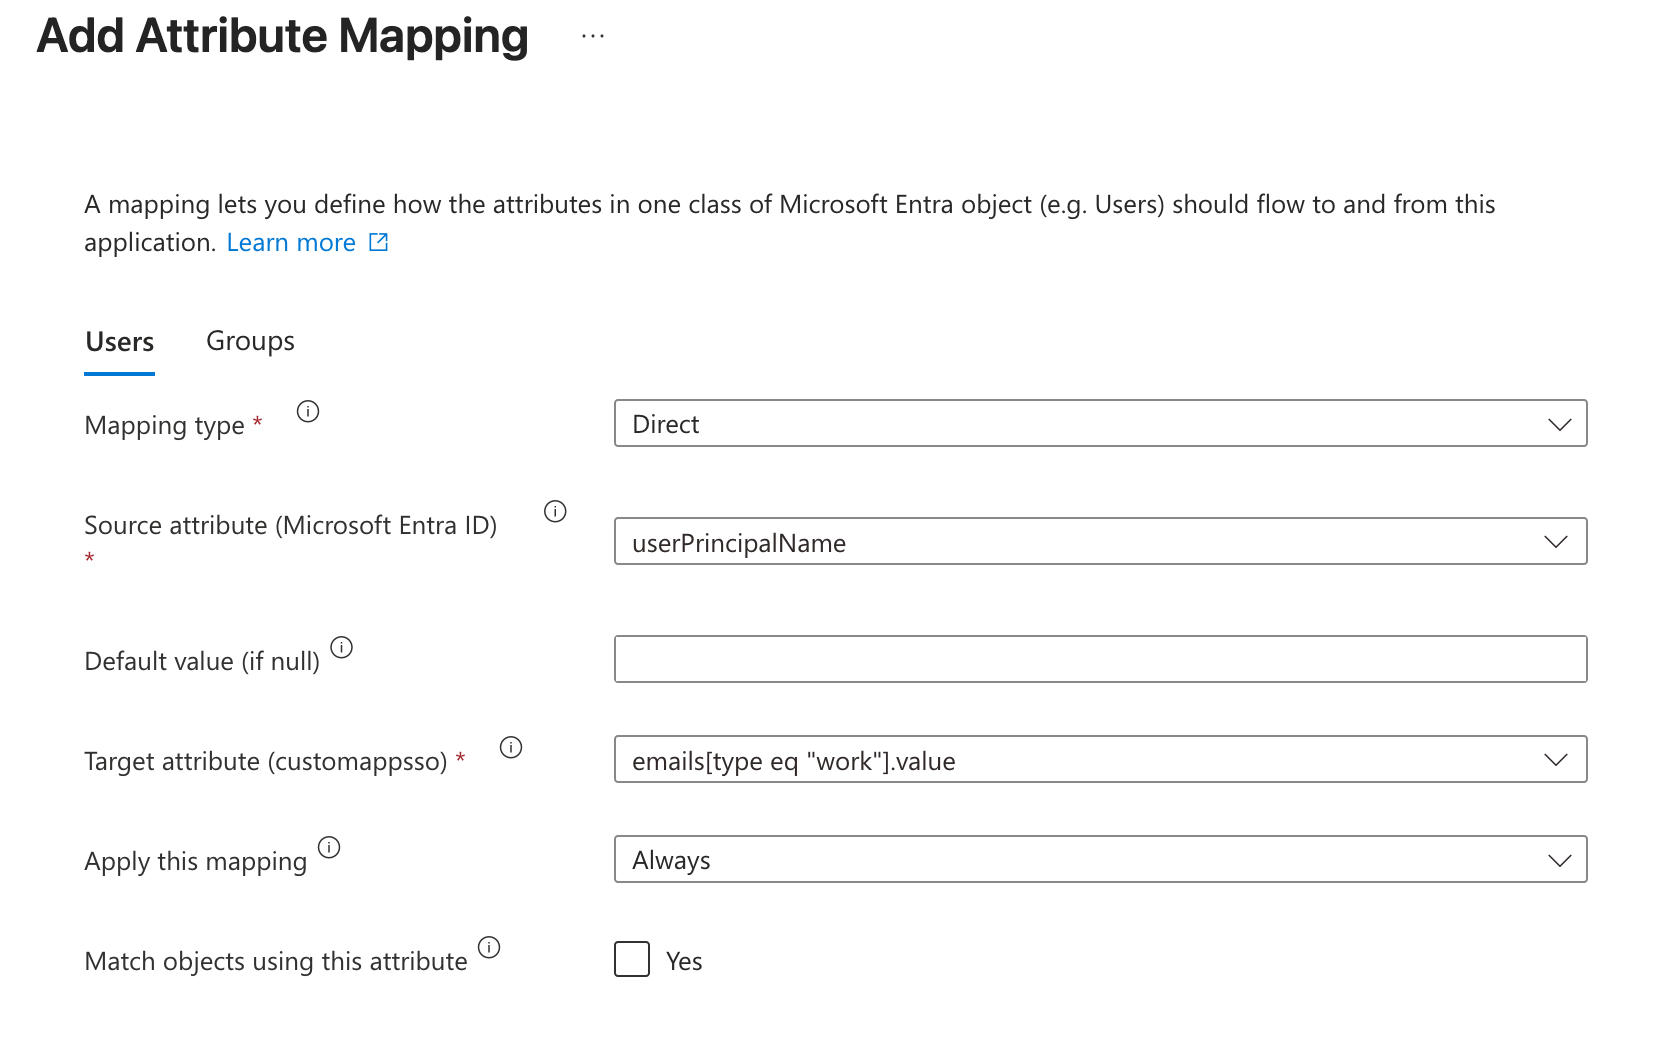
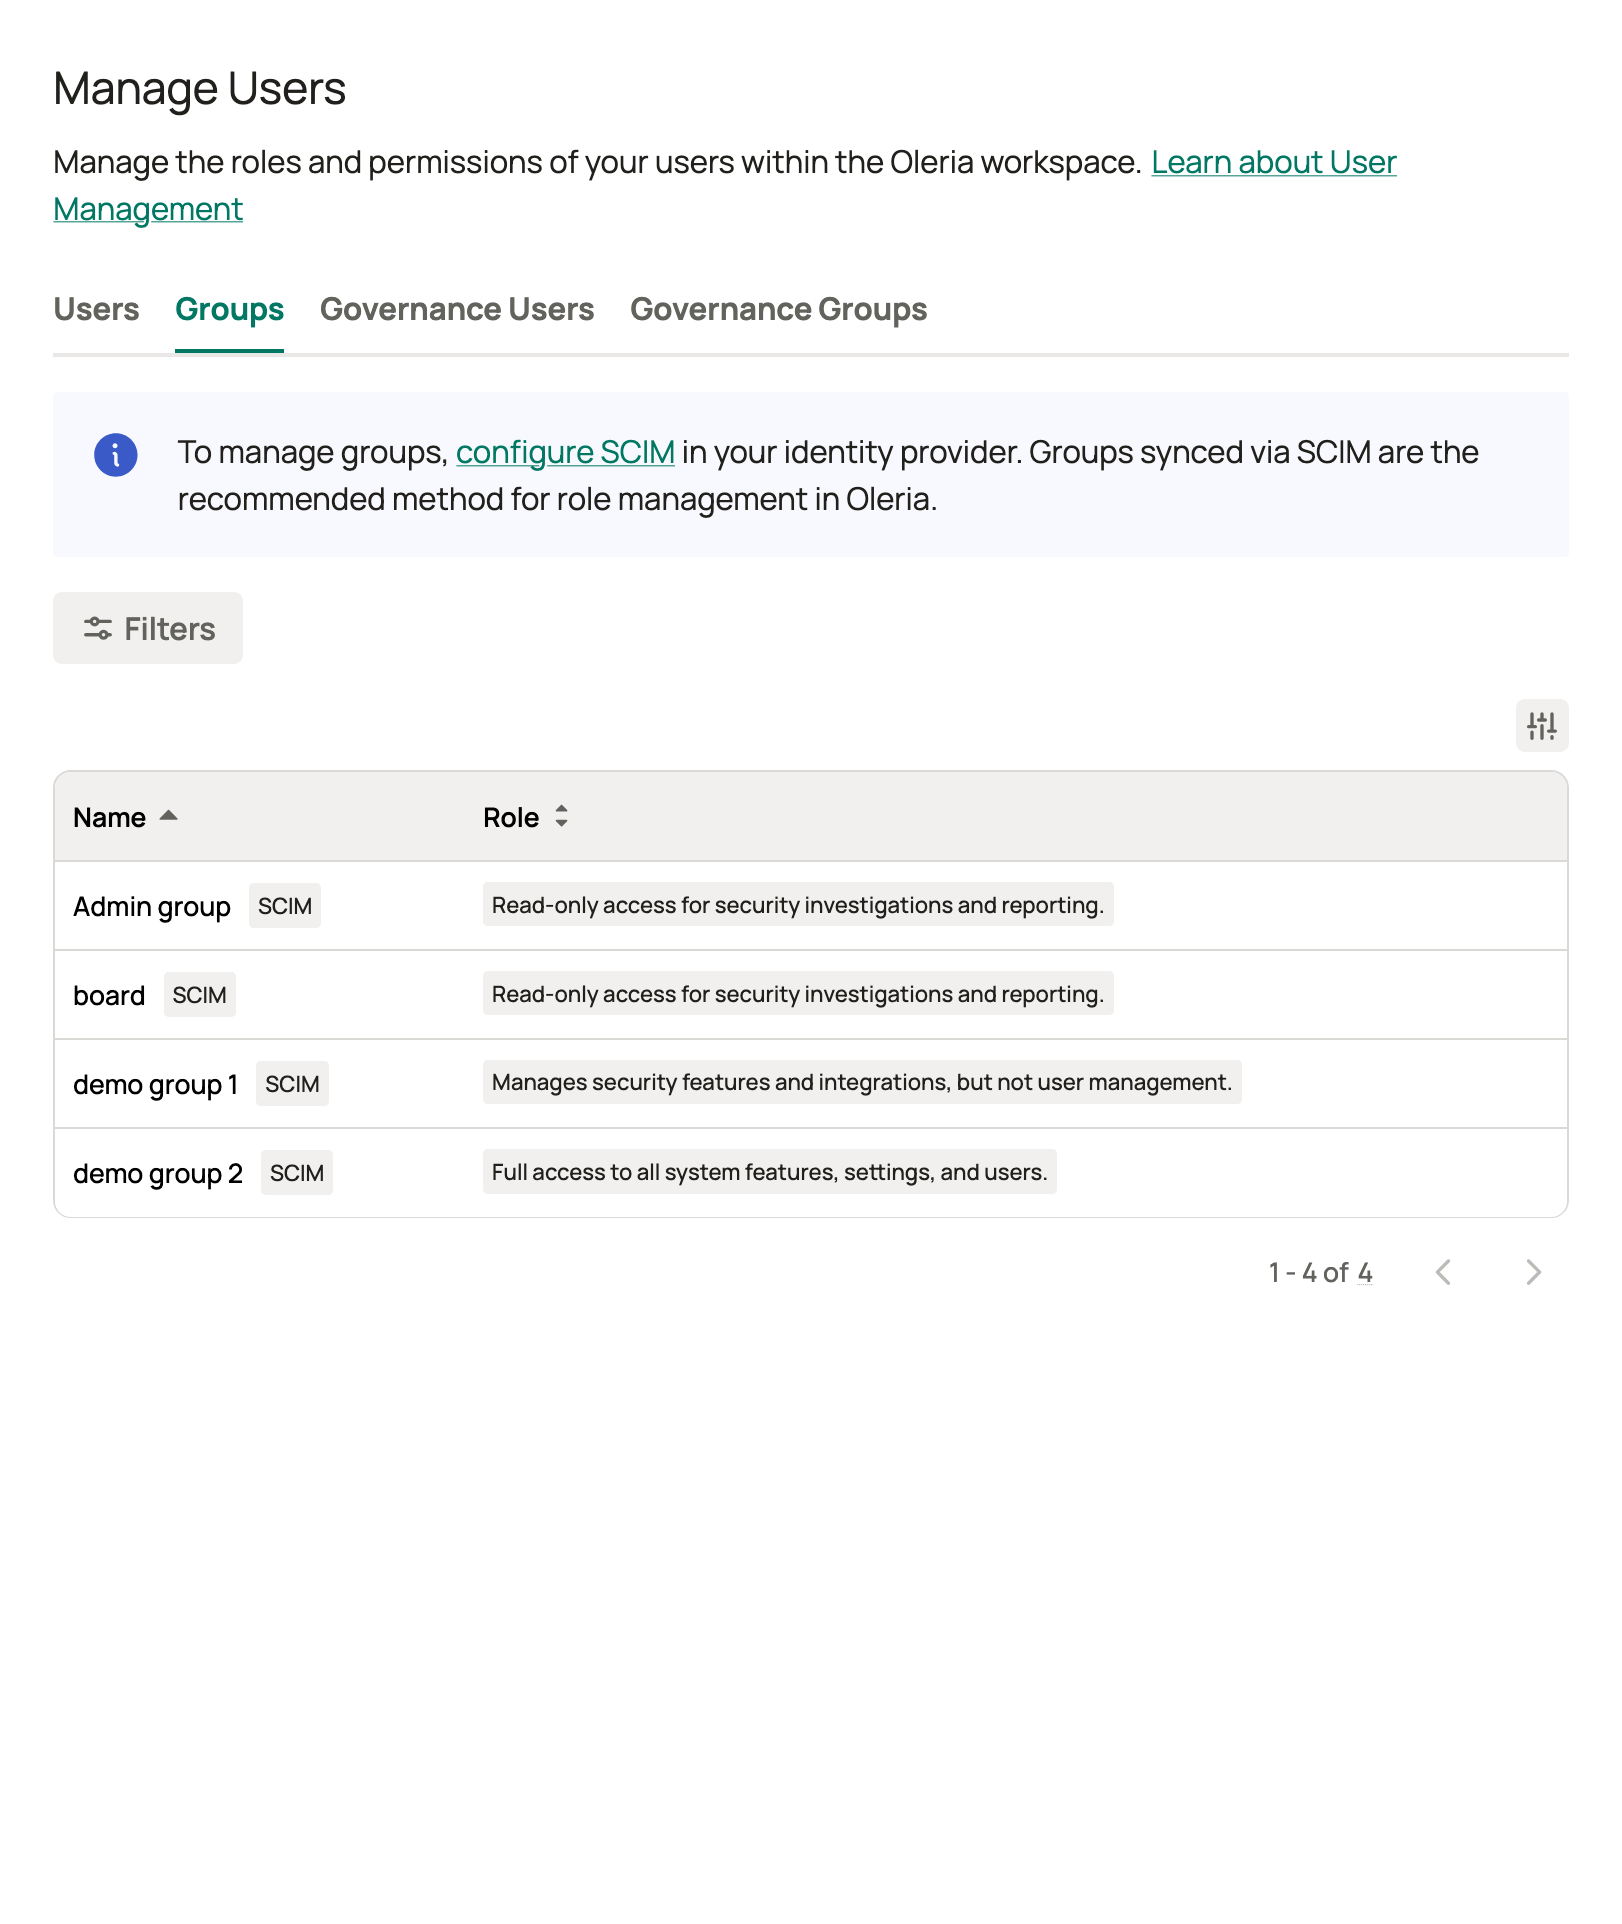
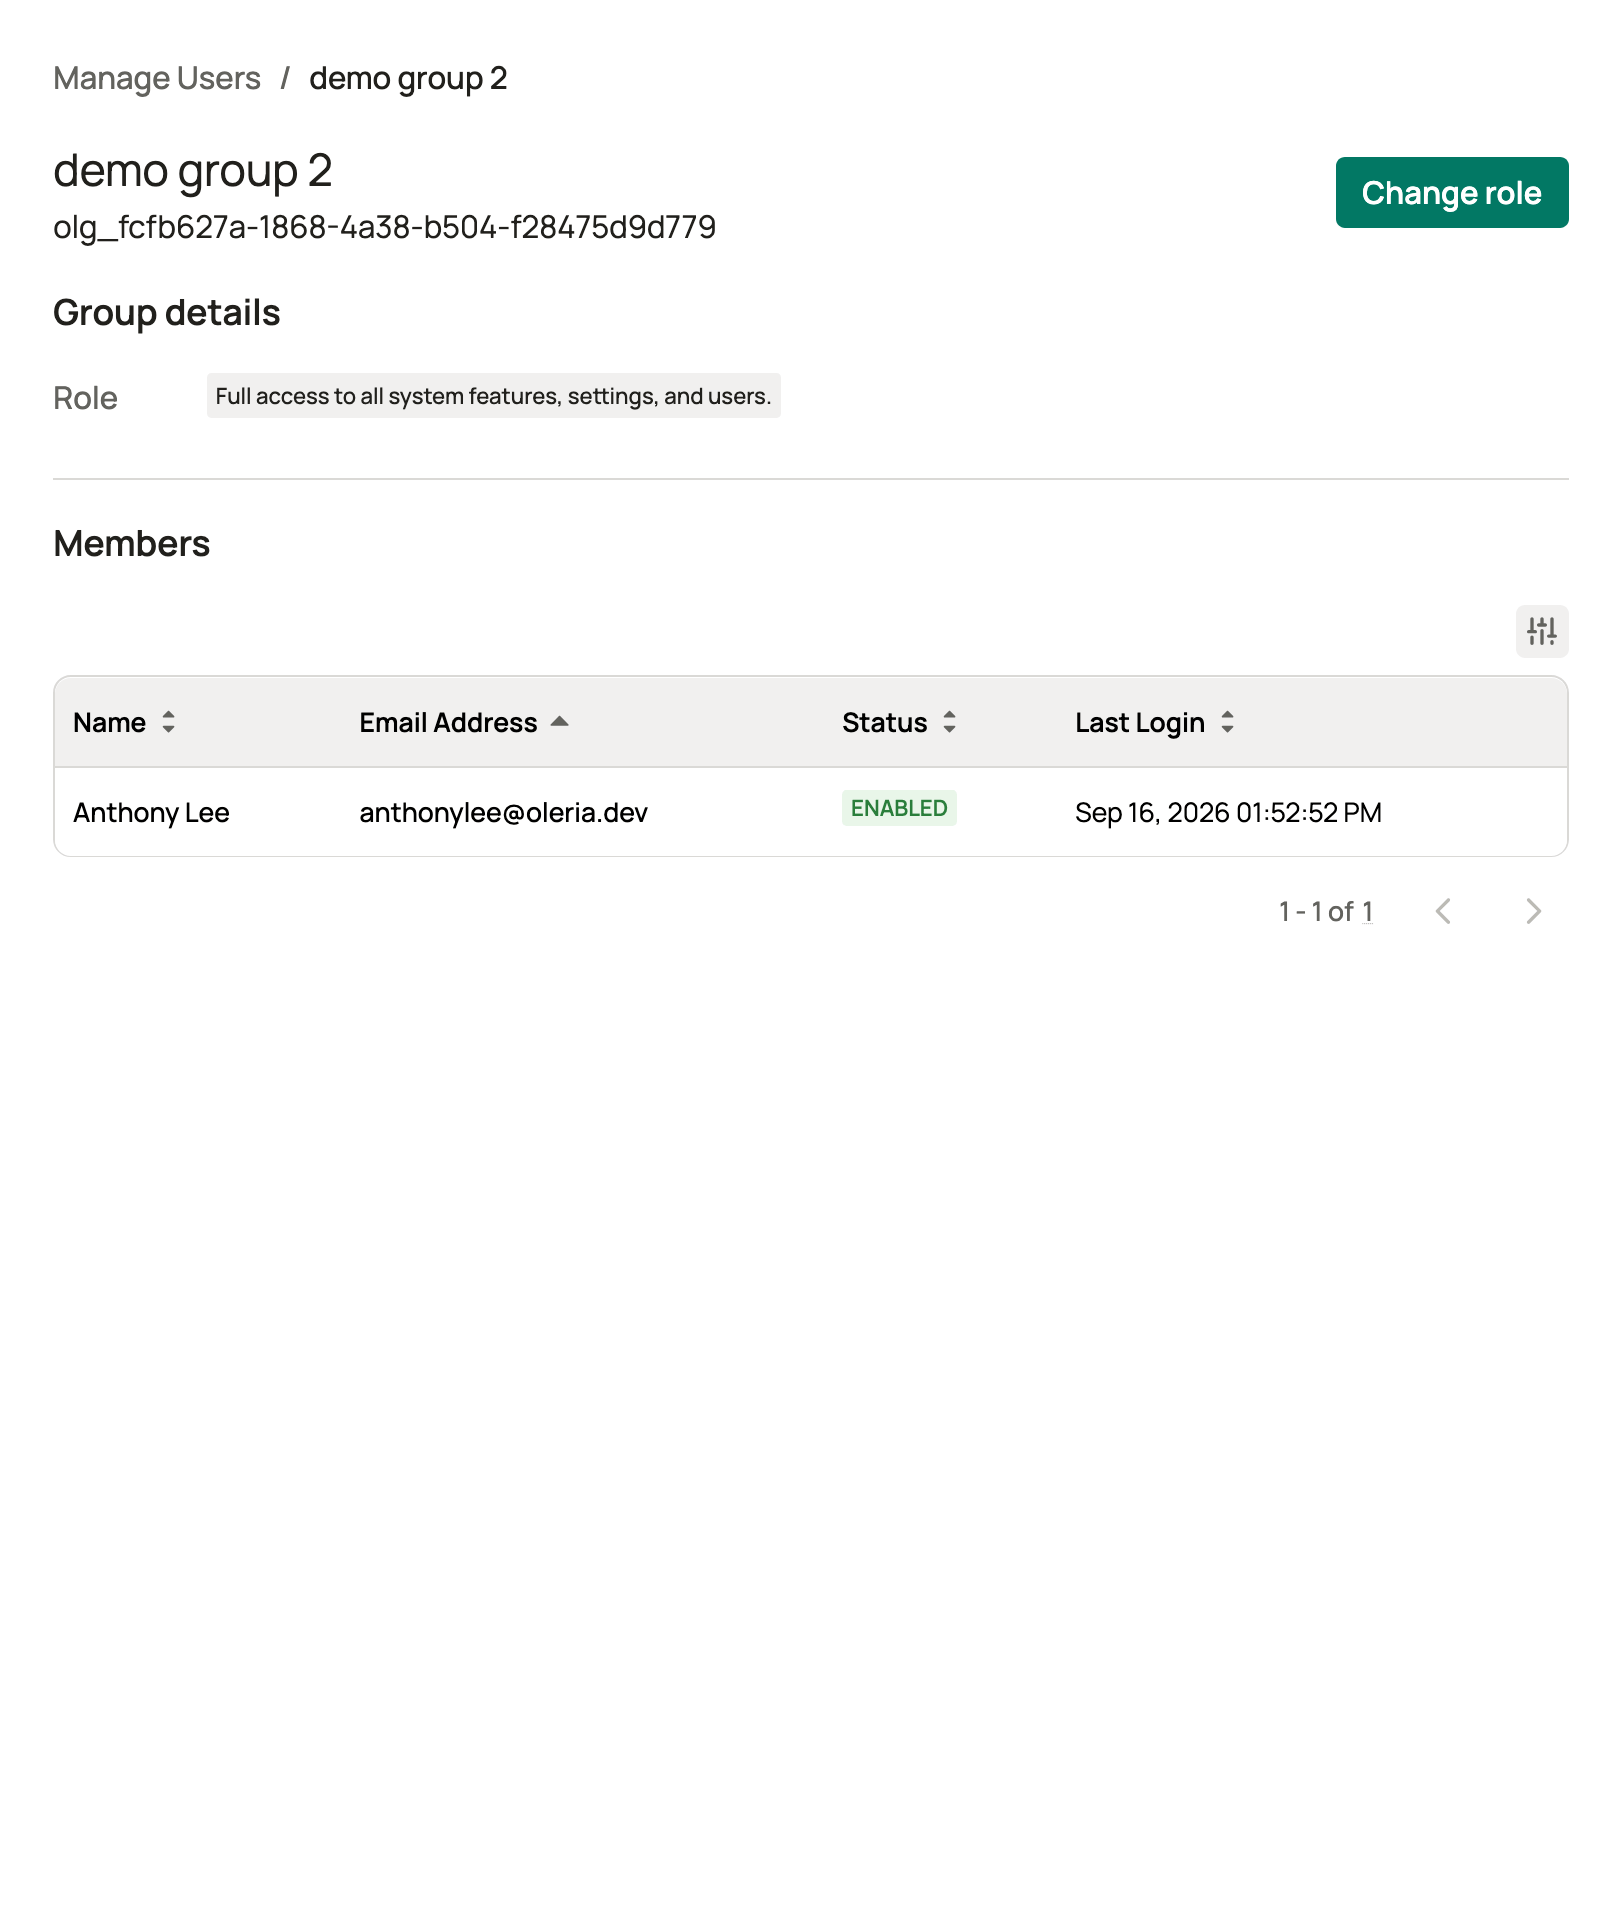
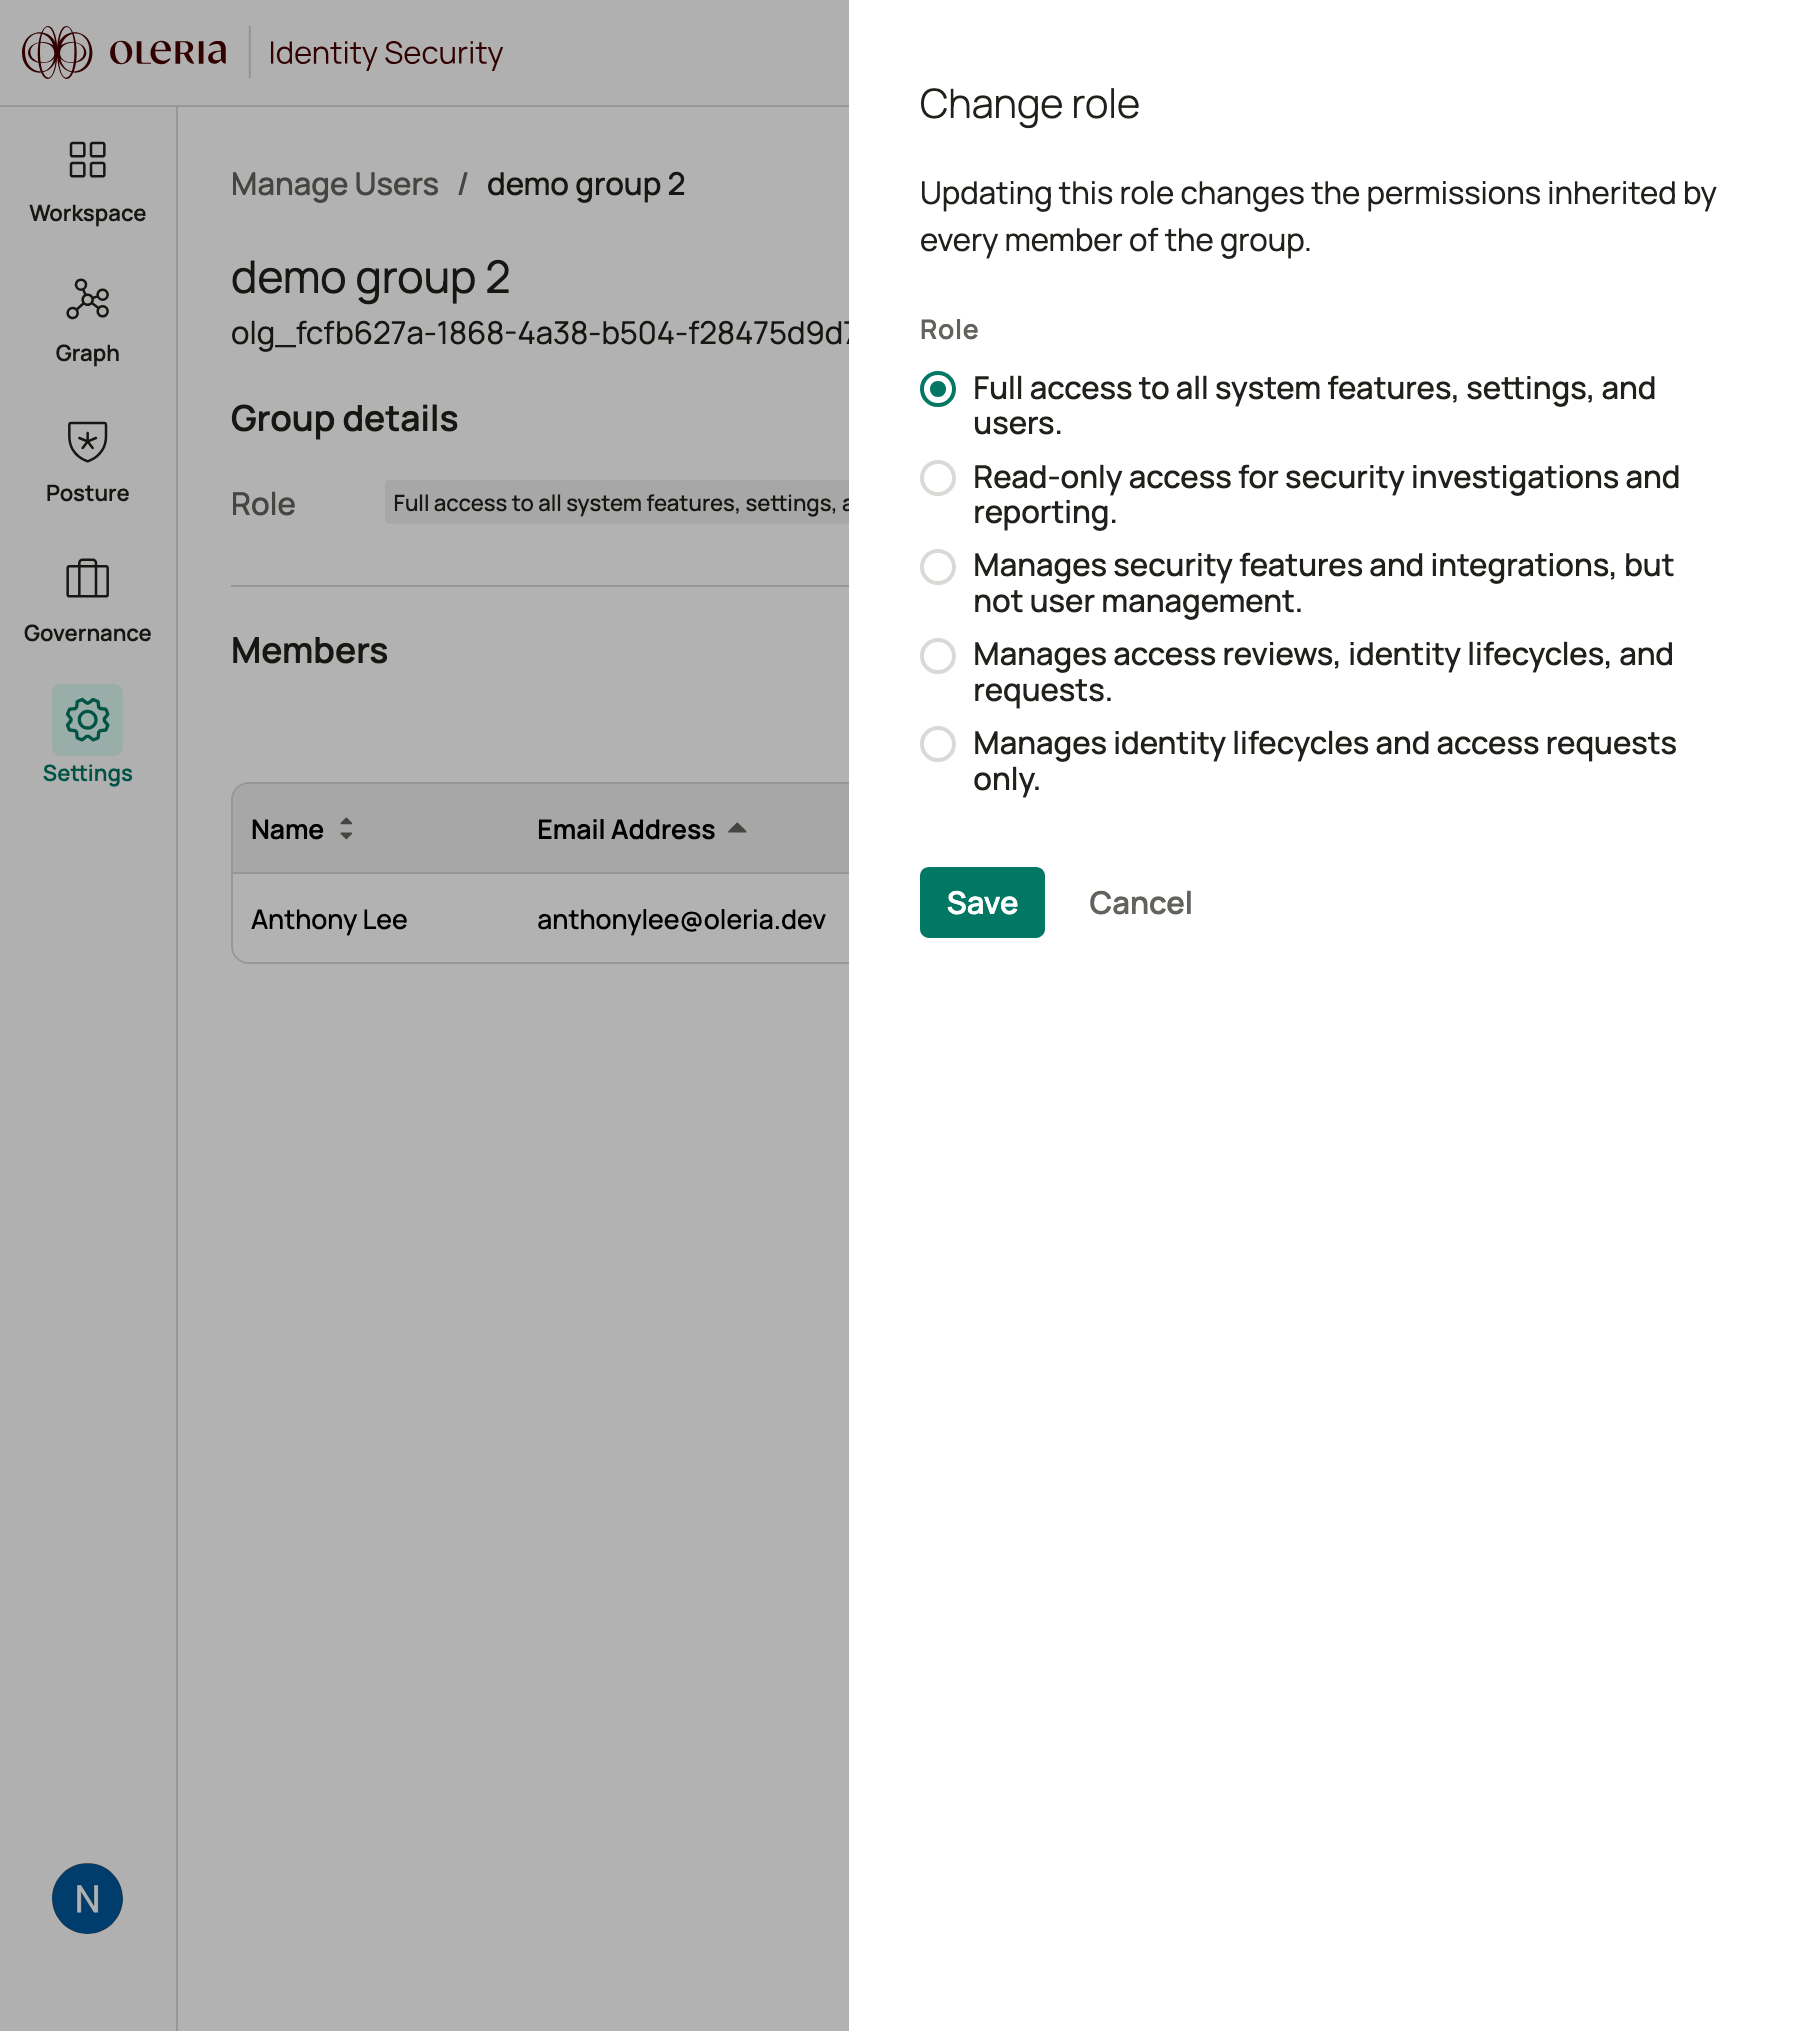
Main Workspace only: assign each group a role in Oleria
Scope and start provisioning
Verify
Alternatives without Entra ID P1
If your tenant is on Entra ID Free and adding P1 isn’t an option, these are the working paths. They’re the same options as the Okta equivalent, since the constraint is on the identity provider side rather than Oleria’s.Set up the second workspace
If you need both workspaces connected to Entra, don’t repeat Part 1 with a new enterprise application - see Entra’s one-app-per-Entity-ID rule above. Instead:- SSO: in Oleria, go to the SSO Configuration page and select the tab for the workspace you have not yet set up. Add an identity provider using the same Entra app’s App Federation Metadata Url from Part 1.
- SCIM: Entra allows only one provisioning job per enterprise application, so you can’t add a second Provisioning configuration to the same app you used for SSO. Create a second Non-gallery application instead, used for provisioning only - leave its Single sign-on section unconfigured entirely. Entra’s Entity ID uniqueness rule only applies to apps with SAML SSO configured, so a provisioning-only app with no SAML section touched never collides with it. Point this second app’s Provisioning details at the other workspace’s SCIM Base URL, OAuth Token URL, Client ID, and Client Secret, following Part 2 again on the new app.
FAQ
Entra and identity provider basics
What is Microsoft Entra ID?
What is Microsoft Entra ID?
What is an identity provider, and what is a service provider?
What is an identity provider, and what is a service provider?
- The user opens Oleria’s sign-in page and selects your identity provider.
- Oleria redirects their browser to Entra, which authenticates them with whatever your tenant requires (password, MFA, conditional access).
- Entra sends the browser back to Oleria’s ACS URL carrying a digitally signed SAML assertion that says who the user is.
- Oleria checks the signature against the certificate in the metadata you gave it, and signs the user in.
What are the Entity ID and ACS URL Oleria gives me?
What are the Entity ID and ACS URL Oleria gives me?
- Entity ID (Entra calls it Identifier) - the unique name of Oleria as a service provider. It’s a name, not a page you can open. Entra uses it to decide which application a given SAML response belongs to, which is why it has to be unique per app. See Entra’s one-app-per-Entity-ID rule.
- ACS URL (Entra calls it Reply URL) - the Assertion Consumer Service URL, the exact address Entra posts the signed assertion to. It has to match character for character.
Where is the Entra admin center, and what is a tenant?
Where is the Entra admin center, and what is a tenant?
contoso.onmicrosoft.com and a tenant ID in the form of a GUID. Everything on this page happens inside one tenant. If your account administers more than one, confirm which directory you’re in before you create the application.What is an enterprise application, and why non-gallery?
What is an enterprise application, and why non-gallery?
What are claims, and what is the NameID?
What are claims, and what is the NameID?
- Unique User Identifier (Name ID) - the user’s primary identifier in the identity provider. Oleria requires the Name ID to use the Persistent format, but doesn’t constrain its value. Use
user.objectid, the GUID Entra assigns each account, rather than an email address or username, both of which change when someone changes their name. emailandname- two extra claims, named exactly that. Entra prefixes new claims with a long namespace URI such ashttp://schemas.xmlsoap.org/ws/2005/05/identity/claims/by default. Clear the Namespace field on both so the claim arrives as plainemailandname, which is what Oleria looks for.
What Entra role do I need to do this?
What Entra role do I need to do this?
How do I tell which Entra license we have?
How do I tell which Entra license we have?
What's the difference between assigning a user and provisioning a user?
What's the difference between assigning a user and provisioning a user?
How often does Entra provisioning run?
How often does Entra provisioning run?
Where does Entra log what happened?
Where does Entra log what happened?
- Sign-in logs, under Entra ID → Monitoring & health → Sign-in logs, for anything about SSO. Filter by Application to your Oleria application. Every failure carries an
AADSTSerror code and a description that is far more specific than what the browser shows the user. - Provisioning logs, on the enterprise application’s provisioning page, for anything about SCIM. They show each user Entra tried to create, update, or disable, and the error Oleria returned if it refused. Provisioning logs require a P1 or P2 license. See Read the provisioning logs.
Does connecting Entra to Oleria change anything in my Entra tenant?
Does connecting Entra to Oleria change anything in my Entra tenant?
Sign-in troubleshooting
Entra says the identifier isn't unique when I create a second application
Entra says the identifier isn't unique when I create a second application
Sign-in fails with AADSTS50105, not assigned to a role for the application
Sign-in fails with AADSTS50105, not assigned to a role for the application
Sign-in fails with AADSTS50011, reply URL mismatch
Sign-in fails with AADSTS50011, reply URL mismatch
http instead of https, and a truncated paste all count as a mismatch. Re-copy the value from Settings → SSO Configuration in Oleria and paste it again, and check the Identifier while you’re there.Microsoft signs the user in, then Oleria rejects them
Microsoft signs the user in, then Oleria rejects them
- Unique User Identifier (Name ID) uses the Persistent format with a stable source attribute such as
user.objectid. - The
emailandnameclaims exist, are spelled exactly that, and have an empty Namespace. - If you turned on Sign requests, Oleria’s request signing certificate is uploaded to Entra under Verification certificates.
- If you turned on Encrypt SAML responses, Oleria’s response encryption certificate is imported and activated on the application’s Token encryption page. An imported but inactive certificate behaves as though you never uploaded it.
The user signs in successfully but has no access to Oleria
The user signs in successfully but has no access to Oleria
- Main Workspace - the account has to come from SCIM or from Manage Users.
- Governance App - the same, unless you turn on automatic user provisioning and add the person’s email domain to the allowed list.
Sign-in worked for months and suddenly stopped
Sign-in worked for months and suddenly stopped
Oleria rejects the identity provider when I add or edit it
Oleria rejects the identity provider when I add or edit it
Start with Provision on demand
Before changing any setting, reproduce the problem against a single user. In the Entra app, go to Provisioning → Provision on demand, select one affected user, and click Provision. Entra runs the full cycle for just that user and returns the result in seconds instead of waiting up to 40 minutes for the next scheduled cycle. The result is shown as four steps, and the one that fails tells you where to look:Read the provisioning logs
Provisioning → Provisioning logs (also under Entra ID → Monitoring → Provisioning logs) records every object Entra processed in every cycle, kept for 30 days. Provisioning logs require Entra ID P1 or P2 - on Entra ID Free there is no way to see why a sync failed, which is why P1 is the practical requirement for SCIM. Filter by Identity (the user’s name or email) or by Status, then open a row to see the same four steps, with the request and response, that Provision on demand shows. Read the Status column first, because the three values point at completely different causes:- Cycles are incremental. After the first full sync, Entra only re-evaluates objects that changed, so a user who failed earlier won’t reappear in later cycles just because you fixed the mapping. Use Restart provisioning (not Save) to clear the watermark and re-evaluate everyone, or Provision on demand for a single user.
- Persistent failures get throttled. After about four weeks of failures Entra quarantines the provisioning job and drops to one attempt per day. The Provisioning page shows the quarantine banner; fix the cause, then Restart provisioning.
403 on Test Connection or in the logs, rather than a 401, usually means the credentials are valid but belong to the other workspace: the Main Workspace and Governance App tabs issue separate credentials, and each is only accepted by its own SCIM base URL.
Provisioning troubleshooting
Test Connection fails in the Provisioning section
Test Connection fails in the Provisioning section
- Authentication method is OAuth2 client credentials grant, not a bearer token. Oleria’s SCIM API only issues short-lived tokens through this exchange.
- Tenant URL is Oleria’s SCIM Base URL, not Oleria’s sign-in address.
- OAuth token endpoint is Oleria’s OAuth Token URL.
- Client identifier and Client secret are pasted whole, with no leading or trailing spaces.
- Credentials are sent by Header, and Scope is empty.
Provisioning is on but nobody appears in Oleria
Provisioning is on but nobody appears in Oleria
- The initial cycle hasn’t finished. Check the cycle status and the provisioning logs before changing anything.
- Scope is Sync only assigned users and groups, but nobody is assigned under Users and groups.
- Provisioning Status was left Off, or the section wasn’t saved.
- The job is in quarantine. Entra pauses a provisioning job after repeated failures and shows a banner saying so. Fix the underlying error, then select Restart provisioning.
Users sync but groups don't (Main Workspace)
Users sync but groups don't (Main Workspace)
- Group provisioning requires a P1 or P2 license even when user provisioning is working. See Entra ID P1 or P2 is required for SCIM.
- Provision Microsoft Entra ID Groups is disabled in the attribute mappings.
- The group itself isn’t assigned to the application. Assigning the members individually syncs the users but never creates the group.
- The group contains other groups. Entra’s provisioning service doesn’t follow nested groups, and skips members that are groups rather than users. Assign the inner groups directly, or flatten them.
Provisioned users have the wrong role, or no access (Main Workspace)
Provisioned users have the wrong role, or no access (Main Workspace)
analyst role.In Oleria, go to Settings → Manage Users, select the Groups tab, select the group, click Change role, and choose the role it should grant. Every current and future member inherits it. See How Oleria maps roles and groups.This doesn’t apply to the Governance App, where every provisioned user gets the reviewer role automatically.Someone I unassigned in Entra still has access to Oleria
Someone I unassigned in Entra still has access to Oleria
Provisioned users have a missing or wrong email address
Provisioned users have a missing or wrong email address
mail attribute to emails[type eq "work"].value, and mail is empty for accounts that have never been given a mailbox. Map userPrincipalName there instead, and to userName, as the attribute mapping step in Part 2 describes. Fix the mapping, then use Provision on demand to re-run one affected user rather than waiting for the next cycle.Provisioning reports duplicate or conflict errors, or provisioned users never update
Provisioning reports duplicate or conflict errors, or provisioned users never update
userName filter. If userName and emails[type eq "work"].value are mapped to different Entra attributes, and those differ for some people, Entra can’t find the account it already created and tries to create it again on every cycle, which Oleria rejects as a duplicate.Map both to the same attribute, using Coalesce([mail], [userPrincipalName]), as the attribute mapping step in Part 2 describes. Then use Provision on demand to re-run one affected user.