> ## Documentation Index
> Fetch the complete documentation index at: https://docs.oleria.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Box
> Connect your Box enterprise to Oleria to continuously discover managed and external users, groups, enterprise roles, folders and who can access them, App Users, AI agents, and admin activity.
Connect Box to Oleria to see who has access across your Box enterprise: managed users, external collaborators, groups, enterprise roles, shared folders and who can access them, App Users and the app's Service Account that act as non-human identities (NHIs), Box AI Studio agents, and admin activity. You create a **Platform App** in the Box Developer Console using **Server Authentication** with Client Credentials Grant, then paste **Client ID**, **Client Secret**, and **Enterprise ID** into Oleria. Oleria authenticates as the app's **Service Account**. This page walks through that setup.
One Oleria connection maps one Box enterprise. Connect additional enterprises as separate instances if you operate more than one.
This integration is for a Box **enterprise** (Business, Business Plus, or Enterprise). It does not apply to a personal Box account. There is no browser consent screen.
## What Oleria discovers
Once connected, Oleria continuously discovers and maps the following from the Box enterprise:
* **Accounts** - managed users and external collaborators, including login, name, status (active or inactive), enterprise role, last login, confirmed alternate email, and the multi-factor authentication (MFA) exemption flag. When at least one discovered folder has an open shared link, Oleria also includes **Anyone with the link**.
* **Roles** - **Enterprise Admin**, **Enterprise Co-Admin**, and **Enterprise User**.
* **User groups** - enterprise groups, including the built-in all-users group, and their membership.
* **Resources** - the enterprise root folder (**All Files**), plus every folder that is shared directly (a collaboration added on that folder) or has a shared link. The root folder always appears, even with no sharing, as the starting point for the folder tree. Folders that only inherit sharing from a parent folder, and folders with no sharing, are used only to reach shared folders and do not appear as resources.
* **Access** - who can reach which folder:
* users collaborating directly on a folder, with their permission level (for example Editor or Viewer)
* groups collaborating directly on a folder, with their permission level
* **Non-human identities (NHIs)** - Box **App Users**, the machine accounts Platform Apps use to act on the enterprise, and the Platform App's own **Service Account**, which Oleria uses to connect.
* **AI agents** - Box AI Studio agents, including whether each agent is enabled, when your Box plan includes AI Studio and the Platform App can read agents. Otherwise Oleria skips agents without failing the sync.
* **Activity** - Box admin events such as logins, user status and role changes, new users, group membership changes, folder collaboration and sharing changes, shared-link changes, new apps, revoked app tokens, and MFA enabled, disabled, or verified. Activity requires report access, see [Prerequisites](#prerequisites).
Folder permission levels such as Editor, Viewer, and Uploader appear on folder access, not under **Roles**. Only Enterprise Admin, Enterprise Co-Admin, and Enterprise User appear under **Roles**. Box does not expose per-user MFA enrollment beyond the exemption flag, or single sign-on (SSO) enforcement, so Oleria reports those as unavailable rather than inferring them. MFA changes still appear in **Activity**.
Standard integrations are configured read-only. Remediation uses the same Platform App with write access, and is opt-in. See [Remediation actions](#remediation-actions) below.
## Prerequisites
* A Box enterprise you want Oleria to inventory (not a personal account).
* Admin or co-admin access to the Box **Developer Console** and **Admin Console**.
* A **Platform App** with **Server Authentication** (Client Credentials Grant), authorized for the enterprise.
* App Access Level set to **App + Enterprise Access**, so the Service Account can see managed users, not only its own App Users.
* Application scopes **Read and write all files and folders**, **Manage users**, **Manage groups**, and **Manage enterprise properties**. These cover discovery and every remediation action. Add **Manage AI** if you want AI agents and your Box plan includes AI Studio.
* An admin or co-admin who can **Run new reports and access existing reports**, if you want Activity. Without this, Oleria still connects and syncs accounts, groups, roles, and folders. Activity is skipped rather than failing the connection.
After you create or change the Platform App, authorize it in the Admin Console (**Apps** -> **Platform Apps Manager** -> **Server Authentication Apps**). Box does not let an unauthorized app authenticate.
## Create a Platform App in Box
Oleria connects as the **Service Account** Box creates for the Platform App, not as an employee's login.
Sign in to Box and open the [Developer Console](https://app.box.com/developers/console). Select **Create New App**, choose a **Platform App**, and set authentication to **Server Authentication** with Client Credentials Grant.
On the **Configuration** tab:
* Set **App Access Level** to **App + Enterprise Access**.
* Grant the application scopes in [Prerequisites](#prerequisites).
* Copy **Client ID** and **Client Secret** from **OAuth 2.0 Credentials**. Copy **Enterprise ID** from **General Settings**.
Viewing the Client Secret in Box requires two-factor authentication on your Box account. Copy the secret immediately and store it securely.
On the **Authorization** tab, submit the app for admin approval if you are not an admin. In the Admin Console, open **Apps** -> **Platform Apps Manager** -> **Server Authentication Apps** and authorize the app for your enterprise.
## Connect Box to Oleria
Go to your Oleria workspace, select **Integrations** -> select **Box**.
Fill in the connection form:
| Field | Notes |
| :------------ | :-------------------------------------------------------- |
| Client ID | Required. From the Platform App **Configuration** tab. |
| Client Secret | Required. From the Platform App **Configuration** tab. |
| Enterprise ID | Required. From the Platform App **General Settings** tab. |
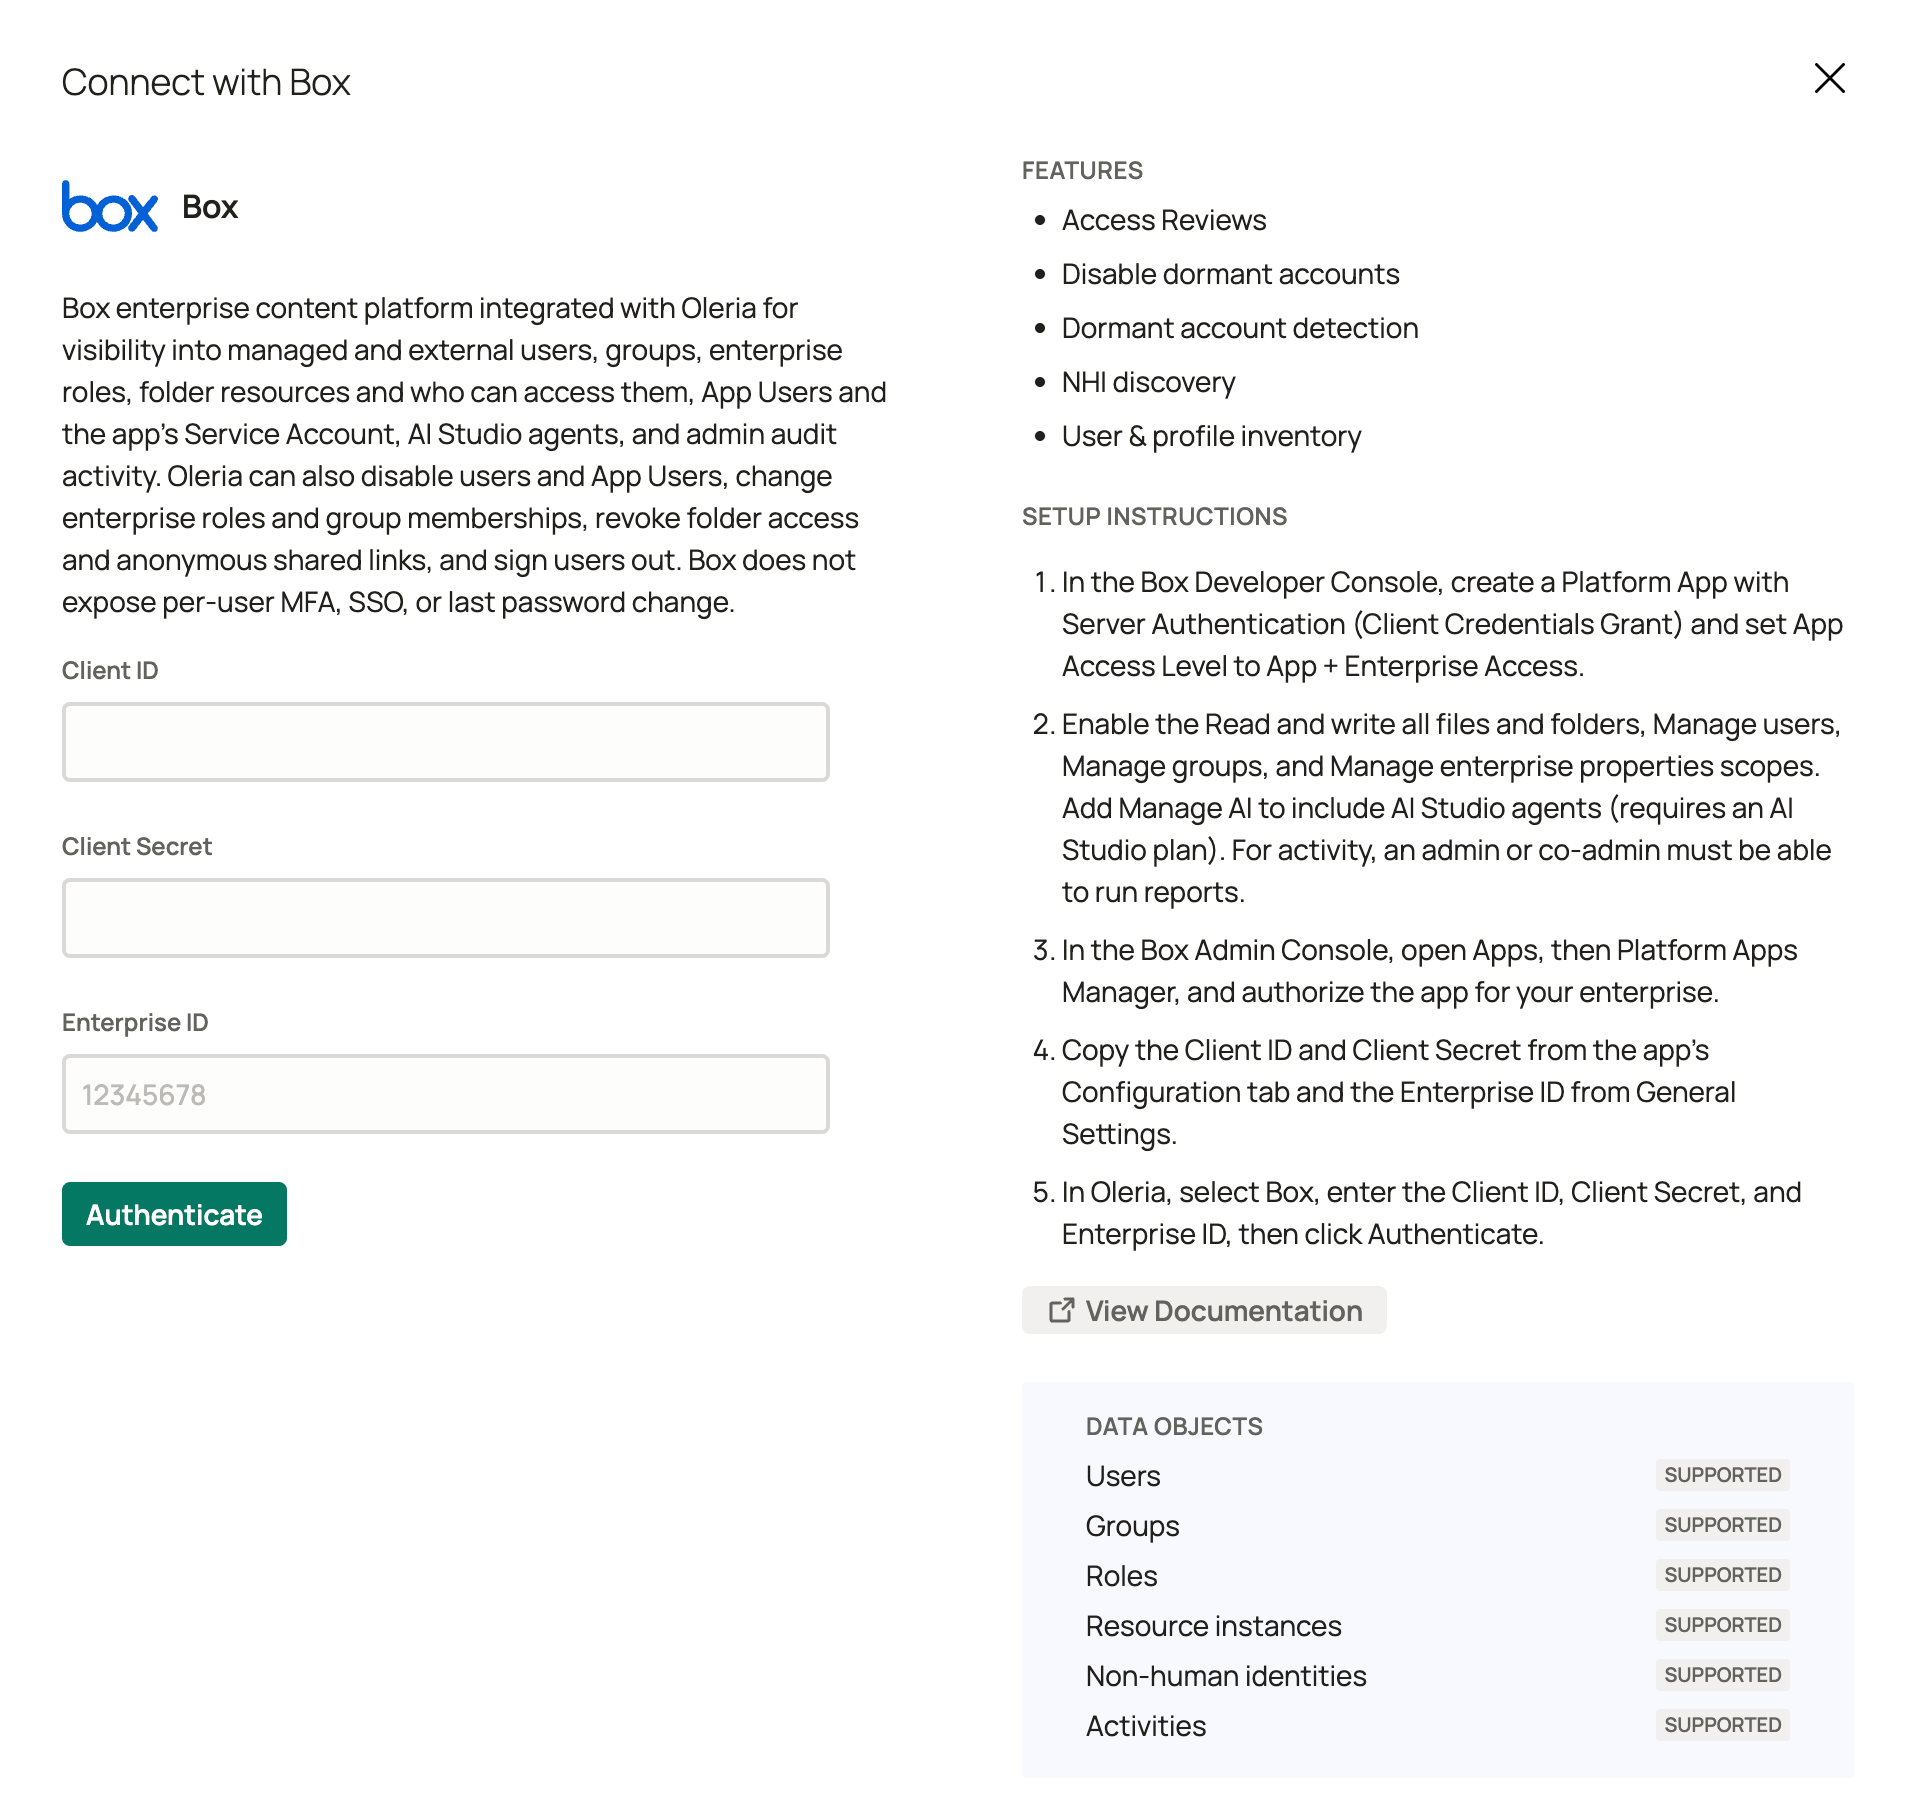 Select **Authenticate**. Oleria validates the credentials against Box before saving.
## Verify the integration
Confirm the Box instance appears in your Oleria workspace's connected integrations. After the first sync completes, you can review the discovered accounts, roles, groups, folders, folder access, NHIs, and AI agents in **Access Inventory**. Activity backfills afterward if the Service Account can run reports.
If you rotate the Client Secret in Box, or an admin revokes the app, reauthorize the app in the Admin Console if needed, then edit the integration in Oleria, paste the new secret, and select **Update**.
Folder discovery starts at the enterprise root and walks the folder tree. The first sync on a very large enterprise can take longer than other object types.
## Remediation actions
Standard integrations are configured read-only. If you enable remediation for Box, Oleria uses the same Platform App. Grant the scopes in [Prerequisites](#prerequisites) on that app.
| Action | What it does | Revert |
| :----------------------------------- | :------------------------------------------------------------------------------------------------------------------------------- | :---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Disable User Account | Sets a managed user's status to inactive. | Supported - restores the previous status. |
| Enable User Account | Sets a managed user's status to active. | Supported - restores the previous status. |
| Grant Co-Admin Enterprise Role | Promotes a managed user to Enterprise Co-Admin. App Users cannot be Co-Admins. | Supported - restores the previous role. |
| Remove Co-Admin Enterprise Role | Demotes an Enterprise Co-Admin to Enterprise User. | Supported - restores Enterprise Co-Admin. |
| Add User to Group | Adds a user to a Box group. If the user is already a member, nothing changes. | Supported - removes them. Box does not restore custom per-membership permissions on a later re-add. |
| Remove User from Group | Removes a user from a Box group. | Supported - re-adds them. Same membership-permission caveat. |
| Revoke Folder Access (Collaboration) | Removes a user or group collaboration added directly on a folder. | Supported - recreates the collaboration with the permission level captured when the action ran. A Co-owner comes back as Viewer. Granting folder access is not a standalone action. |
| Disable App User | Sets an App User (NHI) to inactive. Only App Users can be disabled with this action, not people or the Service Account. | Supported - restores the previous status. |
| Revoke Anonymous Folder Access | Changes an open shared link on a folder to **People in this folder**, so only collaborators can use it. The link itself is kept. | Supported - restores the previous link access. |
| Sign Out User | Ends the user's active Box sessions, so they must sign in again. | Not supported - the user signs in again to start a new session. |
Oleria does not remove a user from the Box enterprise. Box would convert that account to a free personal Box account, which is not reliably reversible. The Enterprise Admin role cannot be granted or removed through Oleria.
## What this integration does not cover
* **Inherited folder access** - access a folder inherits from a parent folder is shown on the parent folder only.
* **Anyone with the link on specific folders** - **Anyone with the link** appears as an account, but not as access on each open-link folder.
* **Folder hierarchy** - parent and child folder relationships are not shown.
* **Folder permission levels as roles** - Editor, Viewer, Uploader, and similar levels appear on folder access, not under **Roles**.
* **Files** - Oleria inventories folders, not individual files.
* **SSO and per-user MFA** - Box does not expose these for this integration, except the MFA exemption flag on accounts.
* **Box Sign, Box Shield, Box Relay, and other add-on products** - not covered.
## Contact us
For questions about this integration, contact us at [support@oleria.com](mailto:support@oleria.com).